Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Ukraine Warns of CABINETRAT Backdoor + XLL Add-ins Spread via Signal ZIPs

Ukraine Warns of CABINETRAT Backdoor + XLL Add-ins Spread via Signal ZIPs

Posted on October 1, 2025October 1, 2025 By CWS

Oct 01, 2025Ravie LakshmananMalware / Incident Response
The Laptop Emergency Response Crew of Ukraine (CERT-UA) has warned of latest focused cyber assaults within the nation utilizing a backdoor referred to as CABINETRAT.
The exercise, noticed in September 2025, has been attributed to a menace cluster it tracks as UAC-0245. The company stated it noticed the assault following the invention of software program instruments taking the type of XLL information, which seek advice from Microsoft Excel add-ins which might be usually used to increase the performance of Excel with customized features.
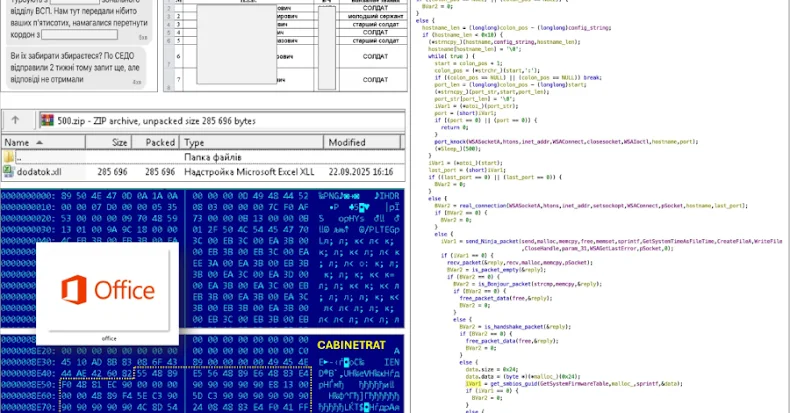
Additional investigation has uncovered that the XLL information are distributed inside ZIP archives shared on the Sign messaging app, disguised as a doc regarding the detention of people who had tried to cross the Ukrainian border.

The XLL, as soon as launched, is designed to create plenty of executables on the compromised host, particularly an EXE file within the Startup folder, an XLL file named “BasicExcelMath.xll” within the “%APPDATApercentMicrosoftExcelXLSTART” listing, and a PNG picture named “Workplace.png.”
Home windows Registry modifications are completed to make sure persistence of the executable, after which it launches the Excel software (“excel.exe”) with the “/e” (“/embed”) parameter in hidden mode in an effort to in the end run the XLL add-in. The primary function of the XLL is to parse and extract from the PNG file shellcode that is labeled as CABINETRAT.
Each the XLL payload and the shellcode include plenty of anti-VM and anti-analysis procedures to evade detection, together with checking for at the least two processor cores and at the least 3GB of RAM, and the presence of instruments like VMware, VirtualBox, Xen, QEMU, Parallels, and Hyper-V.
A full-fledged backdoor written within the C programming language, CABINETRAT is especially designed to assemble system data, an inventory of put in packages, screenshots, in addition to enumerate listing contents, deleting particular information or directories, operating instructions, and finishing up file uploads/downloads. It communicates with a distant server over a TCP connection.
The disclosure comes days after Fortinet FortiGuard Labs warned of assaults concentrating on Ukraine by impersonating the Nationwide Police of Ukraine in a fileless phishing marketing campaign that delivers Amatera Stealer and PureMiner for harvesting delicate information and mining cryptocurrency from focused methods.

The Hacker News Tags:Addins, Backdoor, CABINETRAT, Signal, Spread, Ukraine, Warns, XLL, ZIPs

Post navigation

Previous Post: OpenSSL Vulnerabilities Let Attackers Execute Malicious Code and Recover Private Key Remotely
Next Post: 48+ Cisco Firewalls Vulnerable to Actively Exploited 0-Day Vulnerability in the Wild

Related Posts

Passkey Phishing Exploits Target Microsoft Cloud Accounts Passkey Phishing Exploits Target Microsoft Cloud Accounts The Hacker News
Malicious PyPI Package Impersonates SymPy, Deploys XMRig Miner on Linux Hosts Malicious PyPI Package Impersonates SymPy, Deploys XMRig Miner on Linux Hosts The Hacker News
Zbtlink Routers Expose Security Flaw with Built-in Backdoor Zbtlink Routers Expose Security Flaw with Built-in Backdoor The Hacker News
Agentjacking Attack Exploits AI Coding Agents Agentjacking Attack Exploits AI Coding Agents The Hacker News
Microsoft 365 Flaw Risked Email and File Theft Microsoft 365 Flaw Risked Email and File Theft The Hacker News
CISA Flags Adobe AEM Flaw with Perfect 10.0 Score — Already Under Active Attack CISA Flags Adobe AEM Flaw with Perfect 10.0 Score — Already Under Active Attack The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Microsoft SharePoint Vulnerability CVE-2026-65660 Under Attack
  • Unpatched Citrix NetScaler Flaws Pose Security Threat
  • Citrix Faces Critical NetScaler RCE Vulnerabilities
  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Microsoft SharePoint Vulnerability CVE-2026-65660 Under Attack
  • Unpatched Citrix NetScaler Flaws Pose Security Threat
  • Citrix Faces Critical NetScaler RCE Vulnerabilities
  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark