A complicated ClickFix marketing campaign dubbed “JackFix” that makes use of faux grownup web sites to hijack screens with life like Home windows Replace prompts, tricking customers into operating multistage malware payloads.
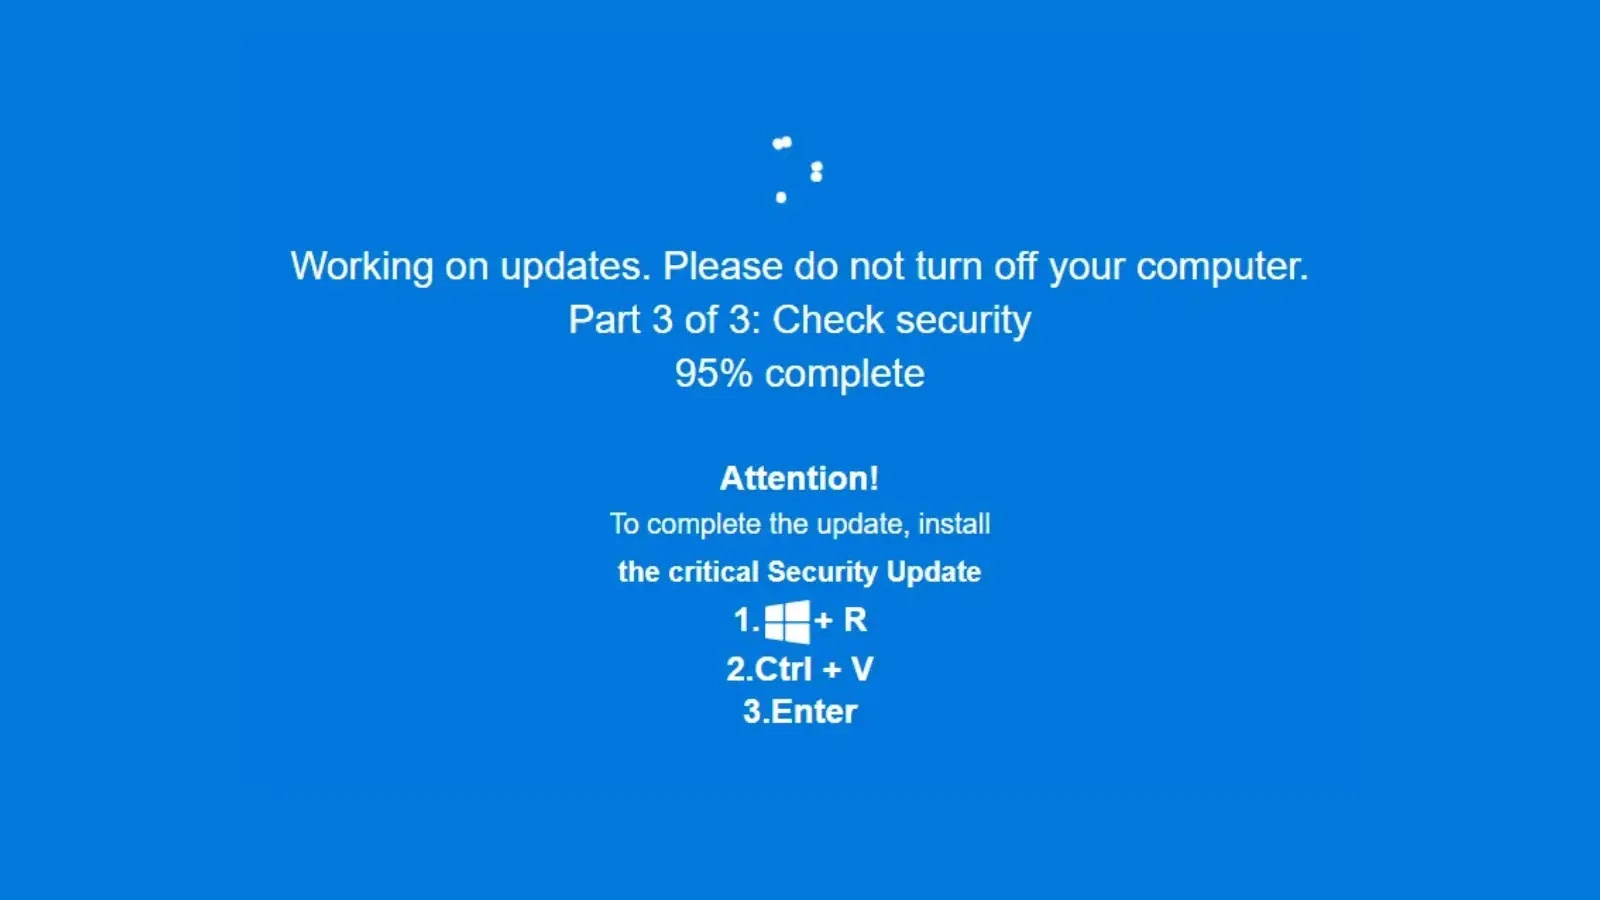
Attackers mimic in style grownup websites like xHamster clones to lure victims, doubtless by way of malvertising on shady platforms. Interplay with the phishing web page triggers a full-screen overlay resembling a crucial Home windows safety replace, full with animations, progress bars, and blue-screen styling.
faux Home windows replace display screen
This “display screen hijacking” combines urgency from the replace theme with embarrassment from grownup content material, pressuring hasty compliance.
The assault’s entry level typically entails faux grownup web sites, equivalent to clones of in style platforms like xHamster and PornHub, that are doubtless promoted by malvertising.
As soon as a consumer interacts with certainly one of these websites, the “JackFix” assault is triggered. The browser is pressured into full-screen mode, displaying a convincing “Essential Home windows Safety Updates” display screen, full with animations and progress counters.
Faux Jakefix Assault
JackFix Assault Leverages Home windows Updates
This screen-locking approach, harking back to older screen-locker malware, pressures the sufferer into following on-screen directions to resolve a fabricated safety subject.
The faux interface disables customary escape keys like Escape and F11, although not totally successfully in examined browsers. This methodology preys on a consumer’s sense of urgency and familiarity to compromise their techniques.
The menace actors have applied a number of superior strategies to evade detection. The marketing campaign not solely obfuscates its malware payloads but in addition the very instructions used to provoke the ClickFix assault, permitting it to bypass many present prevention instruments.
Moreover, the malicious URLs used within the assault make use of a intelligent redirection technique. If accessed instantly, they redirect to benign websites like Google or Steam, however they ship the malicious payload solely when accessed by way of particular PowerShell instructions.
powers
This tactic helps the attacker’s infrastructure keep away from being flagged as malicious by safety evaluation instruments like VirusTotal.
As soon as the sufferer is tricked into operating the preliminary instructions, a multistage assault chain is initiated. The method begins with mshta, which ends up in a PowerShell downloader.
This second-stage script bombards the consumer with Person Account Management (UAC) prompts, successfully rendering the machine unusable till administrative privileges are granted. After gaining elevated entry, the script proceeds to deploy a staggering variety of malware samples concurrently.
In what researchers describe as a “spray and prey” technique, a single an infection can execute eight totally different malware variants. The deployed malware contains the most recent variations of potent info-stealers like Rhadamanthys, Vidar 2.0, and RedLine, in addition to the Amadey botnet shopper and varied loaders and Distant Entry Trojans (RATs).
This large deployment ensures that even when some payloads are blocked, others are prone to succeed, posing a extreme threat of knowledge theft, together with passwords and cryptocurrency wallets.
The researchers famous that this distinctive mixture of psychological manipulation, superior obfuscation, and multi-payload supply makes the “JackFix” marketing campaign a big and evolving menace.
Observe us on Google Information, LinkedIn, and X for every day cybersecurity updates. Contact us to function your tales.