Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Malicious Go Module Targets Passwords and Installs Backdoor

Malicious Go Module Targets Passwords and Installs Backdoor

Posted on February 27, 2026 By CWS

Cybersecurity experts have revealed a new threat involving a deceptive Go module designed to steal passwords and establish unauthorized access via SSH, deploying a Linux backdoor known as Rekoobe.

Deceptive Module and Its Operations

The malicious module, found on github[.]com/xinfeisoft/crypto, masquerades as the legitimate “golang.org/x/crypto” repository. It injects harmful code to capture sensitive information entered through terminal password prompts, which is then sent to a remote server. A shell script is executed in response, further facilitating the attack.

Researchers, including Kirill Boychenko from Socket, have identified this activity as a case of namespace confusion. The threat actor exploits the distinction between the official go.googlesource.com/crypto repository and its GitHub mirror to make their malicious repository appear legitimate in dependency graphs.

Backdoor Details and Impact

The Rekoobe backdoor is embedded within “ssh/terminal/terminal.go”. Whenever a victim application uses the ReadPassword() function intended to securely read inputs like passwords, it inadvertently captures and transmits sensitive data.

The downloaded script acts as a Linux stager, inserting an attacker’s SSH key into the “/home/ubuntu/.ssh/authorized_keys” file, modifying iptables to relax firewall settings, and fetching additional payloads disguised with the .mp5 extension. One payload checks internet connectivity and attempts communication with a specific IP over TCP port 443, potentially serving as a recon tool.

Rekoobe and Ongoing Threats

The second payload is identified as Rekoobe, a Linux trojan active since at least 2015. It allows attackers to execute commands from a controlled server, facilitating further payload downloads, file theft, and reverse shell execution. Recently, groups like APT31 have utilized Rekoobe for cyber espionage.

Although the malicious package is still visible on pkg.go.dev, the Go security team has initiated actions to mark it as harmful. This campaign is a classic example of low-effort, high-impact attacks, leveraging lookalike modules to exploit high-value functions such as ReadPassword.

Experts warn of similar supply chain attacks targeting other critical libraries, anticipating increased use of hosting surfaces to rotate infrastructure without code republishing.
The Hacker News Tags:APT31, Cybersecurity, Linux security, malicious Go module, namespace confusion, password theft, Rekoobe backdoor, SSH access, supply chain attacks, threat actor

Post navigation

Previous Post: Go Module Attack: Password Theft and Backdoor Insertion Threat
Next Post: Aeternum Botnet Uses Polygon Blockchain for C&C Resilience

Related Posts

Android Trojan Crocodilus Now Active in 8 Countries, Targeting Banks and Crypto Wallets Android Trojan Crocodilus Now Active in 8 Countries, Targeting Banks and Crypto Wallets The Hacker News
Fortinet Confirms Active FortiCloud SSO Bypass on Fully Patched FortiGate Firewalls Fortinet Confirms Active FortiCloud SSO Bypass on Fully Patched FortiGate Firewalls The Hacker News
AI Hallucinations Pose New Security Challenges AI Hallucinations Pose New Security Challenges The Hacker News
New TrickMo Variant Enhances Android Network Exploits New TrickMo Variant Enhances Android Network Exploits The Hacker News
AI-Assisted Malware Targets npm Users with PhantomRaven AI-Assisted Malware Targets npm Users with PhantomRaven The Hacker News
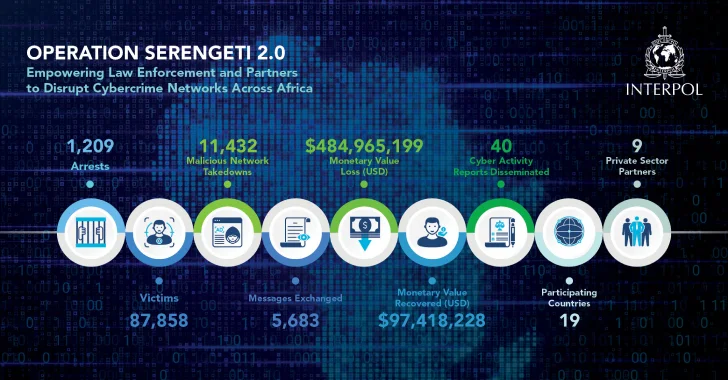
INTERPOL Arrests 1,209 Cybercriminals Across 18 African Nations in Global Crackdown INTERPOL Arrests 1,209 Cybercriminals Across 18 African Nations in Global Crackdown The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • OpenAI Employee Charged for Planting Hidden Recorder
  • Microsoft Disrupts Major Phishing Kits Behind Global Scams
  • Critical NGINX Vulnerabilities Risk Server Stability
  • Critical Flaw in Collabora CODE App Exploited by Hackers
  • Windows 11 Update Disrupts Remote Desktop Connectivity

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • OpenAI Employee Charged for Planting Hidden Recorder
  • Microsoft Disrupts Major Phishing Kits Behind Global Scams
  • Critical NGINX Vulnerabilities Risk Server Stability
  • Critical Flaw in Collabora CODE App Exploited by Hackers
  • Windows 11 Update Disrupts Remote Desktop Connectivity

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark