Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Over 900 FreePBX Systems Infected in Web Shell Attacks

Over 900 FreePBX Systems Infected in Web Shell Attacks

Posted on February 27, 2026 By CWS

The Shadowserver Foundation has disclosed a significant cybersecurity incident affecting over 900 Sangoma FreePBX systems worldwide. These systems have been compromised by web shells, a direct consequence of a command injection vulnerability that began being exploited in December 2025.

Widespread Impact of the Vulnerability

The majority of the affected FreePBX instances are distributed globally, with 401 located in the United States, followed by Brazil, Canada, Germany, and France. The exploitation of this vulnerability, identified as CVE-2025-64328 with a CVSS score of 8.6, allows attackers to execute arbitrary shell commands post-authentication.

An advisory from FreePBX in November 2025 highlighted the potential for remote access through this flaw, particularly affecting users with access to the FreePBX Administration panel. This exploit could grant unauthorized access to the system, enabling harmful activities.

Version Vulnerability and Mitigation Steps

Vulnerable versions include FreePBX 17.0.2.36 and newer, with a fix available in version 17.0.3. To mitigate risks, it’s crucial to implement security controls ensuring that only authorized personnel can access the FreePBX Administrator Control Panel. Additional precautions include restricting ACP access from untrusted networks and updating the filestore module promptly.

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has recognized the active exploitation of this vulnerability, adding it to their Known Exploited Vulnerabilities (KEV) list, emphasizing the need for immediate action.

Exploitation by Threat Actors

A report by Fortinet FortiGuard Labs ties the exploitation to a cybercriminal group known as INJ3CTOR3. This group has been using CVE-2025-64328 since early December 2025 to install a web shell named EncystPHP. This shell operates with elevated privileges, allowing arbitrary commands and initiating outbound calls via the PBX system.

To safeguard against these ongoing threats, FreePBX users are strongly advised to upgrade their systems to the latest version immediately. Staying updated is critical in preventing further exploitation and securing network environments.

As cyber threats continue to evolve, maintaining up-to-date security measures and monitoring systems for vulnerabilities are essential steps for protecting sensitive information and infrastructure.
The Hacker News Tags:CISA, CVE-2025-64328, Cybersecurity, Fortinet, FreePBX, INJ3CTOR3, network security, Shadowserver Foundation, Vulnerability, web shell attacks

Post navigation

Previous Post: Vshell: Emerging C2 Tool Gains Popularity Among Cybercriminals
Next Post: Dohdoor Malware Targets U.S. Schools and Healthcare

Related Posts

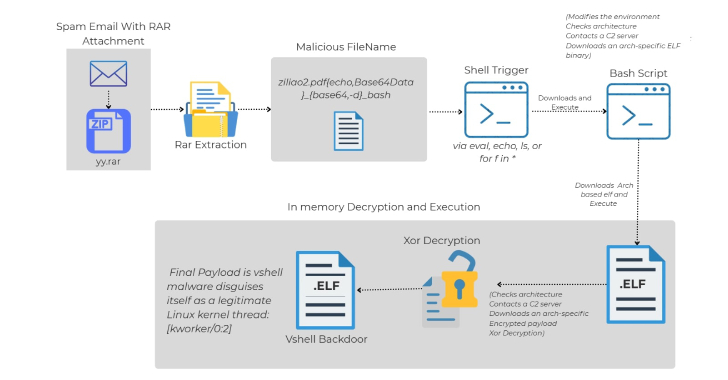
Linux Malware Delivered via Malicious RAR Filenames Evades Antivirus Detection Linux Malware Delivered via Malicious RAR Filenames Evades Antivirus Detection The Hacker News
AI-Driven Windows Malware Uses Voting System AI-Driven Windows Malware Uses Voting System The Hacker News
Open Source Web Application Firewall with Zero-Day Detection and Bot Protection Open Source Web Application Firewall with Zero-Day Detection and Bot Protection The Hacker News
JADEPUFFER Exploits Azure to Delete Resources JADEPUFFER Exploits Azure to Delete Resources The Hacker News
Two CVSS 10.0 Bugs in Red Lion RTUs Could Hand Hackers Full Industrial Control Two CVSS 10.0 Bugs in Red Lion RTUs Could Hand Hackers Full Industrial Control The Hacker News
Security Tools Alone Don’t Protect You — Control Effectiveness Does Security Tools Alone Don’t Protect You — Control Effectiveness Does The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Windows 11 Update Disrupts Remote Desktop Connectivity
  • Cisco Alerts on Exploited Vulnerability in Email Gateway
  • Optimize MSSP Efficiency by Reducing Tier 1 Bottlenecks
  • SAP Addresses Critical Vulnerabilities in NetWeaver and S/4HANA
  • Microsoft Fixes Record 1,413 Vulnerabilities Including Exploited Bug

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Windows 11 Update Disrupts Remote Desktop Connectivity
  • Cisco Alerts on Exploited Vulnerability in Email Gateway
  • Optimize MSSP Efficiency by Reducing Tier 1 Bottlenecks
  • SAP Addresses Critical Vulnerabilities in NetWeaver and S/4HANA
  • Microsoft Fixes Record 1,413 Vulnerabilities Including Exploited Bug

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark