Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Windows 11 Upgrade Issues Disrupt Network Access

Windows 11 Upgrade Issues Disrupt Network Access

Posted on March 4, 2026 By CWS

Windows 11 users are encountering significant network disruptions following upgrades from version 23H2 to 25H2. This recurring issue, which has affected enterprise environments, involves the deletion of essential 802.1X authentication configurations, resulting in systems being unable to connect to wired networks without manual intervention.

Persistent Network Bug

Reports from the tech community, particularly on Reddit’s r/sysadmin, highlight this persistent bug that has troubled administrators since the transition from Windows 10 to 11. The problem, now observed in annual version upgrades, has notably impacted the 23H2-to-24H2 and 23H2-to-25H2 upgrade paths.

During these upgrades, critical files within the C:Windowsdot3svcPolicies directory, which store LAN authentication profiles, are inexplicably erased. This results in systems losing network access post-upgrade as they rely on these profiles for IEEE 802.1X authentication.

Impact on Enterprise Systems

The absence of network connectivity poses a severe challenge in enterprise settings. Without access to the network, systems are unable to receive necessary Group Policy updates to restore the 802.1X configurations. As a result, administrators must physically connect affected devices to unsecured network segments and manually execute commands to reapply the policies.

This issue has been documented since the Windows 10 22H2 to Windows 11 23H2 transition, with recent upgrades showing similar data loss patterns. The problem’s persistence through multiple Windows 11 updates has yet to receive a formal acknowledgment or fix from Microsoft.

Workarounds and Next Steps

In the absence of an official solution, system administrators have devised temporary workarounds. These include backing up the dot3svcPolicies folder before upgrades and restoring it afterward, connecting devices to non-802.1X ports for policy reapplication, and integrating profile restoration commands into the Windows setup process.

Despite these efforts, Microsoft has not issued a knowledge base article or hotfix regarding this issue. Administrators managing large networks are advised to review and adjust their upgrade procedures, ensuring critical backup steps are implemented before deploying future Windows updates.

For ongoing updates on cybersecurity and IT management, follow us on Google News, LinkedIn, and X. Reach out if you have stories to share or insights to feature.
Cyber Security News Tags:802.1X, enterprise IT, IT management, Microsoft, network authentication, network connectivity, system administrators, upgrade issue, Windows 11, Windows upgrade bug

Post navigation

Previous Post: Coruna Exploit Kit Threatens Thousands of iPhones
Next Post: CISA Flags VMware Vulnerability Amid Active Exploits

Related Posts

Threat Actors Exploiting Black Friday Shopping Hype Threat Actors Exploiting Black Friday Shopping Hype Cyber Security News
Critical Vulnerability in Active Directory Services Resolved Critical Vulnerability in Active Directory Services Resolved Cyber Security News
Bloody Wolf Hackers Mimic as Government Agencies to Deploy NetSupport RAT via Weaponized PDF’s Bloody Wolf Hackers Mimic as Government Agencies to Deploy NetSupport RAT via Weaponized PDF’s Cyber Security News
Microsoft 365 Introduces Copilot Cowork for Task Automation Microsoft 365 Introduces Copilot Cowork for Task Automation Cyber Security News
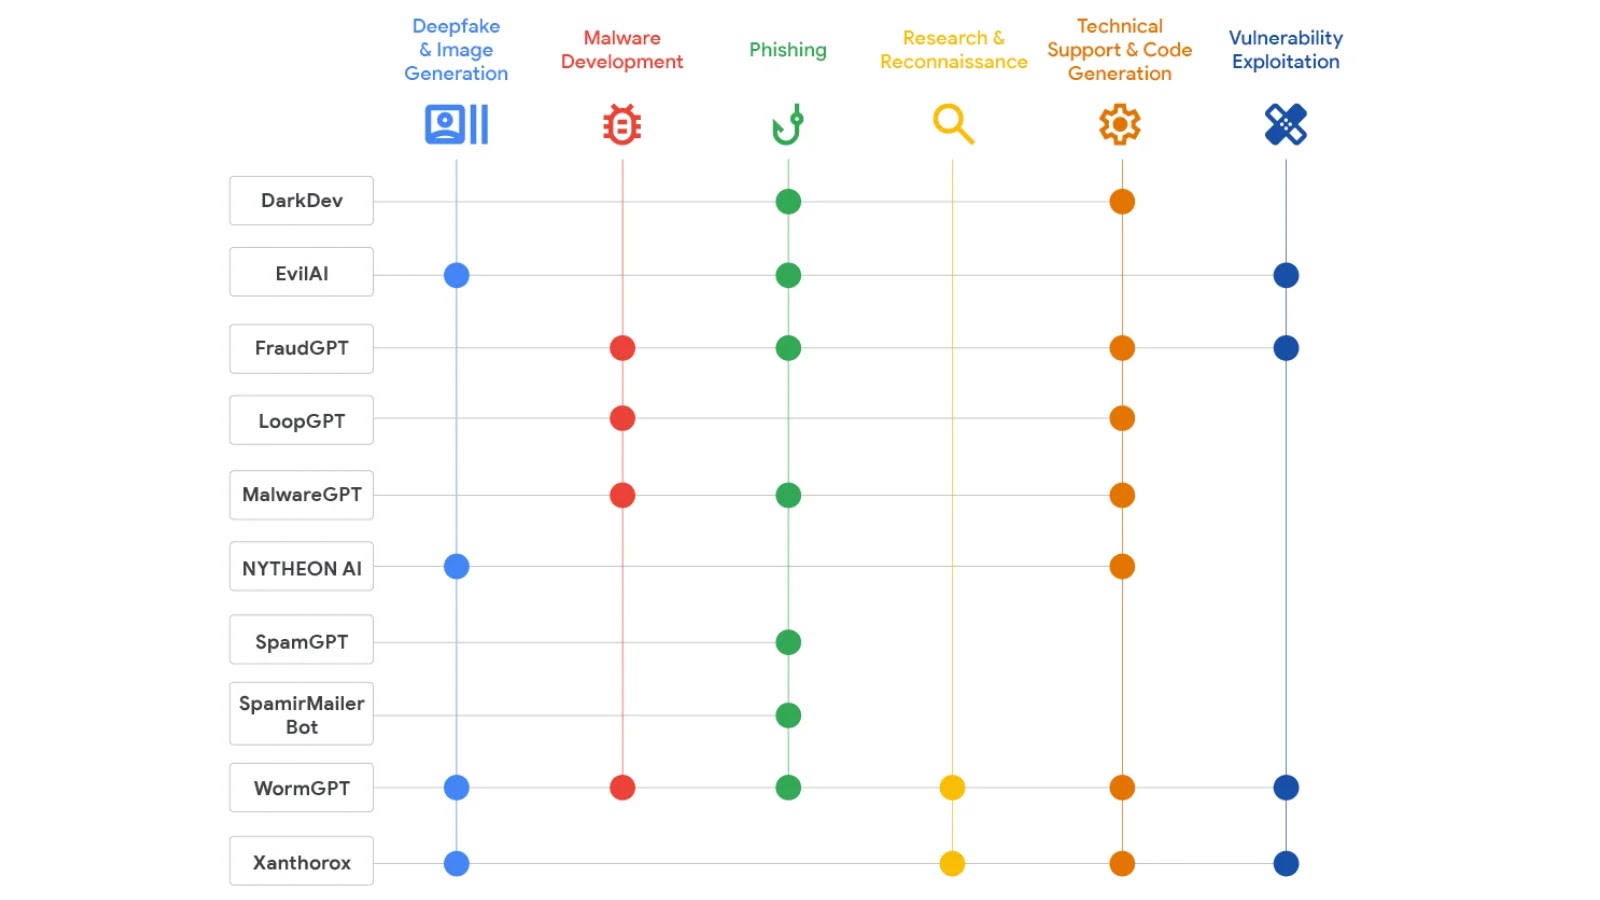
List of AI Tools Promoted by Threat Actors in Underground Forums and Their Capabilities List of AI Tools Promoted by Threat Actors in Underground Forums and Their Capabilities Cyber Security News
AI-powered Pentesting Tool ‘Villager’ Combines Kali Linux Tools with DeepSeek AI for Automated Attacks AI-powered Pentesting Tool ‘Villager’ Combines Kali Linux Tools with DeepSeek AI for Automated Attacks Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • AI-Driven Attacks Target Over 100 Companies, Cost $5,000
  • SBI Alleged Data Breach: Hackers Claim Access to Vast Database
  • ROMULUS Platform Exploited by Hackers for Malware Distribution
  • AI Uncovers Hidden Cryptocurrency Miner on Mac
  • AI Agents Pose Potential Security Risks, Microsoft Warns

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • AI-Driven Attacks Target Over 100 Companies, Cost $5,000
  • SBI Alleged Data Breach: Hackers Claim Access to Vast Database
  • ROMULUS Platform Exploited by Hackers for Malware Distribution
  • AI Uncovers Hidden Cryptocurrency Miner on Mac
  • AI Agents Pose Potential Security Risks, Microsoft Warns

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark