Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Adobe Reader Zero-Day Exploit Targets Users Since Late 2025

Adobe Reader Zero-Day Exploit Targets Users Since Late 2025

Posted on April 9, 2026 By CWS

Since late 2025, cybercriminals have been leveraging a previously undisclosed zero-day vulnerability in Adobe Reader through malicious PDF files. Detailed by EXPMON’s Haifei Li, this sophisticated exploit has surfaced with documents like ‘Invoice540.pdf’ appearing on the VirusTotal platform. The initial instance was detected on November 28, 2025, followed by another upload on March 23, 2026.

Exploitation Tactics and Social Engineering

The strategically named PDF files suggest a social engineering component, enticing users to open these documents in Adobe Reader. Upon access, the files execute hidden JavaScript aimed at gathering sensitive information and facilitating additional payloads. A security researcher, Gi7w0rm, noted in an online post that these PDF files employ Russian language themes related to current events in the oil and gas sector.

Technical Breakdown of the Exploit

The vulnerability allows the execution of privileged Acrobat APIs in the latest Adobe Reader version, posing a significant threat. The exploit acts as an initial entry point for information collection and potential escalation to remote code execution (RCE) and sandbox escape (SBX) attacks. It also transmits collected data to a remote server, with the capacity to execute further JavaScript code.

Implications and Security Community Response

The potential for further exploitation is underscored by the possibility of collecting local data and advancing fingerprinting attacks. However, the exact nature of subsequent exploits remains unclear, as no response was received from the server, possibly due to unmet criteria in the testing environment. Despite this, Haifei Li emphasizes that the zero-day capability for broad data harvesting and possible RCE/SBX exploits necessitates heightened vigilance from the security community.

This story is under continuous development. Stay tuned for updates as more information becomes available.

The Hacker News Tags:Adobe Reader, Cybersecurity, information harvesting, JavaScript exploit, malicious PDFs, PDF exploit, remote code execution, sandbox escape, threat intelligence, zero-day vulnerability

Post navigation

Previous Post: LucidRook Malware Masquerades as Security Software in Taiwan
Next Post: Google API Keys in Android Apps Risk Data Breach

Related Posts

Global Crackdown on SocGholish Malware Cleans Thousands of Sites Global Crackdown on SocGholish Malware Cleans Thousands of Sites The Hacker News
Critical Flaw in LMS Exploited for Cyber Attacks Critical Flaw in LMS Exploited for Cyber Attacks The Hacker News
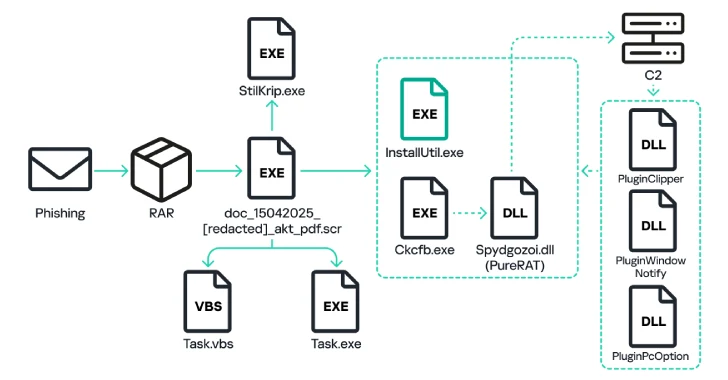
PureRAT Malware Spikes 4x in 2025, Deploying PureLogs to Target Russian Firms PureRAT Malware Spikes 4x in 2025, Deploying PureLogs to Target Russian Firms The Hacker News
PaperCut Zero-Day Vulnerability Actively Exploited PaperCut Zero-Day Vulnerability Actively Exploited The Hacker News
UAT-9921 Targets Tech and Finance with VoidLink Malware UAT-9921 Targets Tech and Finance with VoidLink Malware The Hacker News
INTERPOL Dismantles Sniper Dz Phishing Platform INTERPOL Dismantles Sniper Dz Phishing Platform The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Cisco Nexus Vulnerabilities Expose Networks to Critical Threats
  • TP-Link Faces Legal Actions Over Security Concerns
  • 16 Harmful Firefox Add-ons Imitate Wallets to Steal Data
  • Hackers Exploit GitHub Poem for AI Malware Control
  • Owner Charged in $11M Fraudulent Ransomware Scheme

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Cisco Nexus Vulnerabilities Expose Networks to Critical Threats
  • TP-Link Faces Legal Actions Over Security Concerns
  • 16 Harmful Firefox Add-ons Imitate Wallets to Steal Data
  • Hackers Exploit GitHub Poem for AI Malware Control
  • Owner Charged in $11M Fraudulent Ransomware Scheme

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark