Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Privacy Concerns Over Exposed Claude AI Chats in Search

Privacy Concerns Over Exposed Claude AI Chats in Search

Posted on July 26, 2026 By CWS

Recent developments have spotlighted significant privacy issues after Anthropic’s Claude AI shared chats were found in public search results. These incidents have raised alarms among users who may have shared sensitive details using the platform.

Public Search Exposure of Shared Chats

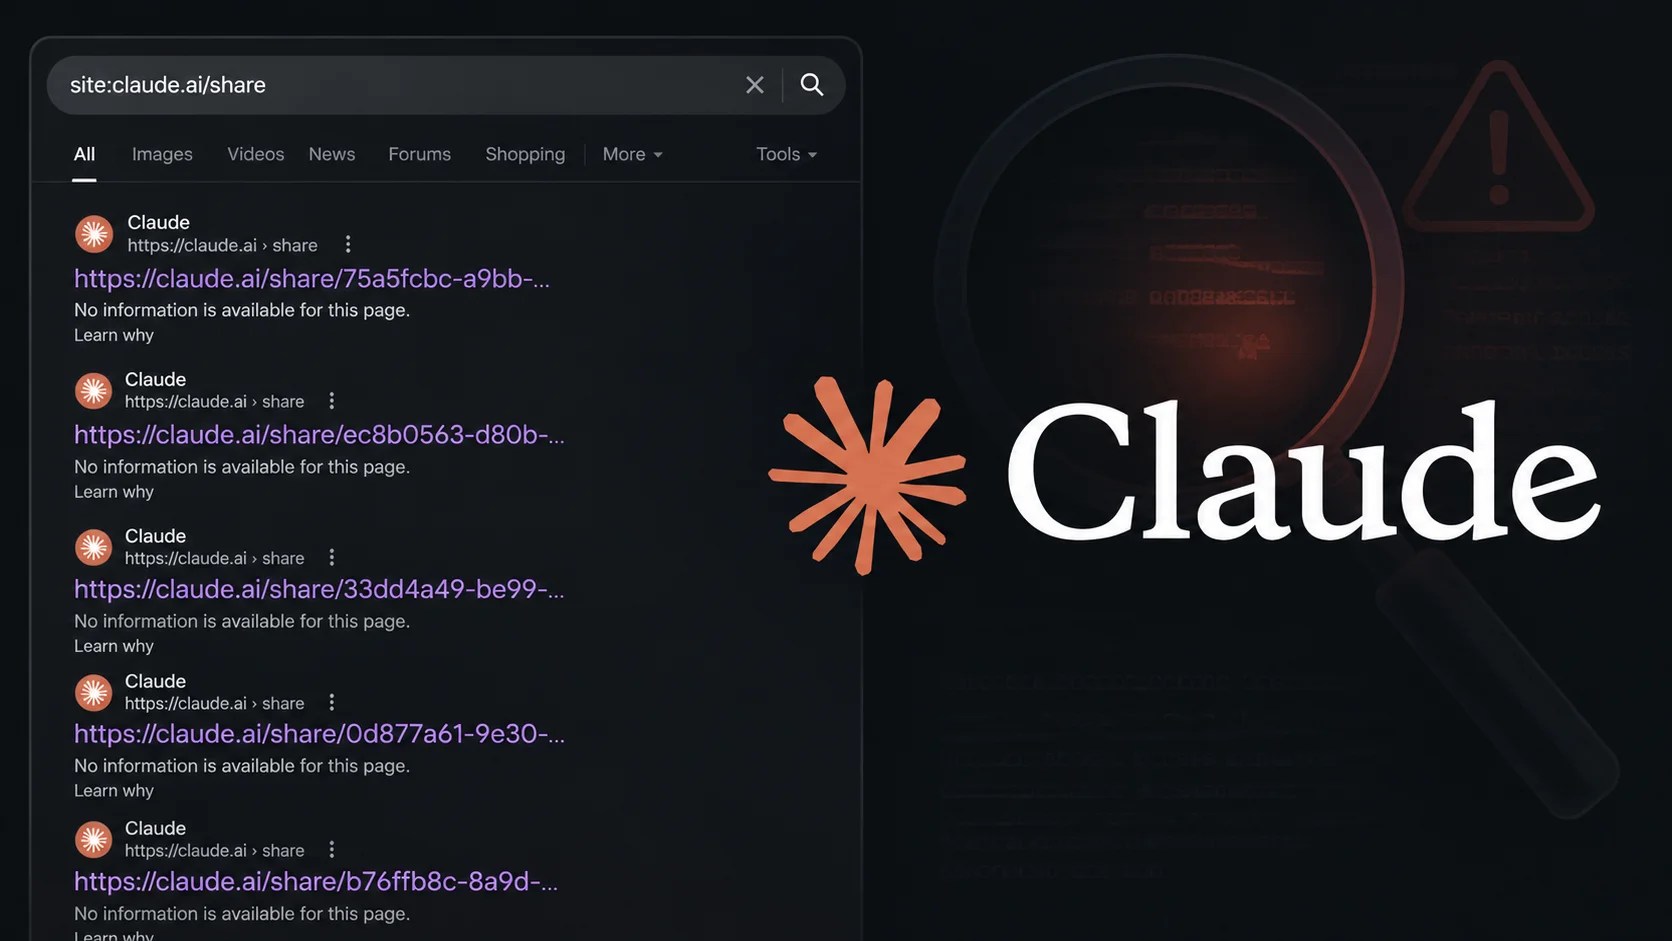
A Reddit user highlighted over the weekend that numerous shared chats from Claude AI were accessible through Google searches. Queries like site:claude.ai/share allowed users to find conversations that included legal advice, engineering tasks, and personal discussions.

The share feature on Claude AI permits users to create public URLs for sharing conversations. According to the Reddit post, these pages were missing appropriate noindex tags, allowing search engines to crawl and index the content fully. Such exposure often occurs when links are disseminated through forums, social media, or unintended channels.

Implications of the Privacy Breach

Exposed chats reportedly encompassed a range of sensitive topics:

  • Legal strategies from attorneys
  • Technical troubleshooting and code from engineers
  • Personal and sensitive user conversations

This situation mirrors past incidents involving ChatGPT, where shared links similarly became searchable, turning private exchanges into public records.

By Sunday, the public visibility of these Claude share pages had diminished, suggesting either swift deindexing or a backend resolution from Anthropic. At the time of this report, Anthropic had not made a public comment.

Risks and Recommendations for Users

Security experts and privacy-minded individuals caution that removal from search results does not ensure previous links are inaccessible. Saved or bookmarked URLs may still be operational unless Anthropic disables them server-side.

Shared AI chats often contain more than casual queries. Professionals use platforms like Claude for tasks such as drafting contracts, debugging proprietary code, analyzing business data, and discussing personal matters. The potential data leakage and intellectual property risks are substantial when these become accessible online.

Anthropic advises users to:

  • Review and manage all shared conversations in Claude settings
  • Delete unnecessary shared links
  • Refrain from posting share URLs in public domains
  • Consider shared AI chats as publicly accessible by default

The incident emphasizes a critical lesson in AI product development: features designed for sharing convenience can inadvertently lead to exposure unless robust privacy controls are implemented.

Cyber Security News Tags:AI privacy, AI security, Anthropic, Claude AI, data exposure, privacy concerns, public search results, search engine indexing, shared chats, user data security

Post navigation

Previous Post: Pro-Iran Hacktivist Groups: Cyber Mobilization in Conflict
Next Post: Cybersecurity: Key Exploits and Vulnerabilities of the Week

Related Posts

Sweet Security Enhances AI Safety with New Blocking Features Sweet Security Enhances AI Safety with New Blocking Features Cyber Security News
VMware Workstation and Fusion 25H2 Released with New Features and Latest OS Support VMware Workstation and Fusion 25H2 Released with New Features and Latest OS Support Cyber Security News
EmEditor Editor Website Hacked to Deliver Infostealer Malware in Supply Chain Attack EmEditor Editor Website Hacked to Deliver Infostealer Malware in Supply Chain Attack Cyber Security News
Cybercriminals Exploit PowerShell for Sophisticated Phishing Attacks Cybercriminals Exploit PowerShell for Sophisticated Phishing Attacks Cyber Security News
Rising Phishing Threats Exploit Microsoft Teams and Email Rising Phishing Threats Exploit Microsoft Teams and Email Cyber Security News
Critical Vulnerability in Python PLY Library Enables Remote Code Execution Critical Vulnerability in Python PLY Library Enables Remote Code Execution Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • PHP Updates Windows Builds to Address Critical HTTP2Shell Flaw
  • Emperador Ransomware Claims Data Breach at AB InBev
  • PHP2Shell Exploit Targets University and Business Websites
  • OpenBSD 8.0 Enhances Security and Post-Quantum SSH
  • Anthropic’s Record-Breaking IPO Amid AI Safety Concerns

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • PHP Updates Windows Builds to Address Critical HTTP2Shell Flaw
  • Emperador Ransomware Claims Data Breach at AB InBev
  • PHP2Shell Exploit Targets University and Business Websites
  • OpenBSD 8.0 Enhances Security and Post-Quantum SSH
  • Anthropic’s Record-Breaking IPO Amid AI Safety Concerns

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark