Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
CEVA Logistics Breach Exposes Steam Hardware Buyers

CEVA Logistics Breach Exposes Steam Hardware Buyers

Posted on August 10, 2026 By CWS

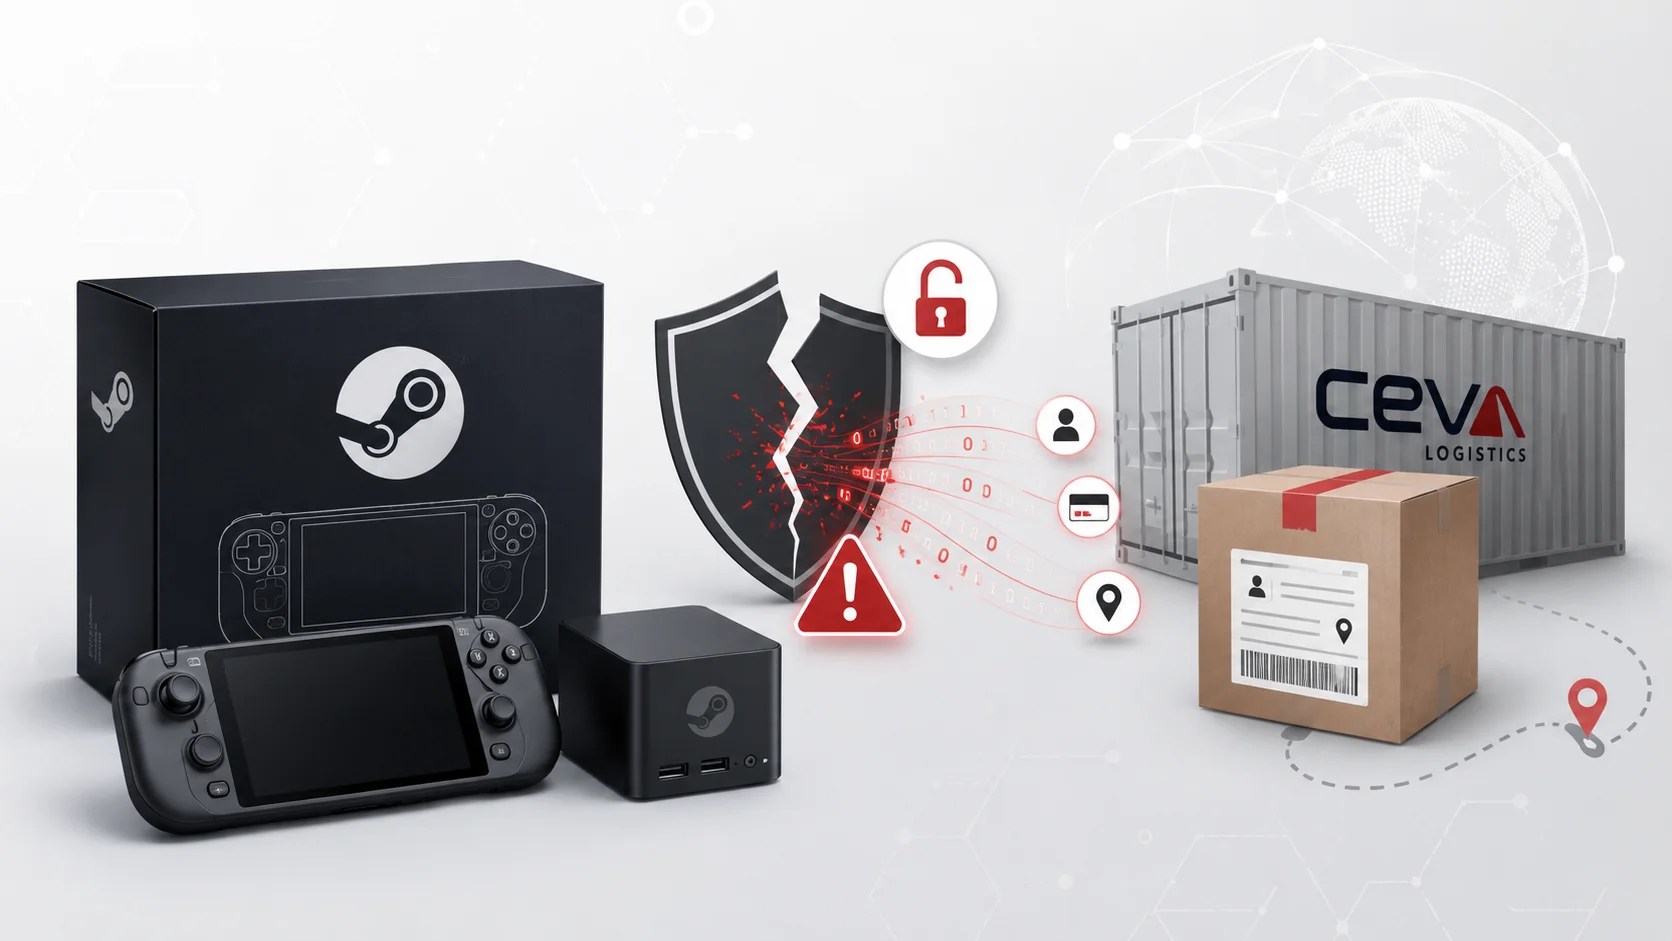
Valve has reported a significant data breach involving its European shipping partner, CEVA Logistics, which has impacted buyers of its Steam hardware products. This breach affected customers who purchased items such as the Steam Deck, Steam Machine, and Steam Controller across Europe.

Details of the Data Breach

The cyberattack on CEVA Logistics took place from July 29 to August 1, 2026. Valve became aware of the breach on August 7 and promptly alerted affected customers through a security email. The breach potentially exposed delivery-related data that CEVA stores for up to ninety days following an order.

The compromised information includes customers’ full names, addresses, phone numbers, email addresses linked to their Steam accounts, and details about purchased hardware. Valve has assured customers that sensitive data such as Steam account credentials, passwords, and payment information remain secure, as CEVA did not have access to these details.

Wider Impact and Previous Incidents

The breach at CEVA Logistics is part of a larger disruption affecting its European operations. Reports indicate that the attack hindered operations in eight CEVA warehouses, causing shipment delays for many retail clients. Notable companies like Bol, De Bijenkorf, Ajax, ING, and Ace & Tate, all reliant on CEVA for logistics, have also reported data exposure.

This incident is not CEVA’s first encounter with cyber threats. In September 2025, a group named CoinbaseCartel claimed responsibility for a breach that compromised extensive database information. The connection between the two incidents remains unclear.

Potential Risks and Customer Guidance

Security experts caution that the leaked information could facilitate phishing and fraud attempts, particularly with the aid of AI tools that customize scam messages. Customers are advised to be vigilant against emails impersonating Steam, especially those requesting payments or login credentials.

Valve has emphasized the importance of verifying communications through official Steam channels and staying aware of potential scam attempts leveraging the exposed data. This breach highlights vulnerabilities in digital supply chains, where even robust internal security measures can be undermined by third-party partners.

Strengthening security protocols and fostering vigilance among customers are crucial in mitigating the risks posed by such data breaches.

Cyber Security News Tags:CEVA Logistics, customer data, Cybersecurity, data breach, digital supply chain, European operations, phishing scams, Steam, Steam Deck, Valve

Post navigation

Previous Post: Stealthium Enhances Security for AI Accelerators and Neo-Clouds
Next Post: Secure AI-Driven Development: Webinar Insights

Related Posts

Kiteworks Advises Server Shutdown Amid Threat Intelligence Kiteworks Advises Server Shutdown Amid Threat Intelligence Cyber Security News
New Tykit Phishing Kit Mimics Microsoft 365 Login Pages to Steal Corporate Account Credentials New Tykit Phishing Kit Mimics Microsoft 365 Login Pages to Steal Corporate Account Credentials Cyber Security News
Threat Actors Weaponizes LNK Files to Deploy RedLoader Malware on Windows Systems Threat Actors Weaponizes LNK Files to Deploy RedLoader Malware on Windows Systems Cyber Security News
Hackers Can Manipulate Internet-Based Solar Panel Systems to Execute Attacks in Minutes Hackers Can Manipulate Internet-Based Solar Panel Systems to Execute Attacks in Minutes Cyber Security News
Bright Security Launches AI-Driven STAR Fuzzer Bright Security Launches AI-Driven STAR Fuzzer Cyber Security News
Critical Cybersecurity Developments: Chrome Zero-Day, AI Threats Critical Cybersecurity Developments: Chrome Zero-Day, AI Threats Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • CISA Highlights SonicOS SSLVPN Security Weakness
  • GhostAction Campaign Targets 500 GitHub Accounts for Credentials
  • Notepad++ 8.9.9 Update Resolves Critical Security Flaws
  • Ethersphere Tools Breached, Malware Targets Wallets
  • Abe Office Malware Circumvents Chrome Security to Steal Data

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • CISA Highlights SonicOS SSLVPN Security Weakness
  • GhostAction Campaign Targets 500 GitHub Accounts for Credentials
  • Notepad++ 8.9.9 Update Resolves Critical Security Flaws
  • Ethersphere Tools Breached, Malware Targets Wallets
  • Abe Office Malware Circumvents Chrome Security to Steal Data

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark