Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Exploit Released for Microsoft Exchange Server RCE Vulnerability

Exploit Released for Microsoft Exchange Server RCE Vulnerability

Posted on September 1, 2026 By CWS

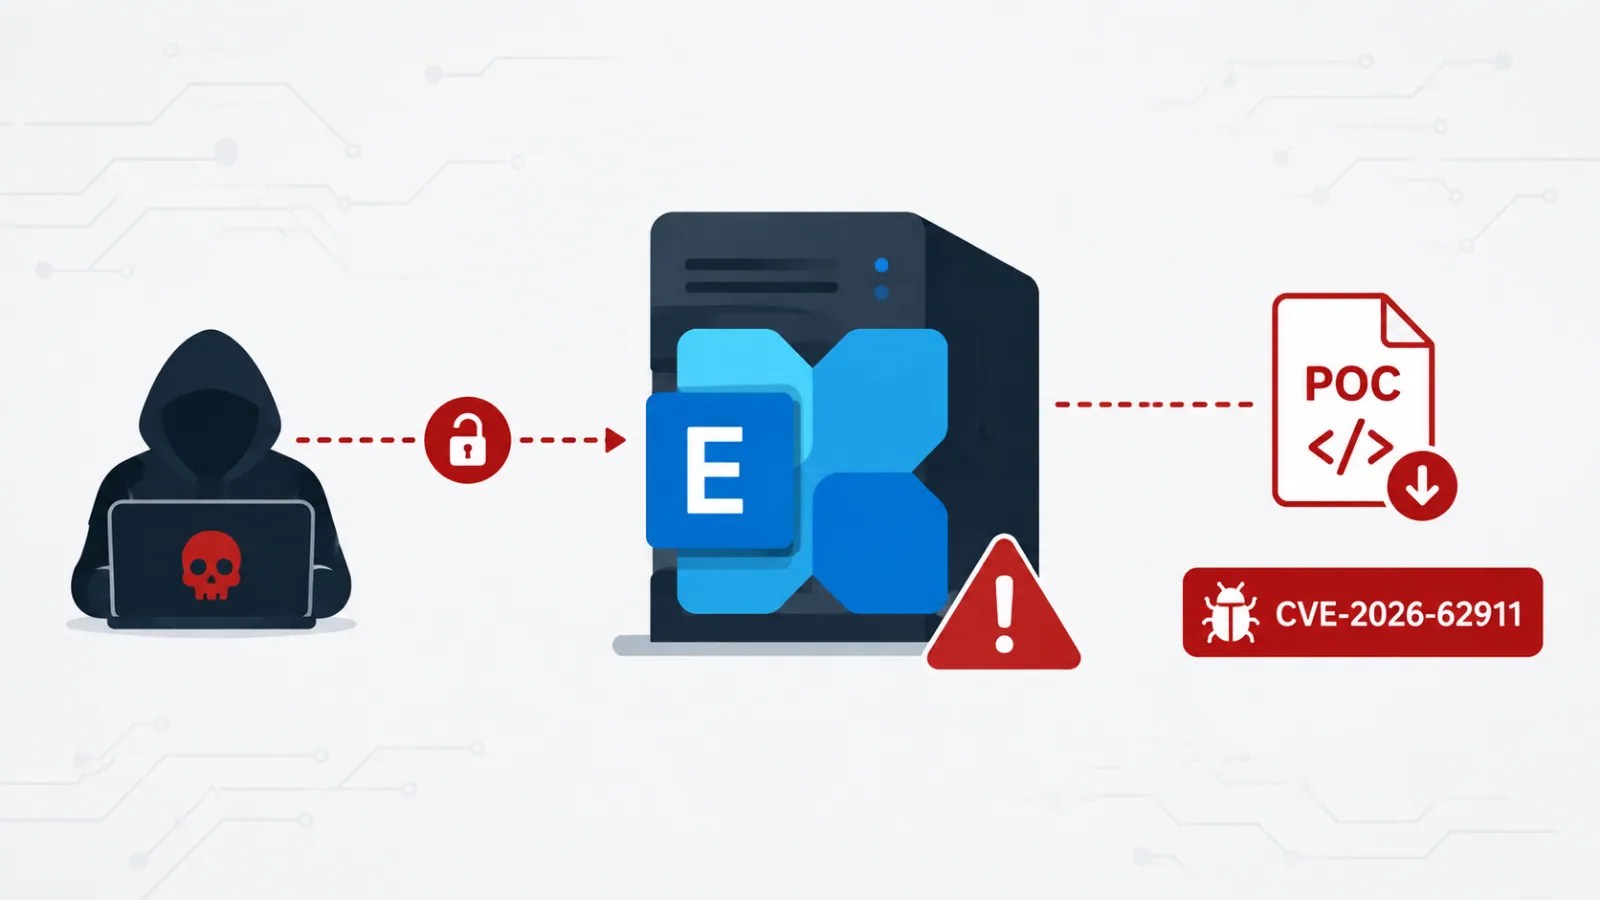
A newly released proof-of-concept (PoC) exploit targeting CVE-2026-62911 has emerged, affecting Microsoft Exchange Server. This vulnerability is linked to an authentication bypass that could potentially lead to remote code execution without requiring prior authentication.

Understanding the Vulnerability

Although Microsoft categorizes this issue as an elevation-of-privilege vulnerability, research shows it can allow unauthenticated remote code execution in vulnerable Exchange environments. Researcher Nguyen Van Hiep published the PoC on GitHub, focusing on the Exchange Mailbox Replication Proxy service, known as MRSProxy.

The exploit documentation outlines that an HTTP.sys-hosted MRSProxy endpoint lacks Extended Protection for Authentication. This deficiency permits attackers to relay NTLM authentication from an Exchange machine account to the MRSProxy service, compromising the system.

Technical Details of the Exploit

Initially disclosed by Microsoft in August 2026, CVE-2026-62911 involves an authentication-bypass capture-replay weakness affecting on-premises Exchange servers. While Microsoft’s official description indicates that an authenticated attacker could elevate their privileges, the PoC reveals a more significant risk by demonstrating an NTLM relay pathway.

Exchange servers expose MRSProxy through multiple endpoints. Although the IIS-hosted /EWS/MRSProxy.svc path is protected, the MailboxReplicationService ProxyService endpoint may fail to validate channel bindings, enabling an NTLM relay attack.

Impact and Mitigation

In the attack scenario, an Exchange server is coerced to authenticate to an attacker-controlled listener using techniques like PetitPotam. The attacker then relays this authentication to another vulnerable Exchange server, gaining access to mailbox replication functions.

The PoC exploits WCF methods within the replication service, potentially allowing attackers to execute commands by placing a webshell in a web-accessible directory. Reports suggest this could lead to SYSTEM-level compromise.

The vulnerability comes from a three-bug chain demonstrated by DEVCORE’s Orange Tsai at Pwn2Own Berlin 2026, highlighting the severe security implications. Affected versions include Exchange Server 2016 CU23, Exchange Server 2019 CU14 and CU15, and Exchange Server Subscription Edition RTM, with fixes available in Microsoft’s August 2026 security updates.

Future Outlook

As Exchange Server 2016 reached the end of support in October 2025, those lacking Extended Security Updates may face challenges in remediation. Administrators should ensure Extended Protection settings are verified, minimize exposure of Exchange services, monitor NTLM relay activity, and inspect unexpected ASPX files in directories.

This incident underscores the importance of timely security updates and proactive monitoring to prevent exploits. Organizations are advised to integrate threat intelligence into their security operations to strengthen defenses against such vulnerabilities.
Cyber Security News Tags:authentication bypass, CVE-2026-62911, Cybersecurity, elevation of privilege, Exchange Server, Exploit, Microsoft Exchange, NTLM relay, RCE vulnerability, security update

Post navigation

Previous Post: Hackers Target Langflow with Critical Vulnerability
Next Post: Iranian Hackers Use Job Offers to Spread Cross-Platform Malware

Related Posts

Russian Hackers Exploiting 7-Year-Old Cisco Vulnerability to Collect Configs from Industrial Systems Russian Hackers Exploiting 7-Year-Old Cisco Vulnerability to Collect Configs from Industrial Systems Cyber Security News
Critical TP-Link Vulnerabilities Enable Unauthorized Access Critical TP-Link Vulnerabilities Enable Unauthorized Access Cyber Security News
Threat Actors Weaponizing .hwp Files to Deliver RokRAT Malware Threat Actors Weaponizing .hwp Files to Deliver RokRAT Malware Cyber Security News
CISA releases New ICS Advisories Surrounding Vulnerabilities and Exploits CISA releases New ICS Advisories Surrounding Vulnerabilities and Exploits Cyber Security News
New Windows-Based Airstalk Malware Employs Multi-Threaded C2 Communication to Steal Logins New Windows-Based Airstalk Malware Employs Multi-Threaded C2 Communication to Steal Logins Cyber Security News
Phishing Emails Target iOS Users with Fake AI Apps Phishing Emails Target iOS Users with Fake AI Apps Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • iOS 27.0.1 Jailbreak Achieved on iPhone 18 Pro
  • AI-Driven Scripts Exploit Linux for Credential Theft
  • OpenBSD Exploit Chains 37-Year-Old Bug for Root Access
  • Decades-Old Kernel Flaw Exploited for OpenBSD Root Access
  • AOMEI Backupper Update Servers Breached for Backdoor Installs

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • iOS 27.0.1 Jailbreak Achieved on iPhone 18 Pro
  • AI-Driven Scripts Exploit Linux for Credential Theft
  • OpenBSD Exploit Chains 37-Year-Old Bug for Root Access
  • Decades-Old Kernel Flaw Exploited for OpenBSD Root Access
  • AOMEI Backupper Update Servers Breached for Backdoor Installs

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark