Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
OWASP’s OASIS Initiative Tackles Open Source Vulnerabilities

OWASP’s OASIS Initiative Tackles Open Source Vulnerabilities

Posted on September 2, 2026 By CWS

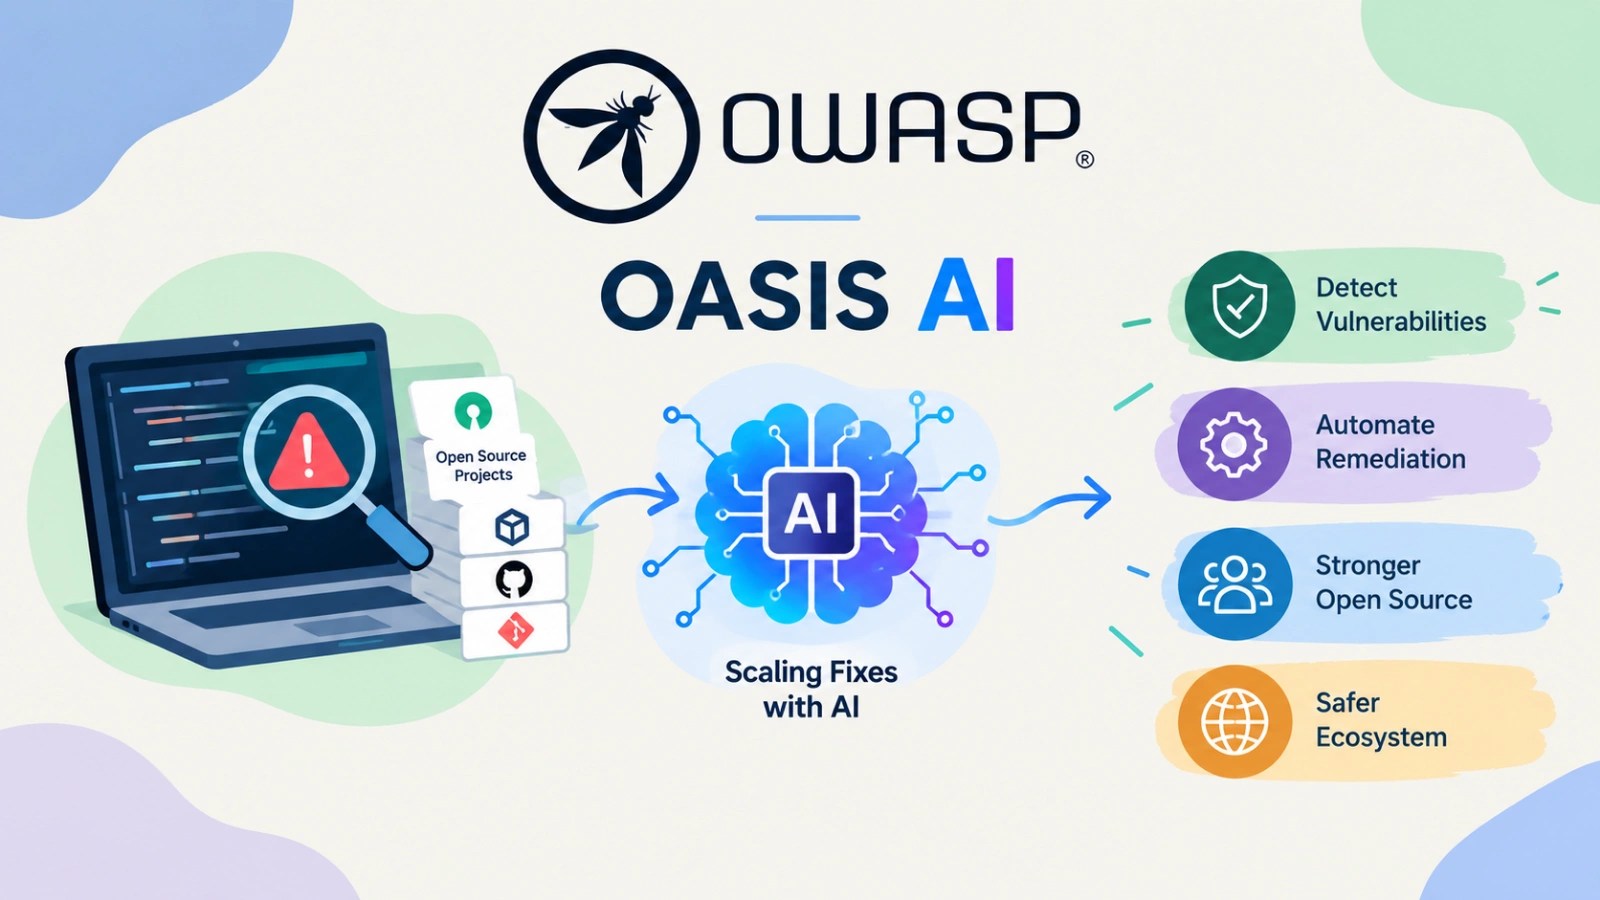
OWASP has introduced the Open Automated Security Initiative for Software (OASIS), a worldwide collaboration aimed at bridging the gap between identifying and remedying vulnerabilities in open source software. Announced in San Francisco on August 26, 2026, the initiative combines AI-generated patches with human oversight from application security experts to provide open source maintainers with reliable, ready-to-deploy solutions, rather than merely increasing the list of known vulnerabilities.

Addressing the Open Source Challenge

According to the 2026 Black Duck Open Source Security and Risk Analysis Report, open source software forms the foundation of approximately 98% of commercial codebases. Yet, maintainers often find themselves overwhelmed by tools that highlight vulnerabilities without offering actionable solutions. OASIS aims to resolve this issue through a three-step process.

The initiative begins with automated tools scanning popular repositories, generating potential fixes as vulnerabilities are detected. These candidate fixes are then subjected to a rapid review by a community of application security professionals, significantly reducing the time required for validation. Once vetted, the patches are submitted to maintainers, providing them with a dependable starting point that can be integrated into their codebases.

Community and Industry Support

Since its initial launch, OASIS has attracted hundreds of security professionals from various sectors, with key support from sponsors like AppSecAI, Intigriti, and DryRun Security. In the announcement, Chris Holt from Intigriti highlighted the systemic risk posed by unresolved vulnerabilities in open source software, emphasizing OASIS’s role in fostering collaboration between the AppSec and open source communities to enhance software security.

As cyber threats evolve, attackers increasingly utilize techniques such as AI-assisted vulnerability discovery, which surpasses manual defensive efforts. James Wickett, CEO of DryRun Security, pointed out that the same AI advancements can be leveraged for defense when combined with human expertise. Michael Cartsonis of AppSecAI noted that OASIS provides security professionals with a streamlined way to contribute their code-review skills effectively.

Strategic Impact and Future Outlook

OASIS is designed to complement existing enterprise-led initiatives like OpenAI’s Patch the Planet and the Linux Foundation’s Akrites by focusing on the extensive range of libraries and applications used by businesses. David Kosorok of ACV Auctions described it as a high-impact approach in application security, as a single verified fix can secure numerous applications downstream.

The initiative invites participation through roles such as vulnerability validators, repository managers, and automation operators, offering a neutral platform for security practitioners eager to address vulnerabilities in open source software. This collaborative effort promises to enhance the security of the digital infrastructure that underpins modern technology.
Cyber Security News Tags:AI, Appsec, community effort, Cybersecurity, Oasis, open source security, open source software, OWASP, software patching, Vulnerabilities

Post navigation

Previous Post: SonicWall Urges Patching of Critical SMA1000 Vulnerabilities
Next Post: OpenAI Astra AI Uncovers Zero-Day Security Threats

Related Posts

New Malware Toolkit Sends Users to Malicious Websites While the URL Stays the Same New Malware Toolkit Sends Users to Malicious Websites While the URL Stays the Same Cyber Security News
Infamous Cybercriminal Forum BreachForums Is Back Again With A New Clear Net Domain Infamous Cybercriminal Forum BreachForums Is Back Again With A New Clear Net Domain Cyber Security News
CISA Flags Critical Microsoft Defender Vulnerabilities CISA Flags Critical Microsoft Defender Vulnerabilities Cyber Security News
APT28 Exploits Microsoft Office Flaw in Cyber Attack APT28 Exploits Microsoft Office Flaw in Cyber Attack Cyber Security News
Oracle PeopleSoft Vulnerability Exploited by ShinyHunters Oracle PeopleSoft Vulnerability Exploited by ShinyHunters Cyber Security News
UTG-Q-1000 Group Weaponizing Subsidy Schemes to Exfiltrate Sensitive Data UTG-Q-1000 Group Weaponizing Subsidy Schemes to Exfiltrate Sensitive Data Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Mave Secures $34M to Advance AI-Driven Security Operations
  • OpenAI Enhances AI Model Security Amid Internet Challenges
  • AI to Detect Phishing in Microsoft Teams Conversations
  • Google AI Features May Influence Targeted Ads
  • LiteLLM Security Breach Exposes GitHub Tokens

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Mave Secures $34M to Advance AI-Driven Security Operations
  • OpenAI Enhances AI Model Security Amid Internet Challenges
  • AI to Detect Phishing in Microsoft Teams Conversations
  • Google AI Features May Influence Targeted Ads
  • LiteLLM Security Breach Exposes GitHub Tokens

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark