Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
AI Assists in Exploit Development for WAGO PLCs

AI Assists in Exploit Development for WAGO PLCs

Posted on September 2, 2026 By CWS

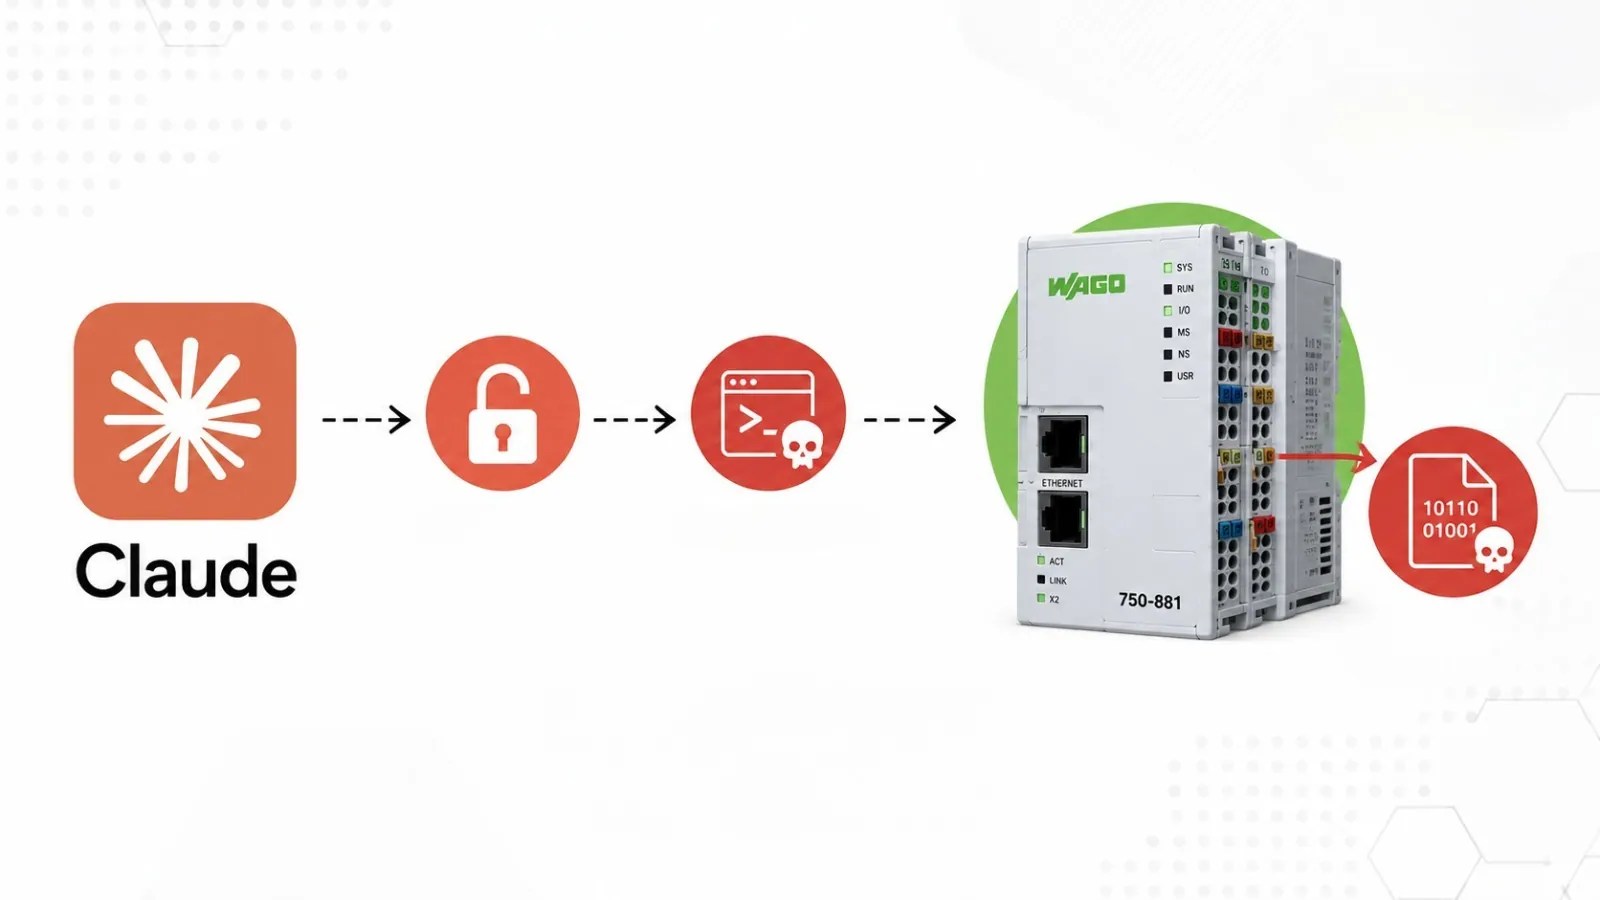
Recent research has demonstrated the capability of AI in crafting remote code execution (RCE) exploits for programmable logic controllers (PLCs). Utilizing Claude AI, researchers successfully ported an exploit to a WAGO 750-831 PLC, showcasing AI’s potential in low-level operational technology (OT) security applications.

AI’s Role in Exploit Development

The experiment focused on executing arbitrary ARM shellcode on a WAGO 750-831 without valid credentials, though it required significant human oversight, costly API usage, and ultimately resulted in a non-functional device. The targeted vulnerability, CVE-2021-31886, is a buffer overflow in the Nucleus FTP server, which arises from inadequate username length validation.

By crafting an oversized username, researchers could overwrite memory and redirect execution flow. The focus was on a WAGO 750-831 running firmware V01.04.16, building upon previous exploits for the WAGO 750-852 model. Claude AI was employed to pinpoint device-specific elements such as memory addresses and shellcode storage regions, critical for the exploit’s development.

Challenges and Breakthroughs

The closed-source nature of the PLC, lacking a debugger, posed unique challenges. Claude AI leveraged firmware analysis tools like Ghidra, Python scripts, and network utilities to dissect the firmware and engage with the controller. Initial AI attempts followed incorrect paths, necessitating human intervention to refine the approach.

The first success was a system crash, confirming the buffer overflow’s viability. However, achieving consistent RCE was complex due to the FTP command processing erasing critical buffers. By altering the command sequence from USER-QUIT to USER-CWD, Claude preserved the payload, enabling successful shellcode execution.

Implications and Recommendations

While AI expedited payload generation, including ICMP echo requests and UDP messages, the exploit required network access to FTP port 21 but bypassed authentication. The final stage of development cost $535.74 in API usage and involved extensive reverse engineering to understand shellcode overwriting issues.

Efforts to develop a command-and-control implant led to a bricked PLC due to a payload writing to flash memory, highlighting the risks of AI-driven testing on cyber-physical systems. The findings underscore AI’s potential in adapting embedded exploits, though expert oversight remains crucial.

To mitigate risks, organizations should limit FTP and remote management exposure, monitor PLCs for anomalies, and consider OT vulnerabilities as significant with AI-driven exploit development becoming more feasible.
Cyber Security News Tags:AI, Claude AI, CVE-2021-31886, cyber-physical security, Cybersecurity, embedded systems, Exploit, FTP vulnerability, network security, operational technology, PLC, remote code execution, reverse engineering, Shellcode, WAGO

Post navigation

Previous Post: Rockwell Automation Fixes Critical Software Vulnerabilities
Next Post: Security Flaws in AI Agents Allow Code Execution

Related Posts

Microsoft Confirms Teams Outage for Users, Investigation Underway Microsoft Confirms Teams Outage for Users, Investigation Underway Cyber Security News
Banana RAT Enhances Banking Malware with New Variants Banana RAT Enhances Banking Malware with New Variants Cyber Security News
New Android Malware ‘Fantasy Hub’ Intercepts SMS Messages, Contacts and Call Logs New Android Malware ‘Fantasy Hub’ Intercepts SMS Messages, Contacts and Call Logs Cyber Security News
Wireshark 4.6.6 Update Fixes Critical Security Flaw Wireshark 4.6.6 Update Fixes Critical Security Flaw Cyber Security News
UAT-638 Hackers Exploit Cityworks Zero-Day to Attack IIS Servers With VSHell Malware UAT-638 Hackers Exploit Cityworks Zero-Day to Attack IIS Servers With VSHell Malware Cyber Security News
Critical Docker Flaw Enables Host File Overwrite Critical Docker Flaw Enables Host File Overwrite Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Hackers Breach Microsoft 365 Using ConnectWise Backup
  • Israeli Firm’s Role in Global Spyware Campaign Uncovered
  • Malicious npm Package ‘imgdecode’ Found in Supply Chain Attack
  • Critical Flaw in Collabora Online Jeopardizes Nextcloud Security
  • Google Patches Chrome Flaws, Including Major Memory Issue

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Hackers Breach Microsoft 365 Using ConnectWise Backup
  • Israeli Firm’s Role in Global Spyware Campaign Uncovered
  • Malicious npm Package ‘imgdecode’ Found in Supply Chain Attack
  • Critical Flaw in Collabora Online Jeopardizes Nextcloud Security
  • Google Patches Chrome Flaws, Including Major Memory Issue

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark