Introduction to Tengu Malware
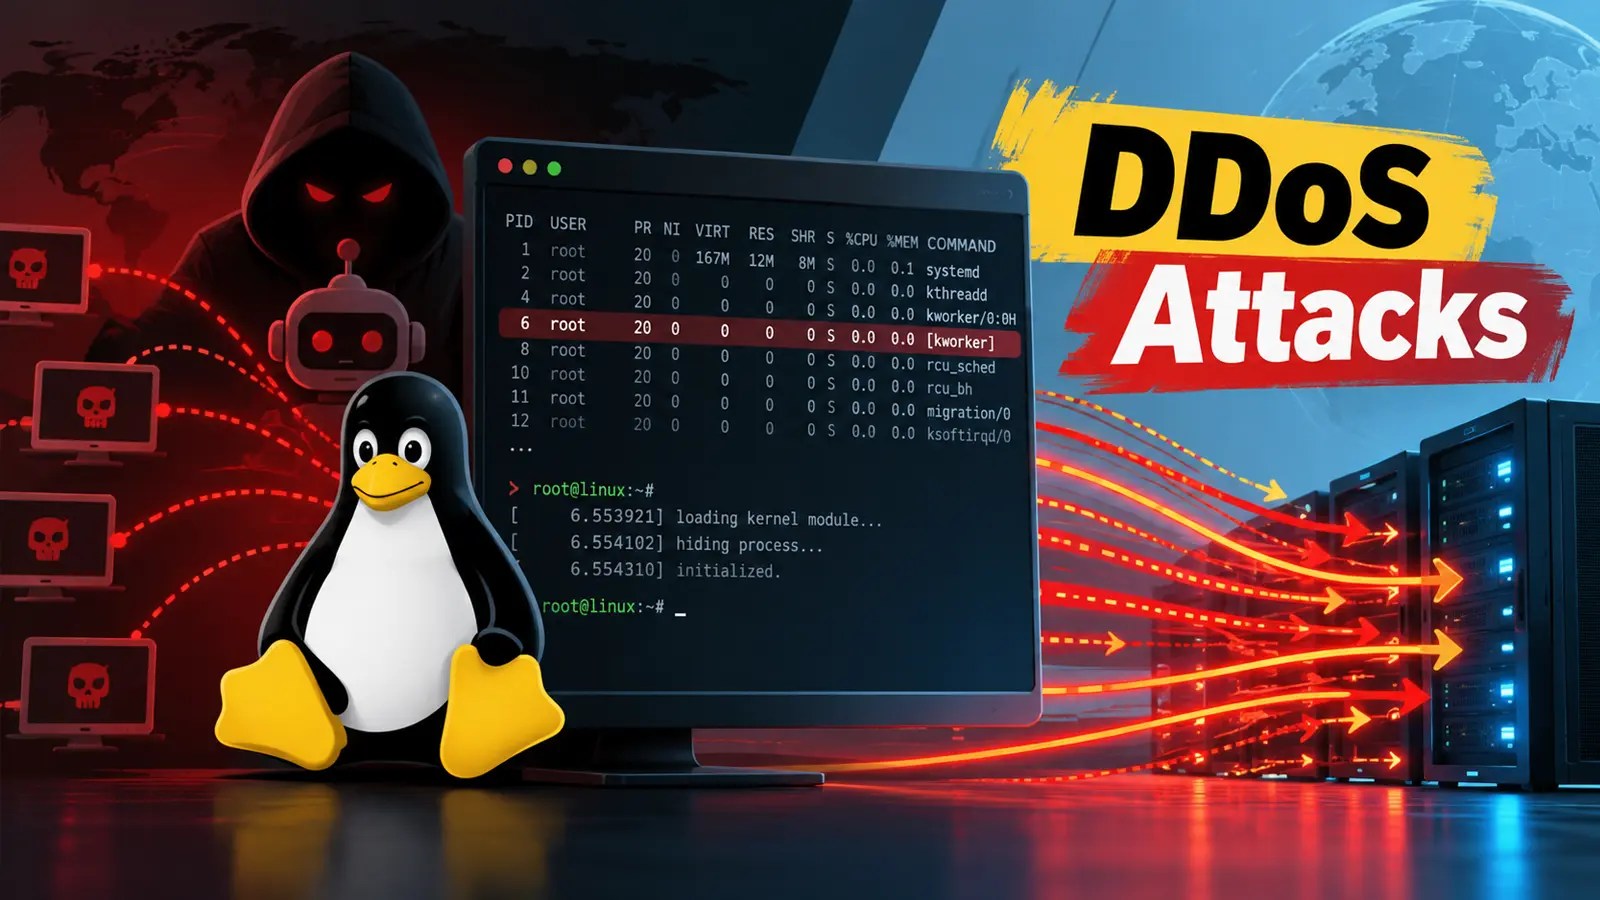
The emergence of a new Linux malware named Tengu is raising alarms in cybersecurity circles. This malicious bot is engineered to remain undetected, transforming compromised systems into instruments of attack. By masquerading as a typical kernel process, Tengu maintains persistence across diverse Linux environments and is capable of orchestrating distributed denial-of-service (DDoS) attacks.
Targeting both servers and IoT devices, Tengu presents a significant threat. Its capabilities extend beyond simple denial-of-service tools, utilizing raw UDP floods, SSH handshakes, and web-request generation to disrupt targeted networks. The exact method of initial compromise remains unknown, adding a layer of complexity to defense strategies.
Features and Persistence
Reverser.space’s analysis, shared with Cyber Security News, reveals that Tengu is a stripped, statically linked 32-bit Linux ELF, specifically designed for servers and IoT environments. Despite its complex feature set, its lineage to other malware like Mirai is not definitively established. However, its stealth and persistence mechanisms pose a significant threat.
Tengu’s ability to disguise itself as a kernel worker allows it to evade detection during standard system checks. The malware also ensures its survival through various startup scripts and services, making it difficult to eradicate once entrenched. This adaptability is critical in its operation across different platforms and systems.
Kernel Process Masquerading
To blend in with legitimate processes, Tengu adopts a randomized kernel-worker-style name. This deceptive tactic reduces its visibility in process listings. Furthermore, Tengu manipulates the operating system’s out-of-memory controls to avoid termination under memory pressure, ensuring its continuous operation.
The malware also manages to persist through reboots by leveraging systemd services, SysV scripts, and other startup mechanisms. This resilience was highlighted in reports of Tengu operations targeting internet-exposed embedded Linux devices, emphasizing its cross-platform reach.
DDoS and Network Disruption
Tengu’s DDoS capabilities include two modes of UDP attack. One mode creates raw IPv4 packets with customizable headers, while the other utilizes standard datagram sockets as a fallback. These tactics, combined with SSH handshake activities, enable it to exhaust network resources and disrupt web services.
Security teams must remain vigilant for unusual network behaviors, such as unexpected UDP traffic or SSH handshake anomalies. Monitoring for these indicators can help in early detection and mitigation of Tengu’s impacts.
Conclusion and Recommendations
The Tengu malware underscores the evolving threat landscape for Linux and IoT devices. Its stealth, persistence, and multifaceted attack strategies highlight the necessity for robust cybersecurity defenses. Administrators should isolate suspected infections, secure network access, and regularly update systems to mitigate risks.
Continuous monitoring for indicators of compromise, such as unexpected process names or network anomalies, is essential in identifying and neutralizing threats posed by Tengu. Proactive measures, including patching vulnerabilities and restricting unnecessary remote access, can further reduce the likelihood of new infections.