Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Ivanti Security Flaws Risk Privilege Escalation and RCE

Ivanti Security Flaws Risk Privilege Escalation and RCE

Posted on September 8, 2026 By CWS

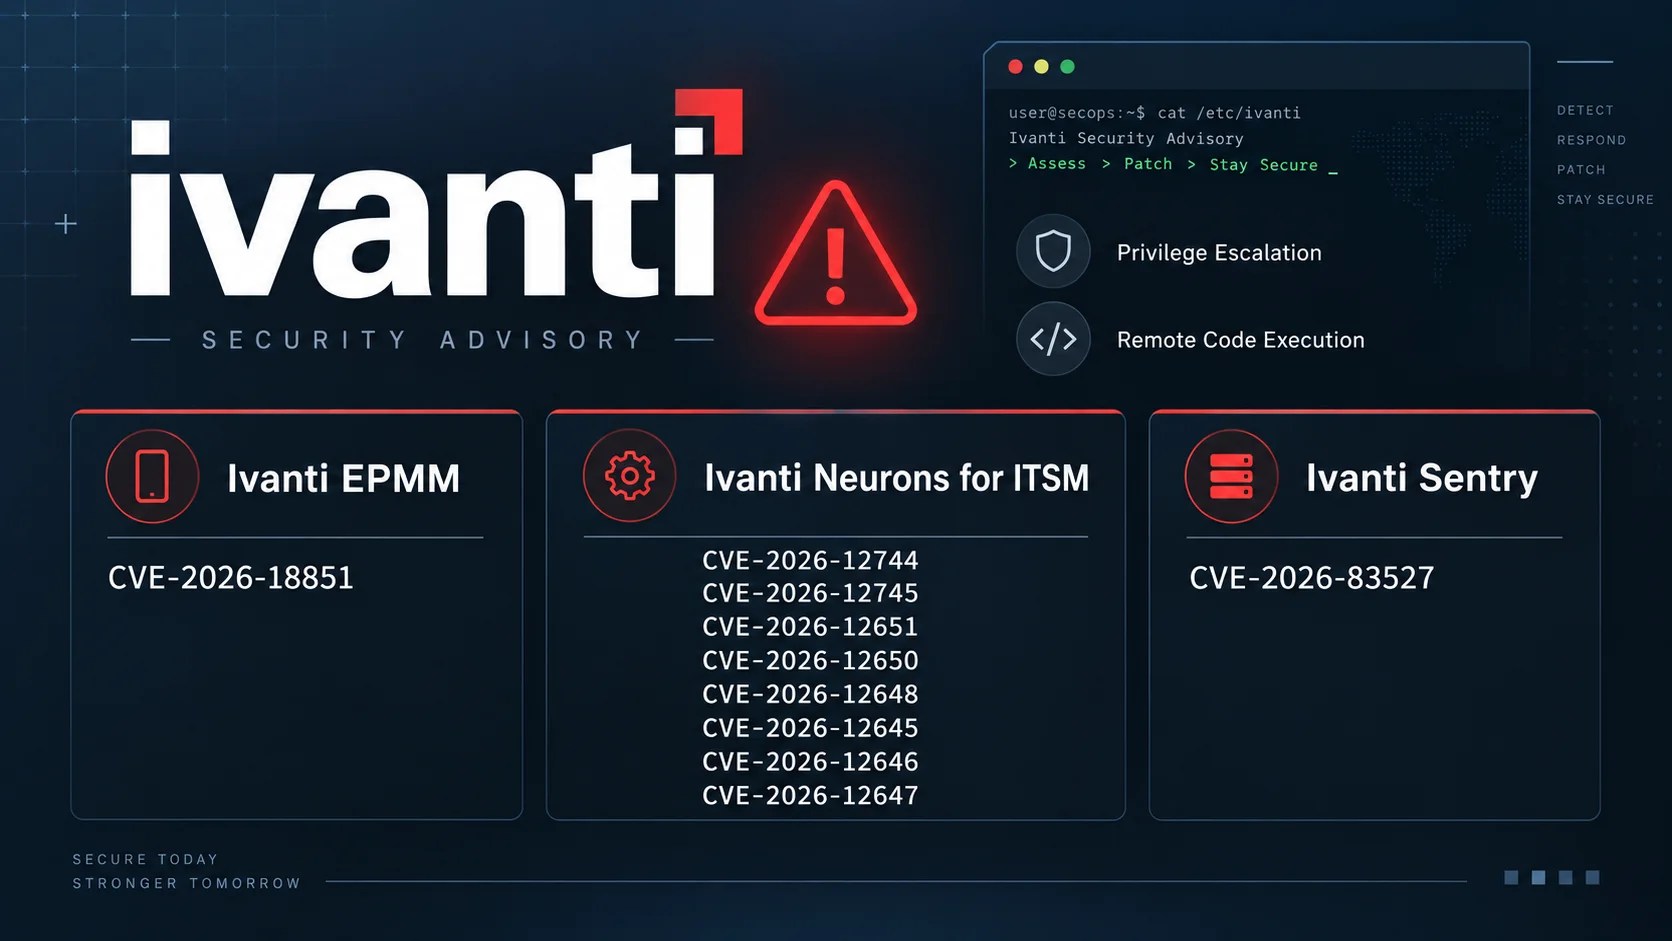
Ivanti has announced a series of critical security vulnerabilities affecting three major enterprise solutions: Endpoint Manager Mobile, Neurons for ITSM, and Sentry. These vulnerabilities pose significant risks, including privilege escalation and remote code execution (RCE), potentially impacting organizations worldwide.

Disclosed on September 8, 2026, these vulnerabilities span ten unique CVEs, several of which hold critical ratings. This wide-ranging exposure highlights the importance of addressing security issues within Ivanti’s mobile device management and IT service management platforms.

Detailed Analysis of EPMM Vulnerabilities

The first security advisory pertains to CVE-2026-18851, a high-severity flaw in Ivanti’s Endpoint Manager Mobile (EPMM). This missing authorization defect, assigned a CVSS score of 8.8, allows remote authenticated attackers to elevate privileges to administrator level. Affected versions include 12.9.0.1 and earlier, 12.8.0.3 and earlier, with remediation provided in updates 12.10.0.0, 12.9.0.2, and 12.8.0.4.

Ivanti has strongly recommended that organizations implement these patches to mitigate potential exploitation risks, particularly for internet-connected instances of EPMM.

Neurons for ITSM: Critical Security Concerns

Ivanti’s Neurons for ITSM has been identified as having eight distinct vulnerabilities. Among these, CVE-2026-12744 and CVE-2026-12745 are the most severe, both involving the deserialization of untrusted data (CWE-502). These flaws could be exploited by unauthenticated attackers to execute arbitrary code, each carrying a critical rating of 9.8.

Additional deserialization vulnerabilities, CVE-2026-12651, CVE-2026-12650, and CVE-2026-12648, necessitate authentication but still enable RCE. Three missing authorization flaws, CVE-2026-12645, CVE-2026-12646, and CVE-2026-12647, also allow authenticated RCE, each rated at 9.9 in severity. Ivanti has patched these issues in cloud deployments with on-premises updates scheduled.

Impacts on Ivanti Sentry and Response Measures

Another significant vulnerability, CVE-2026-83527, affects Ivanti Sentry, managed via EPMM and Neurons for MDM. This authentication bypass flaw, with a CVSS score of 8.1, enables remote unauthenticated attackers to gain administrative access. Fixed versions R10.8.2, R10.7.3, and R10.6.4 have been released to address this issue.

Ivanti has confirmed no evidence of active exploitation of these vulnerabilities prior to their disclosure. Nonetheless, due to the historical targeting of Ivanti’s management infrastructure, security teams are advised to prioritize patching, especially for Neurons for ITSM instances exposed to the internet.

The company credits advanced AI models integrated into its security workflows for the discovery of these vulnerabilities, underscoring the role of AI in enhancing cybersecurity measures.
Cyber Security News Tags:AI vulnerability detection, authentication bypass, CVE, cybersecurity news, deserialization flaws, enterprise security, EPMM, ITSM, Ivanti, patch management, privilege escalation, remote code execution, security vulnerabilities, Sentry

Post navigation

Previous Post: CISA Alerts on Active Chromium Vulnerability Exploitation
Next Post: Critical Flaws in Dell Gateway Pose Severe Security Risks

Related Posts

Hackers Breaking Internet with 7.3 Tbps and 4.8 Billion Packets Per Second DDoS Attack Hackers Breaking Internet with 7.3 Tbps and 4.8 Billion Packets Per Second DDoS Attack Cyber Security News
KillSec Ransomware Attacking Healthcare Industry IT Systems KillSec Ransomware Attacking Healthcare Industry IT Systems Cyber Security News
Telegram’s t.me Domain Suspension Disrupts Global Links Telegram’s t.me Domain Suspension Disrupts Global Links Cyber Security News
New Attack Technique That Enables Attackers To Exfiltrate Git Credentials In Argocd New Attack Technique That Enables Attackers To Exfiltrate Git Credentials In Argocd Cyber Security News
Adware Conceals ValleyRAT Backdoor in China and India Adware Conceals ValleyRAT Backdoor in China and India Cyber Security News
Microsoft Unveils Kazuar Malware’s Advanced Design Microsoft Unveils Kazuar Malware’s Advanced Design Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Google AI Features May Influence Targeted Ads
  • LiteLLM Security Breach Exposes GitHub Tokens
  • Brotli Decoder Flaw Impacts Major Software Platforms
  • Security Firm Halts Botnet Threat from Popcorn Time Updater
  • PHP Vulnerabilities Impact Palo Alto PAN-OS Systems

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Google AI Features May Influence Targeted Ads
  • LiteLLM Security Breach Exposes GitHub Tokens
  • Brotli Decoder Flaw Impacts Major Software Platforms
  • Security Firm Halts Botnet Threat from Popcorn Time Updater
  • PHP Vulnerabilities Impact Palo Alto PAN-OS Systems

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark