Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Ukrainian Hacker Sentenced for Role in Conti Ransomware

Ukrainian Hacker Sentenced for Role in Conti Ransomware

Posted on September 11, 2026 By CWS

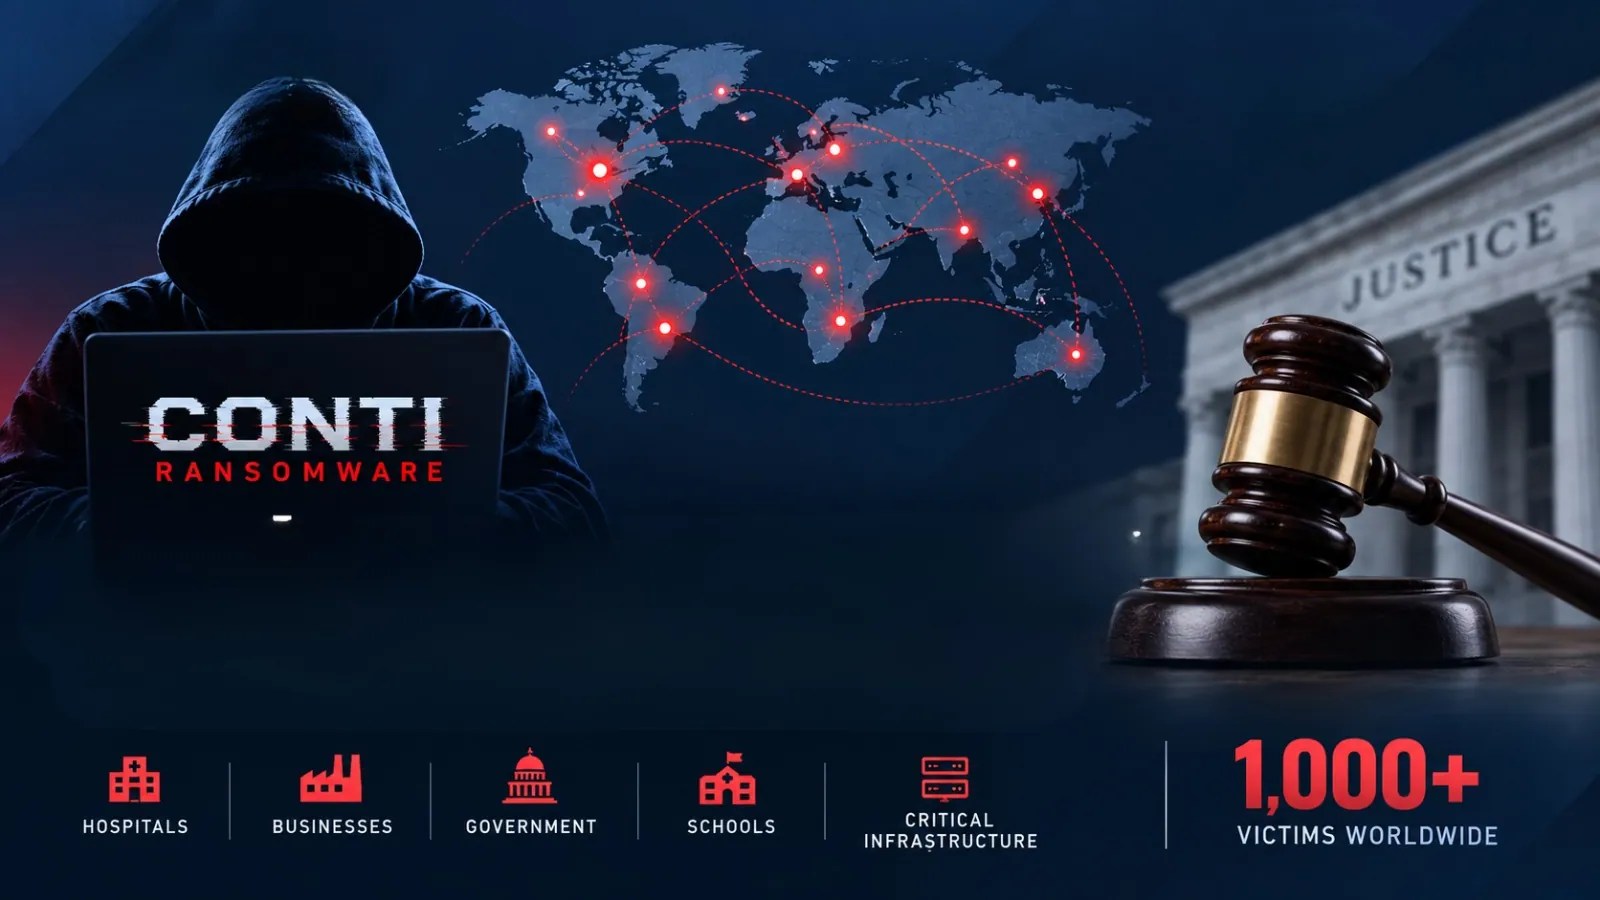
A Ukrainian hacker has been sentenced to four years in a U.S. prison for his involvement in the notorious Conti ransomware scheme. This operation affected over 1,000 victims globally, resulting in at least $150 million in ransom collections.

Details of the Sentencing

Oleksii Oleksiyovych Lytvynenko, aged 44, who previously resided in Cork, Ireland, received his sentence for conspiracy to commit wire fraud. According to U.S. prosecutors, Lytvynenko collaborated with other members of the Conti group to execute ransomware attacks, exfiltrate sensitive data, and extort funds from impacted entities.

The Conti ransomware operation emerged as one of the most disruptive cyber threats from 2020 to 2022. Its targets included corporate entities, healthcare institutions, educational facilities, local governments, and other critical infrastructure sectors. The group’s reach extended to 47 U.S. states, the District of Columbia, Puerto Rico, and 31 countries outside the U.S.

Impact and Financial Damage

By January 2022, the FBI estimated that victims of the Conti group had collectively paid over $150 million in ransom. Experts believe the actual economic impact was much greater, considering associated costs such as ransom demands, recovery expenses, incident response, business interruption, data theft, and damage to reputations.

Court documents revealed that Lytvynenko possessed data stolen from 12 different Conti victims, including eight based in the United States and four international entities. Investigators unearthed evidence from his digital accounts, linking him to the handling and storage of stolen victim data.

Technical Involvement and Operation Resilience

Lytvynenko admitted to participating in a technical team managed by another Conti conspirator, where he was responsible for developing a malware “loader”. This tool was integral to deploying additional malicious software on compromised networks.

In ransomware operations, loaders play crucial roles by deploying payloads, establishing persistence, and launching ransomware across enterprise infrastructures. Forensic evidence obtained at the time of Lytvynenko’s arrest in County Cork, Ireland, in July 2023, indicated his continued involvement in ransomware activities even after the dissolution of the original Conti operation. He pleaded guilty to conspiracy to commit wire fraud in June 2026.

Broader Implications and Ongoing Investigations

This sentencing is part of a larger investigation by U.S. authorities into the Conti and TrickBot cybercriminal networks. In September 2023, charges were unsealed against four additional foreign nationals allegedly linked to the malware and ransomware conspiracy.

The investigation was spearheaded by FBI field offices in San Diego, Nashville, and El Paso, with assistance from the U.S. Secret Service and Homeland Security Investigations. Irish law enforcement played a key role in Lytvynenko’s arrest and extradition.

This conviction underscores the ongoing international effort to combat ransomware operators and developers. U.S. officials have reiterated that cybercriminals involved in orchestrating or benefiting from ransomware attacks can be prosecuted, regardless of their location.

Cyber Security News Tags:Conti operation, Conti Ransomware, cyber attack, cybercrime sentencing, Cybersecurity, FBI investigation, hacker sentencing, international cooperation, international cybercrime, Lytvynenko, Malware, ransomware attack, ransomware ecosystem, U.S. prosecution, wire fraud

Post navigation

Previous Post: Weekly Cybersecurity Update: Key Threats and Developments
Next Post: AI Exploited in Cyber Attacks Across the Globe

Related Posts

Critical Backdoor in WordPress Plugin Exposes Admin Access Critical Backdoor in WordPress Plugin Exposes Admin Access Cyber Security News
GhostApproval Flaw in Popular AI Coding Tools Raises Security Concerns GhostApproval Flaw in Popular AI Coding Tools Raises Security Concerns Cyber Security News
WhatsApp Introduces Handles for Enhanced Privacy WhatsApp Introduces Handles for Enhanced Privacy Cyber Security News
Turkish Banks Hit by Extensive Phishing and Scam Ads Turkish Banks Hit by Extensive Phishing and Scam Ads Cyber Security News
Microsoft 365 Services and Copilot Outage Hits Users in Japan and China Microsoft 365 Services and Copilot Outage Hits Users in Japan and China Cyber Security News
Ransomware Campaign Mimics Akira in South America Ransomware Campaign Mimics Akira in South America Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Hackers Exploit Instagram Ads to Deliver iPhone Spyware
  • CISA Alerts on Exploitation of Critical PHP Vulnerabilities
  • Hackers Exploit Claude’s Site and Ads for Malware Spread
  • Apache Camel Resolves Critical Vulnerabilities
  • Exploit Targets WordPress Admin Sessions with PHP Backdoor

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Hackers Exploit Instagram Ads to Deliver iPhone Spyware
  • CISA Alerts on Exploitation of Critical PHP Vulnerabilities
  • Hackers Exploit Claude’s Site and Ads for Malware Spread
  • Apache Camel Resolves Critical Vulnerabilities
  • Exploit Targets WordPress Admin Sessions with PHP Backdoor

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark