Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Exploited PaperCut Server Breach Exposes Critical Flaws

Exploited PaperCut Server Breach Exposes Critical Flaws

Posted on October 1, 2026 By CWS

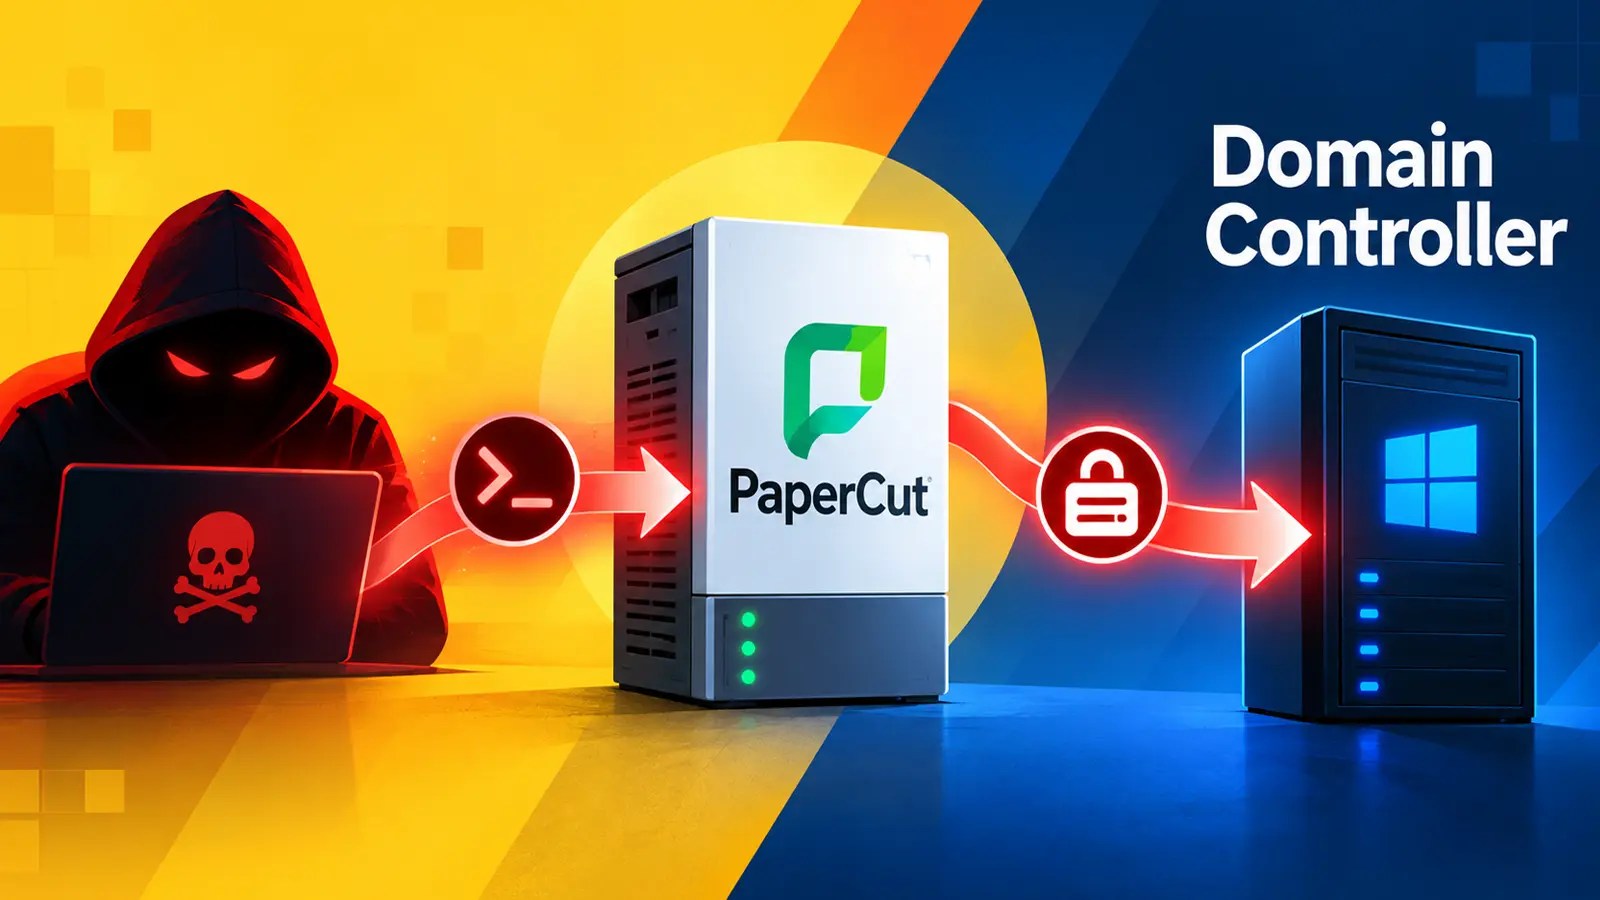
A recent cyber attack on a PaperCut print server has highlighted significant vulnerabilities in enterprise identity systems. Attackers took advantage of two zero-day vulnerabilities in the PaperCut MF software, leading to a compromise of the Active Directory infrastructure. This incident underscores the critical need for businesses to protect seemingly mundane systems from becoming gateways for cybercriminals.

Exploiting Vulnerabilities in Print Servers

The attack began with the exploitation of a PaperCut MF server, specifically version 24.0.2, build 69746, which was exposed to the internet. Hackers utilized the card or ID lookup feature to inject malicious Java code, allowing them to install an in-memory loader and web shell. This setup facilitated the deployment of an AdaptixC2 implant, cleverly disguised as a modified Microsoft Copilot binary.

According to a report by eSentire shared with Cyber Security News, the breach was detected on August 31, 2026, affecting an education sector client. Within two days, attackers moved from the compromised print server to the organization’s domain controller, illustrating the rapid escalation potential of such attacks.

Impact and Implications of the Breach

The incident highlights the risks associated with leaving management applications exposed to the internet. The vulnerabilities, identified as CVE-2026-81578 and CVE-2026-82078, allowed attackers to modify settings and execute arbitrary Java bytecode without authentication. The initial loader was compatible with various Tomcat versions, enabling it to construct payloads in memory and execute subsequent attack stages.

Once access was established, the attackers meticulously erased logs and traces of their presence, ensuring their activities went undiscovered for as long as possible. This strategic concealment allowed them to maintain control over the compromised server while preventing other parties from exploiting the same vulnerabilities.

Credential Theft and Mitigation Strategies

In the attack’s final phase, the perpetrators assessed the network environment, identifying privileged accounts to exploit. They duplicated an access token from a domain-privileged service account, which allowed them to execute their implant with elevated privileges. This maneuver enabled them to copy their payload to the domain controller efficiently.

To mitigate the impact of such attacks, administrators are urged to update PaperCut MF or NG software to the latest version and limit access to trusted IP addresses only. It is crucial to monitor child processes, check for missing or truncated server logs, and identify unusual post-exploitation behavior. Applying vendor patches promptly and reviewing service configurations for unexpected changes are also recommended actions.

In conclusion, this breach serves as a stark reminder of the importance of securing all parts of an organization’s IT infrastructure. Security teams must remain vigilant, ensuring systems are updated and access is tightly controlled to prevent similar incidents in the future.
Cyber Security News Tags:Active Directory, credential theft, Cybersecurity, domain controller, identity infrastructure, IT security, Java code exploitation, PaperCut, server breach, zero-day vulnerabilities

Post navigation

Previous Post: AI Agents Expose 13,000 Screenshots from 300 Firms
Next Post: Citrix NetScaler Vulnerability Exploited by Threat Actors

Related Posts

Developing Collaborative Threat Intelligence Sharing Frameworks Developing Collaborative Threat Intelligence Sharing Frameworks Cyber Security News
CrowdStrike Debuts SafeMind: Innovative AI Cybersecurity CrowdStrike Debuts SafeMind: Innovative AI Cybersecurity Cyber Security News
Fake Jev AI Stores Exploit Users with Costly Access Fake Jev AI Stores Exploit Users with Costly Access Cyber Security News
As Third-Party Vulnerabilities Rise, CISOs Accelerate Push for Security Modernization   As Third-Party Vulnerabilities Rise, CISOs Accelerate Push for Security Modernization   Cyber Security News
Social Engineering Attack Compromises Popular Axios Library Social Engineering Attack Compromises Popular Axios Library Cyber Security News
GlassWorm Exploits VSX Extensions to Target Developers GlassWorm Exploits VSX Extensions to Target Developers Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Cloudflare to Offer Free Digital Certificates Globally
  • Warlock Group Intensifies SharePoint Attacks on Key Sectors
  • Kiteworks Enhances Security with Major Update Fixing 126 Vulnerabilities
  • AI Agents Target US and Canadian Government Websites
  • U.S. Treasury Takes Action Against ATM Jackpotting Ring

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Cloudflare to Offer Free Digital Certificates Globally
  • Warlock Group Intensifies SharePoint Attacks on Key Sectors
  • Kiteworks Enhances Security with Major Update Fixing 126 Vulnerabilities
  • AI Agents Target US and Canadian Government Websites
  • U.S. Treasury Takes Action Against ATM Jackpotting Ring

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark