Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Adobe Addresses Critical PDF Flaw Allowing Memory Corruption

Adobe Addresses Critical PDF Flaw Allowing Memory Corruption

Posted on October 16, 2026 By CWS

Adobe has recently addressed a significant vulnerability in its Acrobat and Acrobat Reader software, which allowed malicious PDF files to induce memory corruption when opened. Identified as CVE-2026-81983, this out-of-bounds write vulnerability was assigned a CVSS score of 7.8, indicating a high risk of code execution under the user’s permissions.

Details of the Vulnerability

Although Adobe has not observed active exploitation of this flaw, it was discovered within Acrobat’s image processing pipeline. This segment of the code begins parsing image data immediately upon opening a PDF. Researchers utilized a custom Python-based fuzzer, designed with the assistance of a large language model, to identify this issue. Instead of altering complete PDF files, the tool generated small, valid documents, focusing on image parameters like width, height, bit depth, color space, and sample bytes.

The investigation revealed that the most severe crash was caused by a crafted 16-bit image, merely 745 bytes in size. The underlying issue was traced to a 32-bit integer overflow within Acrobat.dll, where the software miscalculates the number of image samples by multiplying the image width and the color component count.

Mechanics of the Exploit

The vulnerability stems from a size calculation error that adds two bytes for each 16-bit sample. With a large image width, this value could wrap around to a smaller number, misleading Acrobat into accepting a very short data stream. The byte-swap loop continues to process a large sample count, reading and writing beyond the buffer limits and causing memory corruption, potentially allowing an attacker to execute arbitrary code.

A proof-of-concept demonstrated this with a width of 536,870,912, a single height unit, 16 bits per color component, and the DeviceCMYK color space. These parameters resulted in a sample count of 0x80000000, which the size check erroneously approved.

Security Measures and Recommendations

Adobe addressed this issue by implementing 64-bit arithmetic for sample count calculations and rejecting values exceeding INT_MAX before they affect memory. This fix was released in security bulletin APSB26-141 on September 8, 2026. Updated versions, including Acrobat and Reader Continuous 26.002.21901 and Acrobat 2024 Classic 24.001.30429, are now available.

Users are advised to update immediately, enable automatic updates, and exercise caution with unexpected PDF attachments. Security teams should filter suspicious PDFs at email gateways and monitor for Acrobat.dll-related crashes. The CVE-2026-81983 vulnerability is labeled critical, with the NVD confirming that exploitation requires user interaction with a crafted file.

This discovery underscores the effectiveness of AI-assisted fuzzing in uncovering deep-seated bugs in legacy file parsers. It also highlights the importance of maintaining robust defenses against emerging malware threats and integrating threat intelligence feeds from various sources for comprehensive security.

Cyber Security News Tags:Acrobat, Adobe, AI-assisted fuzzing, CVE-2026-81983, Cybersecurity, memory corruption, PDF, Security, software update, Vulnerability

Post navigation

Previous Post: Proofpoint to Acquire Varonis in $6.3 Billion Deal
Next Post: CERT-In Alerts on AI Agents Accessing Sensitive Data

Related Posts

McGraw-Hill Data Breach Exposes 13.5 Million Users McGraw-Hill Data Breach Exposes 13.5 Million Users Cyber Security News
Hackers Exploit Search Engines with Phishing Pages Hackers Exploit Search Engines with Phishing Pages Cyber Security News
Cisco Nexus Dashboard Fabric Controller Vulnerability Allows Attackers Device Impersonate as Managed Devices Cisco Nexus Dashboard Fabric Controller Vulnerability Allows Attackers Device Impersonate as Managed Devices Cyber Security News
Criminal IP to Showcase ASM and CTI Innovations at GovWare 2025 in Singapore Criminal IP to Showcase ASM and CTI Innovations at GovWare 2025 in Singapore Cyber Security News
Remote Code Execution Risk in Telnetd Impacts Security Remote Code Execution Risk in Telnetd Impacts Security Cyber Security News
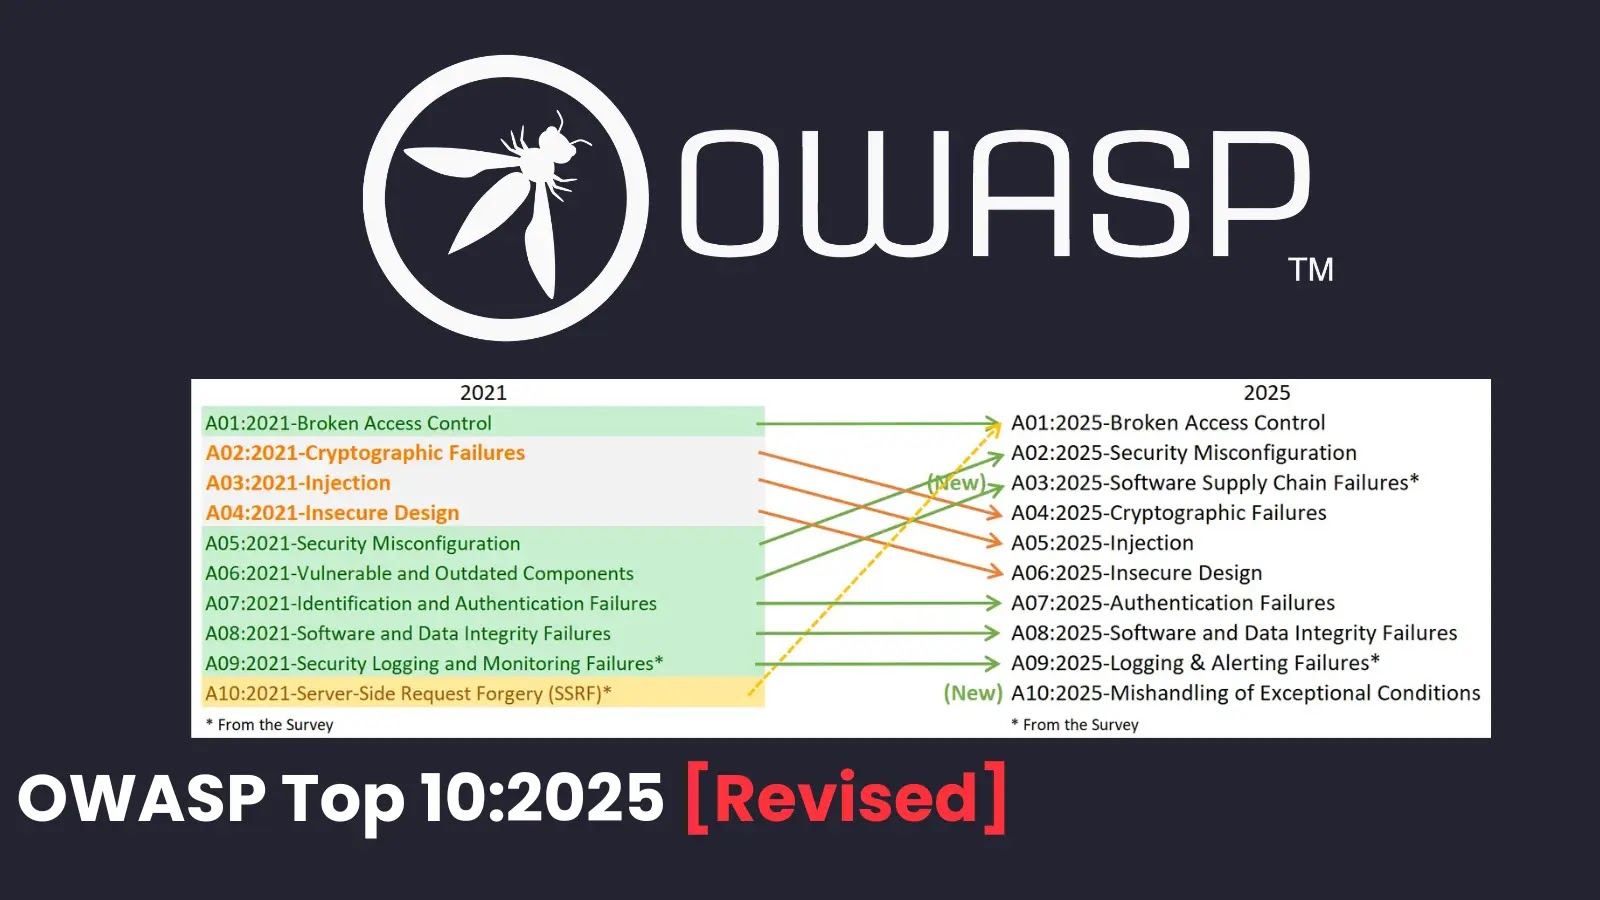
OWASP Top 10 2025 – Revised Version Released With Two New Categories OWASP Top 10 2025 – Revised Version Released With Two New Categories Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Leading Data Classification Tools for 2026 Unveiled
  • Microsoft Addresses RCE Vulnerabilities in Office Suite
  • CERT-In Alerts on AI Agents Accessing Sensitive Data
  • Adobe Addresses Critical PDF Flaw Allowing Memory Corruption
  • Proofpoint to Acquire Varonis in $6.3 Billion Deal

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Leading Data Classification Tools for 2026 Unveiled
  • Microsoft Addresses RCE Vulnerabilities in Office Suite
  • CERT-In Alerts on AI Agents Accessing Sensitive Data
  • Adobe Addresses Critical PDF Flaw Allowing Memory Corruption
  • Proofpoint to Acquire Varonis in $6.3 Billion Deal

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark