Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
TeamViewer Flaw Risks Remote Support Security Breach

TeamViewer Flaw Risks Remote Support Security Breach

Posted on October 31, 2026 By CWS

A recent security vulnerability discovered in TeamViewer poses a serious risk to remote support sessions. This flaw, identified as CVE-2026-111585, could allow an attacker to crash the viewer application and execute code on the support technician’s device. TeamViewer has rated this vulnerability as high with a CVSS score of 8.8, indicating significant potential impact.

Understanding the TeamViewer Vulnerability

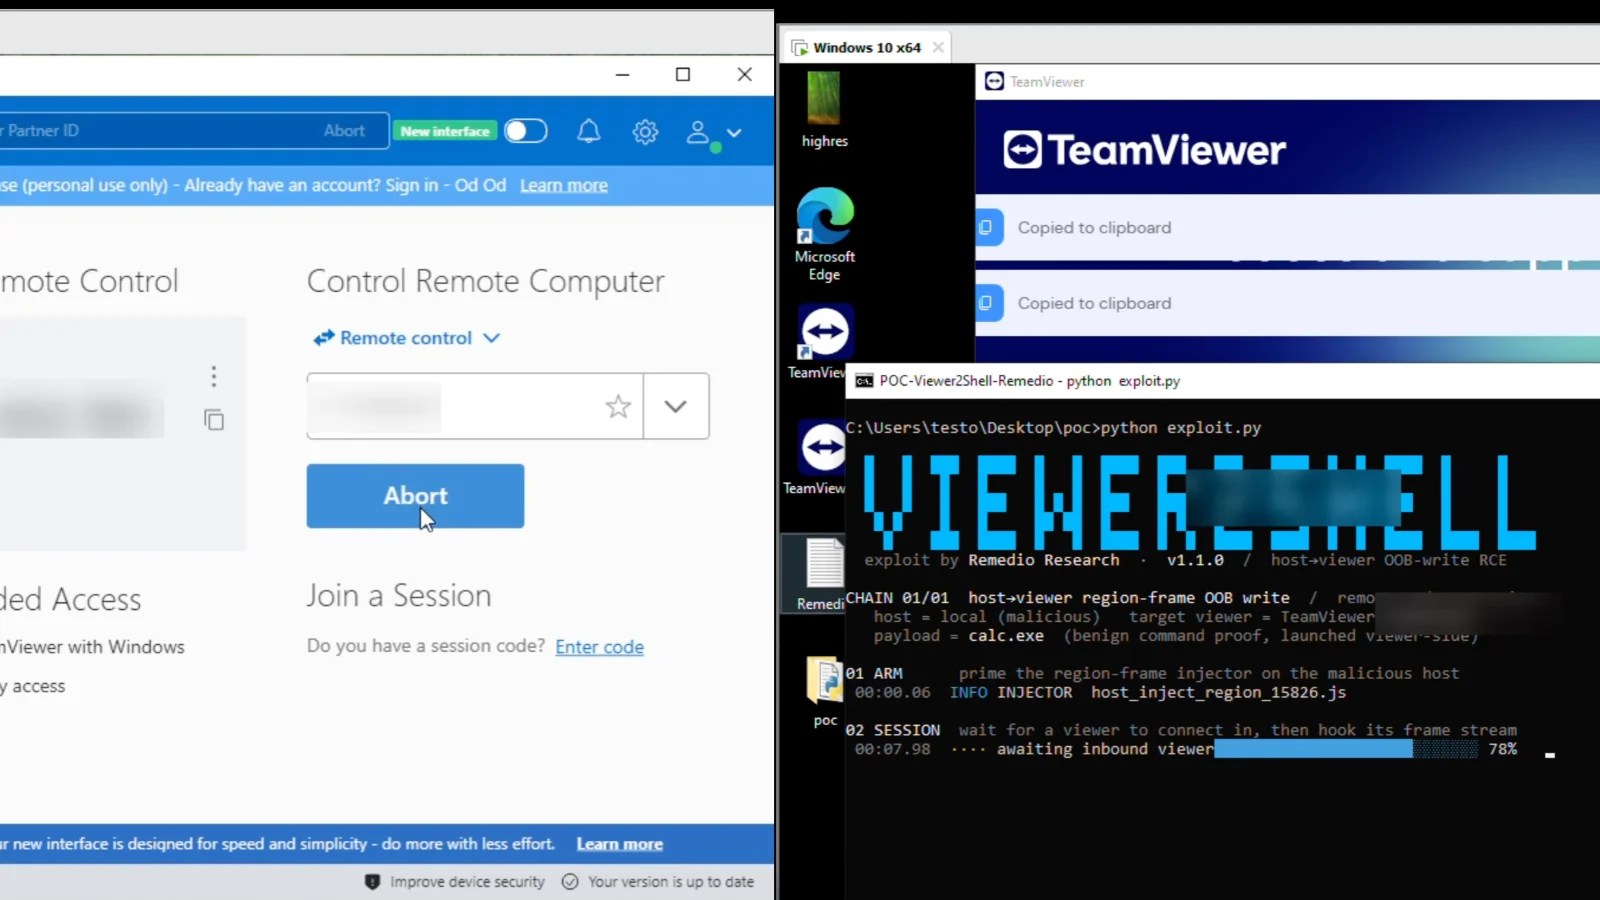
Researcher Omri Dar from Remedio disclosed the technical details of this vulnerability on October 29, shortly after TeamViewer released a fix on October 27. The attack requires the victim to initiate a remote session with a compromised or attacker-controlled host. Notably, no additional user interaction is necessary once the connection is established.

The vulnerability arises from TeamViewer’s session architecture, which divides the connection into a host that shares the screen and a viewer that displays it. In this scenario, a host can exploit the connection by sending crafted screen data, endangering the technician’s machine instead of the host.

Technical Details and Exploitation

The attack involves the host sending a DisplayParams message, which includes details like screen dimensions and color depth. The viewer uses this data to allocate memory for incoming pixel updates within a component called CBitmapBuffer. A malicious host can force the viewer to process bitmap updates by rejecting AV1 and H.264 video options.

The problem lies in the 32-bit arithmetic used to calculate buffer size. When oversized screen dimensions are declared, the calculation wraps around, allocating significantly less memory than required. As a result, there is a discrepancy between the declared screen size and the actual memory allocation, allowing data to overflow into adjacent memory spaces.

Affected Versions and Mitigation Steps

TeamViewer’s security bulletin TV-2026-1011 outlines the affected versions, which include Full Client versions prior to 15.83 across Windows, Linux, and macOS, as well as Windows Portable and Android Remote Control. Exploitation depends on the platform and is limited to the viewer process’s permissions.

Administrators are urged to update to version 15.83 or the latest available version to mitigate this risk. This update is crucial for all support workstations and legacy systems that may not follow regular update protocols. While there have been no known active exploitations reported at the time of the bulletin’s release, updating remains a priority to safeguard against potential threats.

As AI technology accelerates the pace and reduces the cost of cyberattacks, ensuring robust defenses capable of responding at machine speed is more critical than ever. Support teams should prioritize system updates and maintain vigilance when connecting to potentially untrusted systems.

Cyber Security News Tags:code execution, CVE-2026-111585, Cybersecurity, IT security, remote desktop, Remote Support, security flaw, software update, TeamViewer, Vulnerability

Post navigation

Previous Post: Apple Alerts iPhone Users Globally to New Spyware Threats
Next Post: New ChatGPT Flaw Exposed: Attackers Could Access Private Chats

Related Posts

Hackers Exploit AI Platforms for Sophisticated Attacks Hackers Exploit AI Platforms for Sophisticated Attacks Cyber Security News
Attackers Reverse‑Engineer Patch to Exploit SmarterMail Admin Bypass in the Wild Attackers Reverse‑Engineer Patch to Exploit SmarterMail Admin Bypass in the Wild Cyber Security News
PHP Developer Community Threatened by Malicious Packages PHP Developer Community Threatened by Malicious Packages Cyber Security News
Odido Data Breach Exposes 1 Million Records After Cyberattack Odido Data Breach Exposes 1 Million Records After Cyberattack Cyber Security News
Critical Cisco SD-WAN Flaw Exploited by Hackers to Deploy Malware Critical Cisco SD-WAN Flaw Exploited by Hackers to Deploy Malware Cyber Security News
How Businesses Prevent Credential Theft with Early Phishing Detection How Businesses Prevent Credential Theft with Early Phishing Detection Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • WordPress RCE Vulnerability Exploited in Thousands of Attacks
  • New ChatGPT Flaw Exposed: Attackers Could Access Private Chats
  • TeamViewer Flaw Risks Remote Support Security Breach
  • Apple Alerts iPhone Users Globally to New Spyware Threats
  • Critical Flaw in Drupal Commerce Threatens Online Stores

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • WordPress RCE Vulnerability Exploited in Thousands of Attacks
  • New ChatGPT Flaw Exposed: Attackers Could Access Private Chats
  • TeamViewer Flaw Risks Remote Support Security Breach
  • Apple Alerts iPhone Users Globally to New Spyware Threats
  • Critical Flaw in Drupal Commerce Threatens Online Stores

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark