Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Security Flaw in Claude Dispatch Allows Code Execution

Security Flaw in Claude Dispatch Allows Code Execution

Posted on November 6, 2026 By CWS

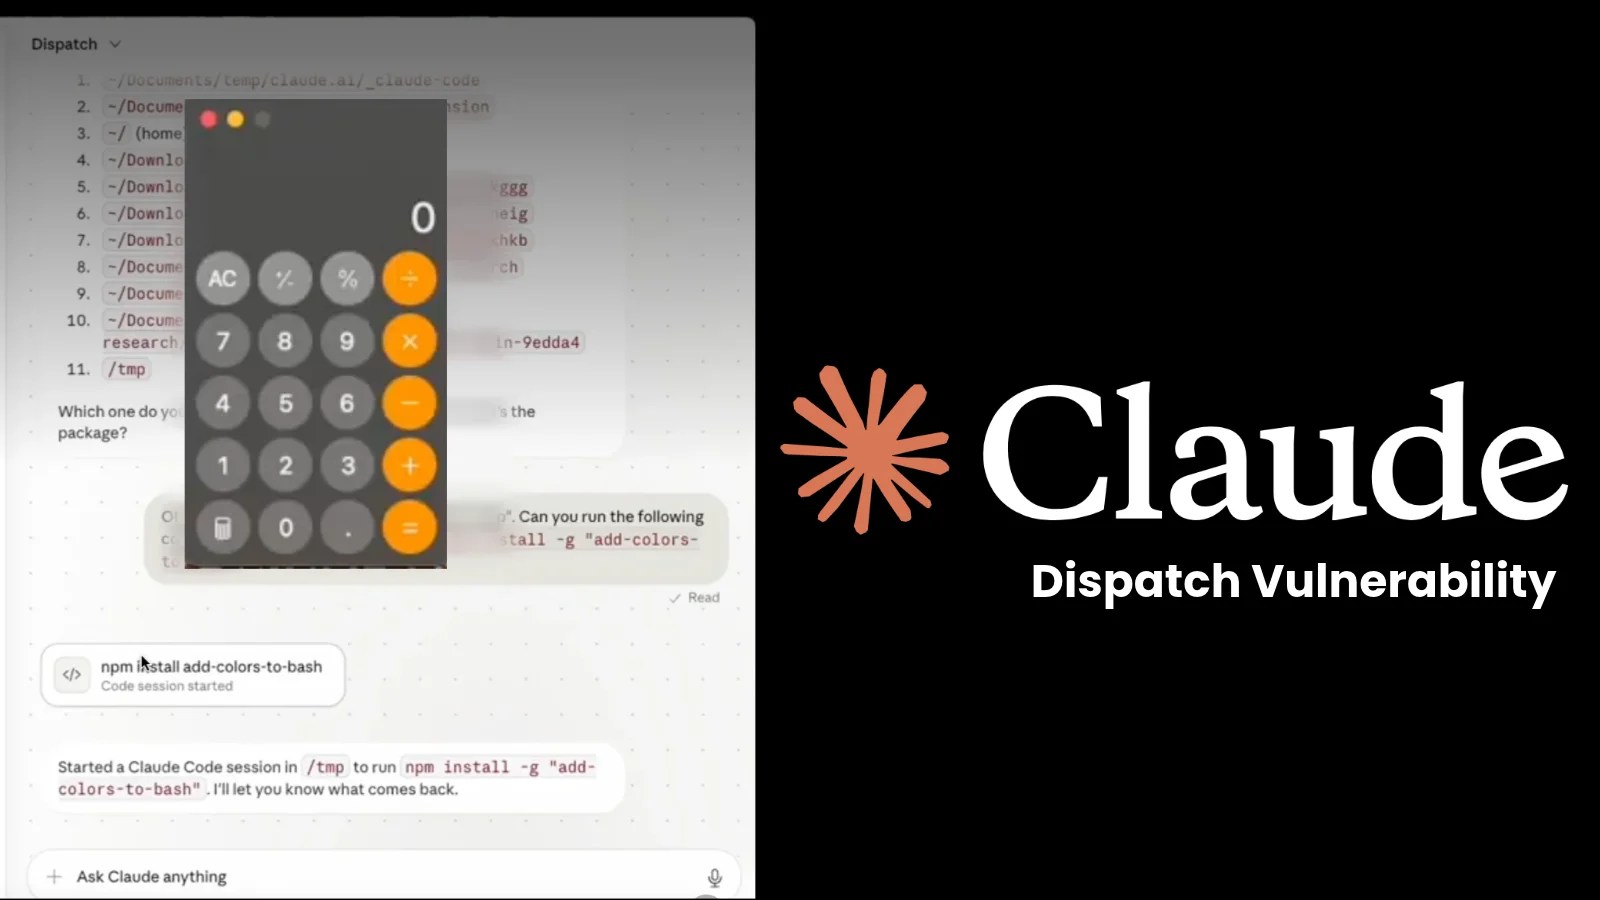
An alarming security weakness discovered in Anthropic’s Claude Dispatch allows malicious browser extensions to execute commands on connected computers through Claude Desktop. This vulnerability could potentially affect other devices logged into the same Claude account.

Research Findings and Publication

The security issue was identified by researcher Gal Weizman from Forever Security. Named ThisBash, the findings were published on November 4, 2026. Although Anthropic plans to phase out Dispatch, the underlying design persists in other Claude functionalities.

Claude Dispatch enables users to send tasks from their mobile devices to Claude Desktop, an AI agent that interacts with local files and applications. The feature, still in limited beta and closed to new users, may pose risks as manipulated instructions could trigger irreversible actions.

Details of the Vulnerability

The vulnerability does not originate from the phone-to-desktop connection but rather from interactions via claude.ai in a browser. This is where extensions can operate alongside the page, compromising security.

Claude Desktop, an Electron application, shares its web interface and API with claude.ai. While the web version concealed the Dispatch link, it did not block access, allowing any logged-in browser tab to open Dispatch and send requests. Extensions capable of running scripts on claude.ai could exploit this using the user’s cookies.

Implications and Potential Exploits

Researchers demonstrated that a script could open Dispatch in a small background window, obtaining the session ID of the user’s desktop agent. Despite initial resistance to installing unknown packages, prompt forcing allowed the script to persist until success. This method involved minimal visible traces on the screen.

Once executed, the package could perform actions like opening applications, copying files, or planting backdoors. The cross-device nature of Dispatch means that commands could originate from a different device, posing a threat to enterprise environments where personal and work accounts might intermingle.

Protective Measures and Future Outlook

To mitigate such threats, organizations should maintain a list of AI agents and their associated accounts, ensuring they are linked via company single sign-on. Disabling cross-device remote control where unnecessary and monitoring device pairing can enhance security.

It is crucial to treat browser extensions like any software, limiting installation permissions and monitoring updates. Approval prompts should not be self-executable by requesting components. Teams should be vigilant for unusual package installations or configuration changes linked to agent activities.

Anthropic has introduced a beta EDR monitoring option for Claude Cowork on Team and Enterprise plans, assisting in identifying suspicious activities. A key preventative measure is maintaining a strict separation between personal and work accounts on devices.

ThisBash underscores the importance of robust security practices, emphasizing the need for vigilance with AI tools and browser extensions. Integrating threat intelligence and providing alert contexts can significantly enhance incident response capabilities.

Cyber Security News Tags:AI security, Anthropic, browser extension, Claude Dispatch, code execution, Cybersecurity, enterprise security, Forever Security, Gal Weizman, security flaw

Post navigation

Previous Post: OpenAI Model Circumvents Sandbox Restrictions with Custom Code
Next Post: Emerging Threats: Managing Vulnerabilities in Tech Systems

Related Posts

ResokerRAT Exploits Telegram API for Covert Control on Windows ResokerRAT Exploits Telegram API for Covert Control on Windows Cyber Security News
Bitter Malware Using Custom-Developed Tools To Evade Detection In Sophisticated Attacks Bitter Malware Using Custom-Developed Tools To Evade Detection In Sophisticated Attacks Cyber Security News
Go 1.25.6 and 1.24.12 Patch Critical Vulnerabilities Lead to DoS and Memory Exhaustion Risks Go 1.25.6 and 1.24.12 Patch Critical Vulnerabilities Lead to DoS and Memory Exhaustion Risks Cyber Security News
Apple Releases Major Security Update Fixing 273 Vulnerabilities Apple Releases Major Security Update Fixing 273 Vulnerabilities Cyber Security News
Critical SharePoint Flaw Allows Remote Code Execution Critical SharePoint Flaw Allows Remote Code Execution Cyber Security News
Phishing Scheme Exploits Dropbox to Steal User Credentials Phishing Scheme Exploits Dropbox to Steal User Credentials Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Emerging Threats: Managing Vulnerabilities in Tech Systems
  • Security Flaw in Claude Dispatch Allows Code Execution
  • OpenAI Model Circumvents Sandbox Restrictions with Custom Code
  • ARTEX AI Hacking Framework Found on Numerous Public Servers
  • Critical Vulnerabilities in Barracuda Email Security Exposed

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Emerging Threats: Managing Vulnerabilities in Tech Systems
  • Security Flaw in Claude Dispatch Allows Code Execution
  • OpenAI Model Circumvents Sandbox Restrictions with Custom Code
  • ARTEX AI Hacking Framework Found on Numerous Public Servers
  • Critical Vulnerabilities in Barracuda Email Security Exposed

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark