Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Web3Auth Flaw Exploited, Keplr Wallets Compromised

Web3Auth Flaw Exploited, Keplr Wallets Compromised

Posted on November 9, 2026 By CWS

An exploit in Web3Auth’s security has led to a significant breach of Keplr cryptocurrency wallets, affecting users who registered with Google or Apple accounts. The breach was announced by both companies late last week, highlighting a critical vulnerability that allowed an attacker to access these digital wallets.

Web3Auth’s Response to the Breach

Web3Auth, upon discovering the security flaw, proactively moved funds from vulnerable wallets to secure recovery wallets, with the assistance of the wallet maker. This preemptive measure was aimed at protecting user assets from being stolen by the attacker. Users who find their wallets empty may have had their funds temporarily secured rather than stolen.

Wallets established through more secure methods, such as using a recovery phrase or hardware wallet, were reportedly unaffected by this incident. Consequently, Web3Auth has suspended Google and Apple sign-in options as they continue to investigate the breach.

Guidance for Affected Users

For users who established their Keplr accounts using Google or Apple logins, specific instructions have been issued. Users are advised not to send new funds to compromised accounts or attempt to recreate them. Instead, funds should be transferred to wallets utilizing recovery phrases or hardware solutions. Official updates should only be trusted from the wallet maker’s official channels.

Assets that are staked or locked are proving more challenging to secure, and the wallet maker is collaborating with Web3Auth to provide users with tools to verify if their accounts were compromised. A published recovery address list aims to help users differentiate between legitimate and malicious transfers.

Extent and Impact of the Breach

The security flaw, described as a private key breach, allowed unauthorized access to some users’ wallets. Although specific details about the flaw and its exploitation timeline remain undisclosed, approximately 20% of accounts using Google and Apple logins were impacted. However, only a subset of those accounts appeared to have been exploited.

According to GoPlus, a Web3 security firm, the financial impact is estimated at around $1 million. Meanwhile, Bitquery, a blockchain data firm, reported that about $6.01 million was transferred to recovery wallets, initially identified as theft but later clarified as a precautionary rescue.

Wider Implications and Future Outlook

Web3Auth’s issue has implications beyond Keplr, affecting other companies using its services, though Keplr is the only named entity. The service has paused its wallet creation feature, leaving its login capabilities offline.

Consensys, which acquired Web3Auth in June 2025, has been working to integrate social login capabilities into its MetaMask wallet. Despite the breach, no MetaMask users have been reported affected. The incident underscores the ongoing challenge of securing digital wallets and the need for robust security measures as cryptocurrency adoption continues to grow.
The Hacker News Tags:Apple login, blockchain security, Consensys, crypto theft, crypto wallet recovery, Cryptocurrency, Google login, Keplr wallet, MetaMask, security breach, Web3Auth

Post navigation

Previous Post: Critical PowerSYSTEM Center Flaws Pose Security Risks
Next Post: Plex2Shell Vulnerability Threatens QNAP NAS Users

Related Posts

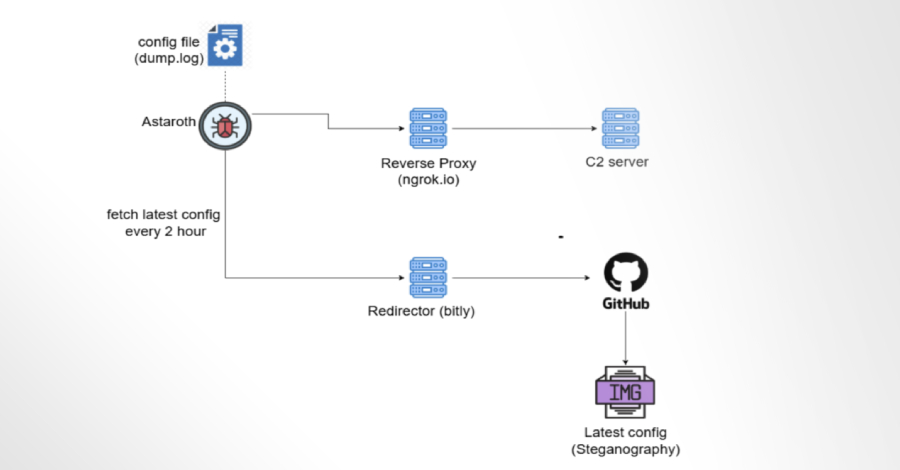
Astaroth Banking Trojan Abuses GitHub to Remain Operational After Takedowns Astaroth Banking Trojan Abuses GitHub to Remain Operational After Takedowns The Hacker News
Microsoft Launches Project Ire to Autonomously Classify Malware Using AI Tools Microsoft Launches Project Ire to Autonomously Classify Malware Using AI Tools The Hacker News
Gravity SMTP Plugin Vulnerability Exposes API Keys Gravity SMTP Plugin Vulnerability Exposes API Keys The Hacker News
FedRAMP at Startup Speed: Lessons Learned FedRAMP at Startup Speed: Lessons Learned The Hacker News
Veeam Fixes Critical Flaws in Backup Software Veeam Fixes Critical Flaws in Backup Software The Hacker News
ShadowSilk Hits 36 Government Targets in Central Asia and APAC Using Telegram Bots ShadowSilk Hits 36 Government Targets in Central Asia and APAC Using Telegram Bots The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Google Gemini Image Safety Bypass Exposed by Researchers
  • Hackers Target ‘SSHole’ Vulnerability in OpenSSH
  • Anubis Ransomware Uses New Lindnor Backdoor in U.S. Attack
  • Italy’s Foreign Minister Data Leak Blamed on Hackers
  • npm Packages Compromised by PolinRider Malware via Ethereum

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Google Gemini Image Safety Bypass Exposed by Researchers
  • Hackers Target ‘SSHole’ Vulnerability in OpenSSH
  • Anubis Ransomware Uses New Lindnor Backdoor in U.S. Attack
  • Italy’s Foreign Minister Data Leak Blamed on Hackers
  • npm Packages Compromised by PolinRider Malware via Ethereum

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark