Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Hackers Allegedly Claim Breach Of HSBC USA Customers’ Records Including Financial Details

Hackers Allegedly Claim Breach Of HSBC USA Customers’ Records Including Financial Details

Posted on October 29, 2025October 29, 2025 By CWS

A menace actor has claimed duty for breaching HSBC USA, alleging possession of an enormous database containing delicate buyer private identifiable info (PII) and monetary particulars.

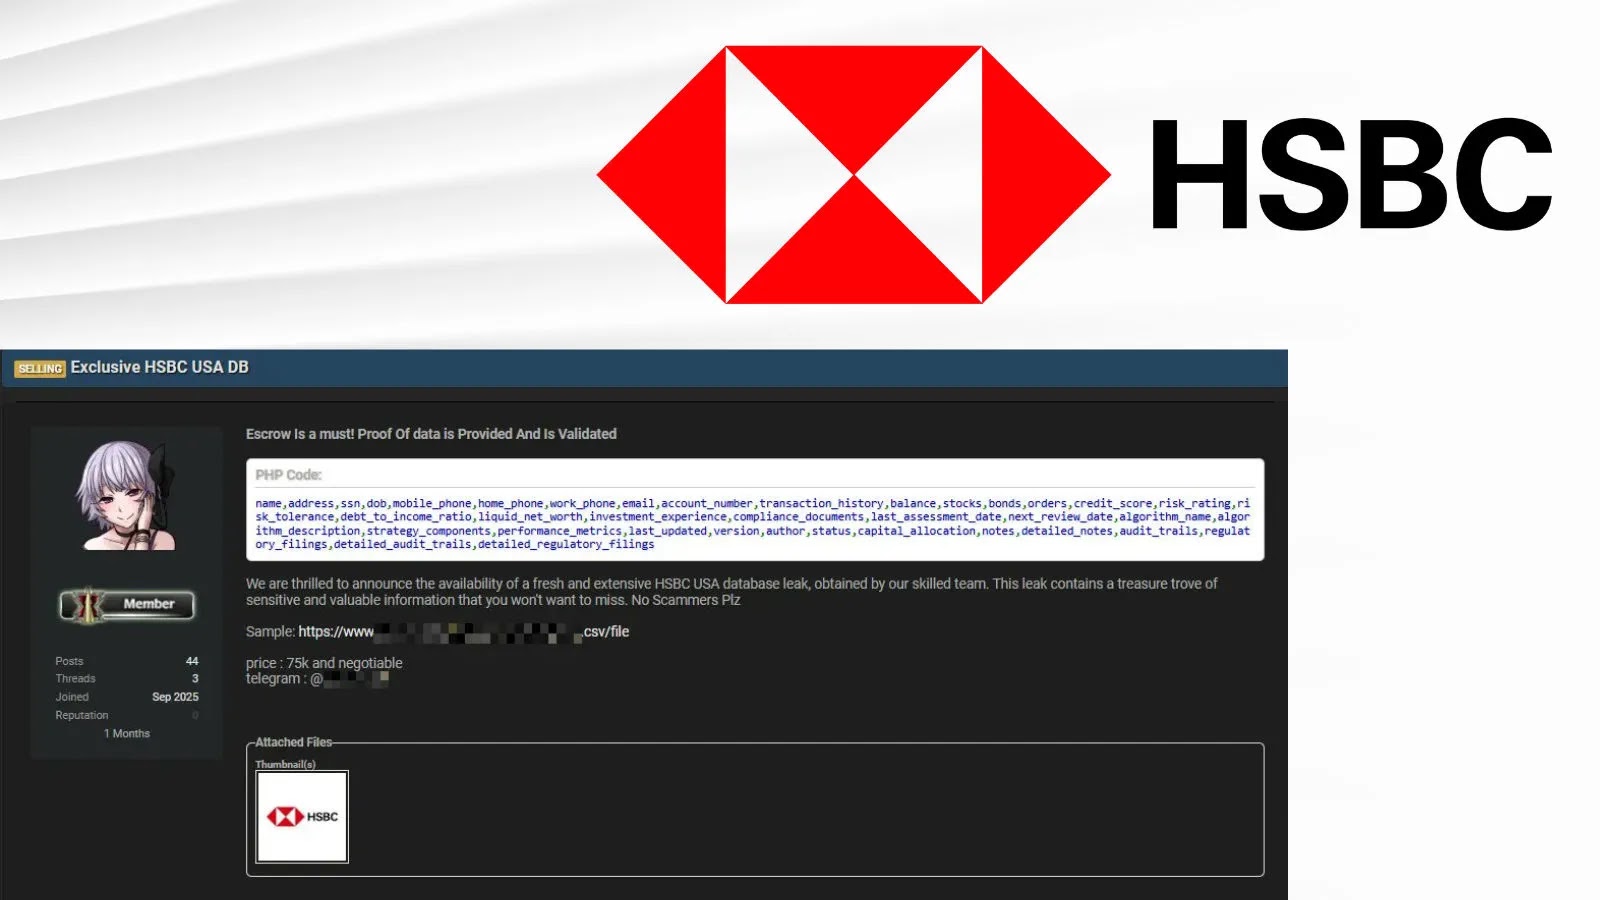
The hacker posted screenshots and information samples on a darkish net leak discussion board, asserting the breach concerned coordinated efforts to extract data from the financial institution’s programs.

This incident, reported on October 28, 2025, has raised alarms within the cybersecurity group amid HSBC’s ongoing challenges within the U.S. market.

The alleged stolen database incorporates full names, addresses, Social Safety numbers (SSNs), dates of start, telephone numbers, e-mail addresses, transaction histories, inventory orders, and checking account numbers.

HSBC USA Prospects Data

Researchers analyzed a supplied pattern and located indications of legitimacy, with the information showing current, doubtlessly from simply weeks prior, and probably focusing on company or institutional shoppers relatively than retail ones.

HSBC USA has largely exited the U.S. mass retail banking sector, which may clarify its concentrate on enterprise accounts.

The hooked up screenshot of the discussion board publish corroborates the declare, exhibiting an “Unique HSBC USA DB” with guarantees of validation and no free distribution.

HSBC’s Response and Implications

HSBC has acknowledged a current denial-of-service (DoS) assault however has firmly denied any buyer information compromise in its official statements.

The financial institution is investigating claims by way of third-party vendor entry factors and has strengthened defenses with enhanced authentication and monitoring.

No confirmed monetary losses have occurred, however consultants warn of dangers corresponding to identification theft, spear-phishing, and social engineering assaults exploiting the uncovered particulars.

Regulatory our bodies, together with the U.S. Division of the Treasury, are monitoring the state of affairs intently. This breach highlights vulnerabilities in monetary third-party ecosystems, doubtlessly damaging HSBC’s status and prompting consumer attrition.

Prospects are urged to observe accounts, allow two-factor authentication, and alter passwords instantly to mitigate potential fallout.

As investigations proceed, the complete scope stays unclear, however the occasion underscores the persistent threats going through world banks.

Observe us on Google Information, LinkedIn, and X for day by day cybersecurity updates. Contact us to characteristic your tales.
Cyber Security News Tags:Allegedly, Breach, Claim, Customers, Details, Financial, Hackers, HSBC, Including, Records, USA

Post navigation

Previous Post: Google Wear OS Message App Vulnerability Let Any Installed App To Send SMS Behalf Of User
Next Post: Chrome to Turn HTTPS on by Default for Public Sites

Related Posts

ChatGPT’s New Support for MCP Tools Let Attackers Exfiltrate All Private Details From Email ChatGPT’s New Support for MCP Tools Let Attackers Exfiltrate All Private Details From Email Cyber Security News
Fake Postmark MCP Server Silently Stole Thousands of Emails With a Single Line of Malicious Code Fake Postmark MCP Server Silently Stole Thousands of Emails With a Single Line of Malicious Code Cyber Security News
Microsoft’s ,000 Bounty for AI Vulnerabilities Microsoft’s $30,000 Bounty for AI Vulnerabilities Cyber Security News
MediaTek Chip Flaw Exposes Android PINs in Seconds MediaTek Chip Flaw Exposes Android PINs in Seconds Cyber Security News
Threat Modeling for DevSecOps Practical Guide Threat Modeling for DevSecOps Practical Guide Cyber Security News
Cisco Urges Immediate Update for Critical IOS XE Vulnerabilities Cisco Urges Immediate Update for Critical IOS XE Vulnerabilities Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • PHP2Shell Exploit Code Released, Botnet Threat Emerges
  • Stadia RAT: New Threat to Windows PC Security
  • Critical VeloCloud Vulnerability Exploited by Hackers
  • Node.js Exploit Exposes Remote Code Execution Risk
  • AI-Driven Ransomware Operations Unveiled by Researchers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • PHP2Shell Exploit Code Released, Botnet Threat Emerges
  • Stadia RAT: New Threat to Windows PC Security
  • Critical VeloCloud Vulnerability Exploited by Hackers
  • Node.js Exploit Exposes Remote Code Execution Risk
  • AI-Driven Ransomware Operations Unveiled by Researchers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark