Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Chinese Hackers Organization Influence U.S. Government Policy on International Issues

Chinese Hackers Organization Influence U.S. Government Policy on International Issues

Posted on November 7, 2025November 7, 2025 By CWS

China-linked risk actors have intensified their concentrate on influencing American governmental decision-making processes by focusing on organizations concerned in shaping worldwide coverage.

In April 2025, a classy intrusion right into a U.S. non-profit group revealed the persistent efforts of those attackers to determine long-term community entry and collect intelligence associated to coverage issues.

The risk actors demonstrated appreciable technical sophistication, using a number of evasion strategies and exploiting numerous vulnerabilities to take care of management over the compromised infrastructure for a number of weeks.

The assault marketing campaign displays a broader sample of Chinese language state-sponsored espionage focusing on policy-influencing establishments.

Preliminary reconnaissance started on April 5, 2025, when attackers performed mass vulnerability scans towards organizational servers, trying exploits together with CVE-2022-26134 (Atlassian OGNL Injection), CVE-2021-44228 (Log4j), CVE-2017-9805 (Apache Struts), and CVE-2017-17562 (GoAhead RCE).

These scanning actions established the inspiration for his or her subsequent exploitation makes an attempt and community compromise.

Symantec safety analysts recognized a number of tactical indicators linking this marketing campaign to established Chinese language risk teams together with Area Pirates, Kelp (Salt Storm), and Earth Longzhi, a acknowledged subgroup of the long-standing APT41 collective.

The forensic proof pointed on to China-based attribution by a number of distinctive assault methodologies.

DLL Sideloading as Main Persistence Mechanism

The attackers deployed DLL sideloading as their major persistence mechanism, leveraging a official VipreAV part named vetysafe.exe to execute malicious payload sbamres.dll.

This method exploits Home windows’ dynamic library search order by planting malicious code that official functions mechanically load and execute.

The attackers created a scheduled activity operating each 60 minutes with SYSTEM privileges, executing msbuild.exe to load an unknown XML configuration file containing injected code.

This code subsequently established communication with a command-and-control server at hxxp://38.180.83[.]166/6CDF0FC26CDF0FC2.

The delicate strategy allowed attackers to take care of persistent entry whereas evading conventional safety detection mechanisms, demonstrating evolving capabilities in focusing on U.S. coverage establishments.

Comply with us on Google Information, LinkedIn, and X to Get Extra Prompt Updates, Set CSN as a Most popular Supply in Google.
Cyber Security News Tags:Chinese, Government, Hackers, Influence, International, Issues, Organization, Policy, U.S

Post navigation

Previous Post: Researchers Evaded Elastic EDR’s Call Stack Signatures by Exploiting Call Gadgets
Next Post: Hidden Logic Bombs in Malware-Laced NuGet Packages Set to Detonate Years After Installation

Related Posts

Multi-Staged ValleyRAT Uses WeChat and DingTalk to Attack Windows Users Multi-Staged ValleyRAT Uses WeChat and DingTalk to Attack Windows Users Cyber Security News
New Spear-Phishing Attack Targeting Security Individuals in Israel Region New Spear-Phishing Attack Targeting Security Individuals in Israel Region Cyber Security News
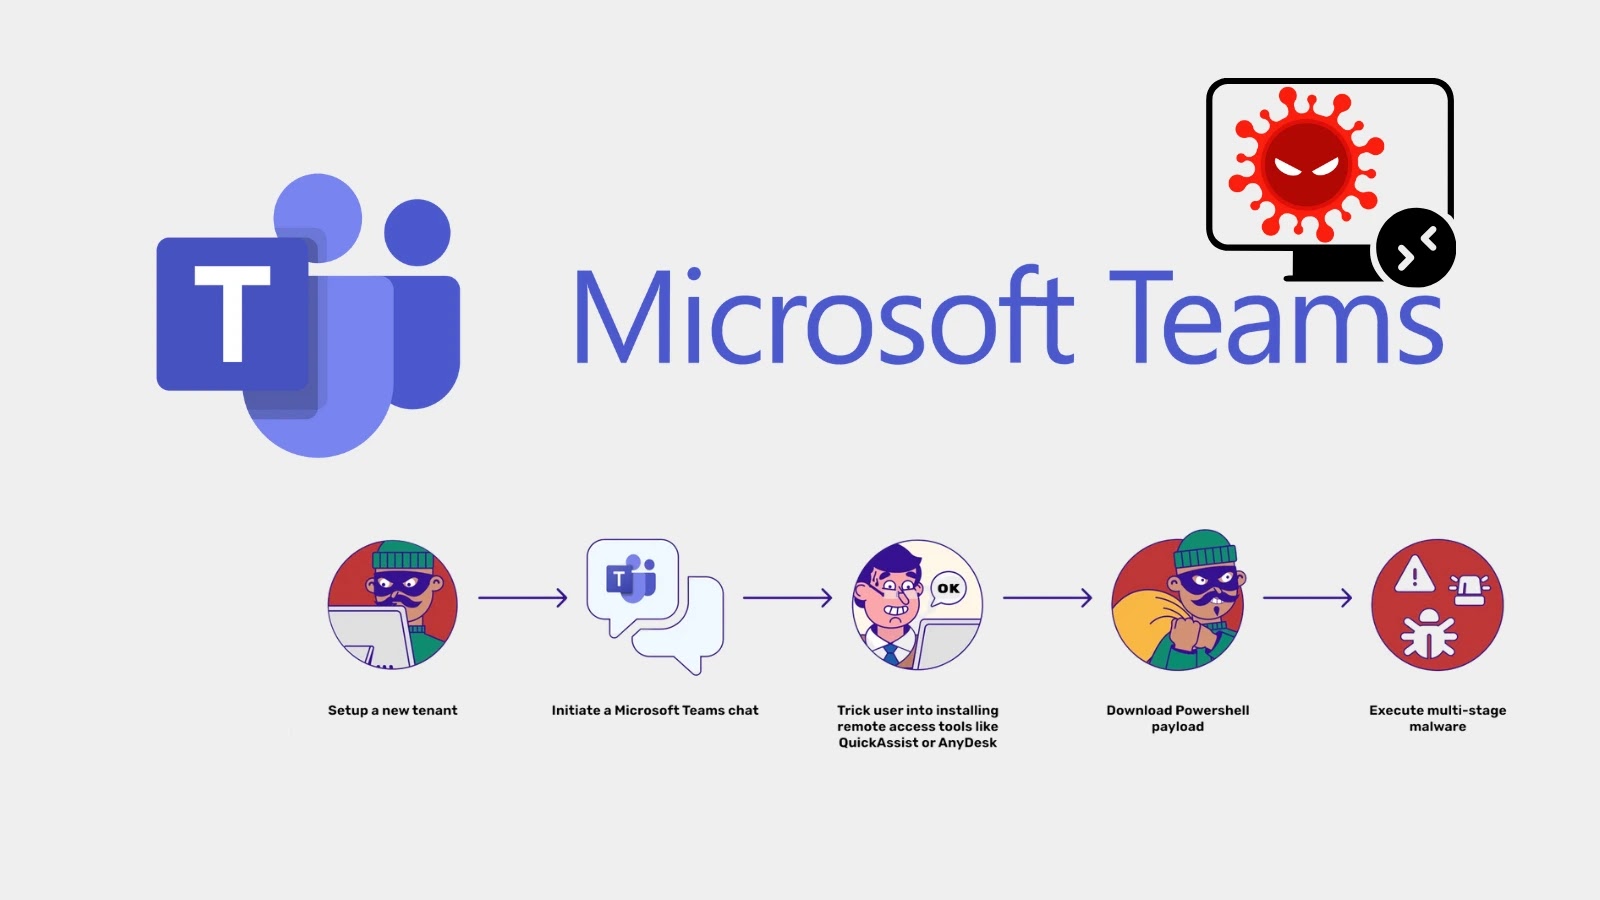
Hackers Abuse Microsoft Teams to Gain Remote Access With PowerShell-based Malware Hackers Abuse Microsoft Teams to Gain Remote Access With PowerShell-based Malware Cyber Security News
Hackers Offered K+ to Sever Ring from Amazon Cloud Hackers Offered $10K+ to Sever Ring from Amazon Cloud Cyber Security News
Metasploit Module Released For Actively Exploited SharePoint 0-Day Vulnerabilities Metasploit Module Released For Actively Exploited SharePoint 0-Day Vulnerabilities Cyber Security News
Plugin4Shell Exploit Threatens AI Coding Tools Plugin4Shell Exploit Threatens AI Coding Tools Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark