Regulation enforcement companies throughout a number of nations have efficiently dismantled a complicated cybercriminal operation that supplied malware testing providers designed to evade antivirus detection programs.
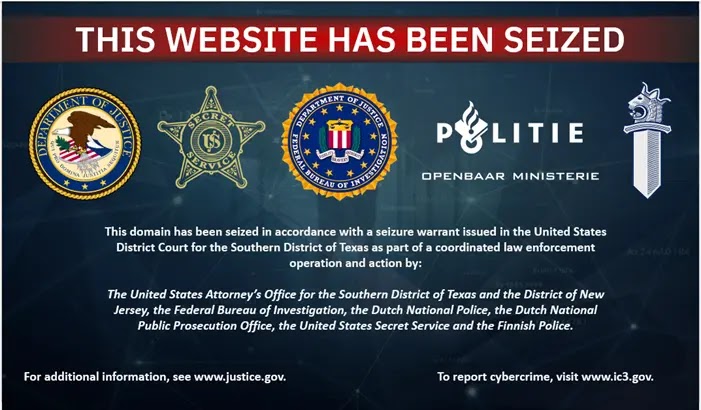
The coordinated worldwide effort resulted within the seizure of 4 domains and their related servers, dealing a major blow to cybercriminal infrastructure that enabled ransomware assaults and different malicious actions worldwide.
U.S. Legal professional Nicholas J. Ganjei introduced the profitable disruption of a web based software program crypting syndicate that specialised in serving to cybercriminals preserve their malicious software program undetected by safety programs.
The seized domains provided counter-antivirus (CAV) instruments and crypting providers that allowed criminals to obfuscate malware, making it nearly invisible to conventional antivirus applications and enabling unauthorized entry to pc programs.
Crypting represents a vital part within the cybercriminal ecosystem, because it includes utilizing specialised software program to switch malware in ways in which make it extraordinarily tough for antivirus applications to establish and neutralize threats.
Authorities Dismantled AVCheck
When mixed with CAV instruments, these providers present cybercriminals with a complete suite of evasion methods that considerably enhance the chance of profitable assaults.
Court docket paperwork reveal that authorities carried out undercover purchases from the seized web sites and completely analyzed the providers to verify their prison nature.
The investigation uncovered connections between these providers and identified ransomware teams which have focused victims throughout america and internationally, together with particular assaults within the Houston metropolitan space.
Investigators reviewed linked e mail addresses and different digital proof that established clear ties between the dismantled providers and energetic cybercriminal organizations.
“Trendy prison threats require trendy legislation enforcement options,” acknowledged Ganjei. “As cybercriminals have change into extra subtle of their schemes, they’ve likewise change into extra superior of their efforts to keep away from detection. Our legislation enforcement efforts should contain placing not simply on the particular person fraudster or hacker, however the enablers of those cybercriminals as nicely.”
FBI Houston Particular Agent in Cost Douglas Williams emphasised the worldwide impression of the operation: “Cybercriminals don’t simply create malware; they good it for max destruction. By leveraging counter antivirus providers, malicious actors refine their weapons towards the world’s hardest safety programs to raised slip previous firewalls, evade forensic evaluation, and wreak havoc throughout victims’ programs.”
The seizures occurred on Might 27 as a part of Operation Endgame, a multinational legislation enforcement initiative targeted on dismantling malware cybercriminal providers.
The operation concerned coordination between america, the Netherlands, France, Germany, and Denmark, with extra assist from Ukraine and Portugal.
The FBI Houston Discipline Workplace led the U.S. part of the investigation with vital help from legislation enforcement companions within the Netherlands and Finland, in addition to the U.S. Secret Service.
Stay Credential Theft Assault Unmask & Immediate Protection – Free Webinar