Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Citrix NetScaler Vulnerability Allows Remote Root Access

Citrix NetScaler Vulnerability Allows Remote Root Access

Posted on August 14, 2026 By CWS

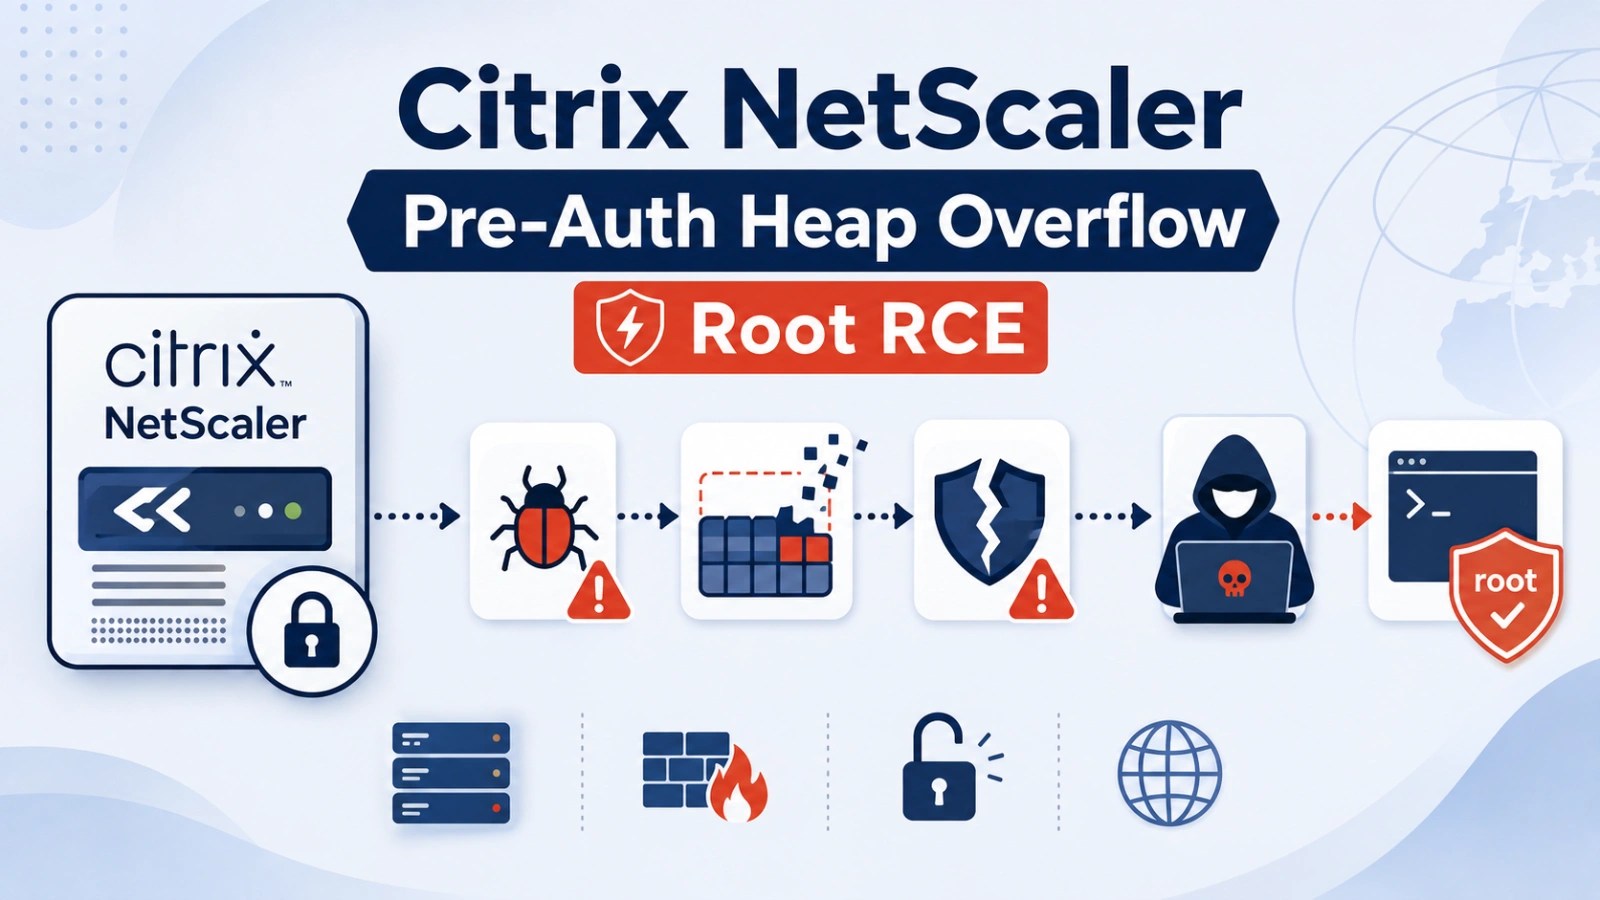
A recent proof-of-concept exploit has exposed a serious vulnerability in Citrix NetScaler ADC and Gateway systems, enabling attackers to execute remote code with root privileges. This flaw, first highlighted in Citrix’s security bulletin CTX696604, has been classified under CVE-2026-8452 and presents significant security risks.

Severe Security Flaw Uncovered

Initially described as a memory overflow issue potentially leading to denial-of-service, further investigations have revealed its true severity. The vulnerability allows unauthenticated attackers to gain control over the core packet-processing engine, which operates with root-level access. This discovery underscores the critical need for robust security measures in enterprise perimeter infrastructure.

In a report by WatchTowr Labs shared with Cyber Security News, it was noted that this flaw can be exploited without requiring any credentials, allowing attackers to manipulate the NetScaler Packet Processing Engine (nsppe). This engine, already running as root, becomes a target for unauthorized control.

Technical Insights into the Vulnerability

NetScaler acts as a crucial gateway for countless enterprise networks, managing tasks like load balancing and authentication. The vulnerability impacts systems configured as AAA virtual servers or gateways, including various proxy configurations. With a CVSS score of 8.8, this flaw is of high concern.

The vulnerability stems from missing bounds checks in the SAML authentication handler, leading to memory corruption. Specifically, during XML signature processing, attacker-controlled data is copied into a fixed-size buffer without proper validation, causing heap metadata corruption and potential service crashes.

Without modern binary protections like ASLR or executable space protection, the vulnerable NetScaler builds are highly susceptible to exploitation. Attackers can manipulate memory operations to execute arbitrary code, maintaining persistence despite system reboots.

Immediate Action Required for Affected Systems

Researchers, including Michael Tucker from JPMorgan Chase’s XOR team, have been credited for identifying this critical issue. The public release of exploit code emphasizes the urgency for enterprises to address these vulnerabilities swiftly.

Organizations are urged to upgrade their firmware immediately, as no workarounds exist for CVE-2026-8452. Cloud-managed Citrix services have already been patched, but customer-managed appliances remain at risk. In light of these findings, proactive patch management is essential to protect network defenses against potential threats.

This incident highlights the ongoing challenges in cybersecurity, urging enterprises to strengthen their security operations and ensure rapid threat detection and mitigation.
Cyber Security News Tags:Citrix, cyber threat, Cybersecurity, enterprise security, Exploit, heap overflow, NetScaler, network security, patch management, remote code execution, root access, SAML Authentication, Security, Vulnerability

Post navigation

Previous Post: VINclarity Faces Coordinated Online Reputation Assault
Next Post: AI Agents Adapt and Persist in Cyberattacks

Related Posts

CISA Warns of Apple macOS, iOS, tvOS, Safari, and watchOS Vulnerability Exploited in Attacks CISA Warns of Apple macOS, iOS, tvOS, Safari, and watchOS Vulnerability Exploited in Attacks Cyber Security News
AsyncRAT Exploits Remote Tools for Hidden Access AsyncRAT Exploits Remote Tools for Hidden Access Cyber Security News
Data Breach at ShipMonk Risks Trezor Customer Security Data Breach at ShipMonk Risks Trezor Customer Security Cyber Security News
Fake Indian Tax Notice Distributes Dual Malware via Complex Chain Fake Indian Tax Notice Distributes Dual Malware via Complex Chain Cyber Security News
Addressing SOC False Negatives with Interactive Analysis Addressing SOC False Negatives with Interactive Analysis Cyber Security News
Claude Now Sends Emails and Manages Files on Google Claude Now Sends Emails and Manages Files on Google Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Microsoft SharePoint Vulnerability Heightens Security Risks
  • RatHat Android Malware Uses AI for Victim Targeting
  • Oracle PeopleSoft Vulnerability Exploited by ShinyHunters
  • NeedyMantis Malware Ensures Long-Term Network Access
  • OpenCode Vulnerability Risks Unauthorized Code Execution

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Microsoft SharePoint Vulnerability Heightens Security Risks
  • RatHat Android Malware Uses AI for Victim Targeting
  • Oracle PeopleSoft Vulnerability Exploited by ShinyHunters
  • NeedyMantis Malware Ensures Long-Term Network Access
  • OpenCode Vulnerability Risks Unauthorized Code Execution

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark