Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Oracle PeopleSoft Vulnerability Exploited by ShinyHunters

Oracle PeopleSoft Vulnerability Exploited by ShinyHunters

Posted on September 28, 2026 By CWS

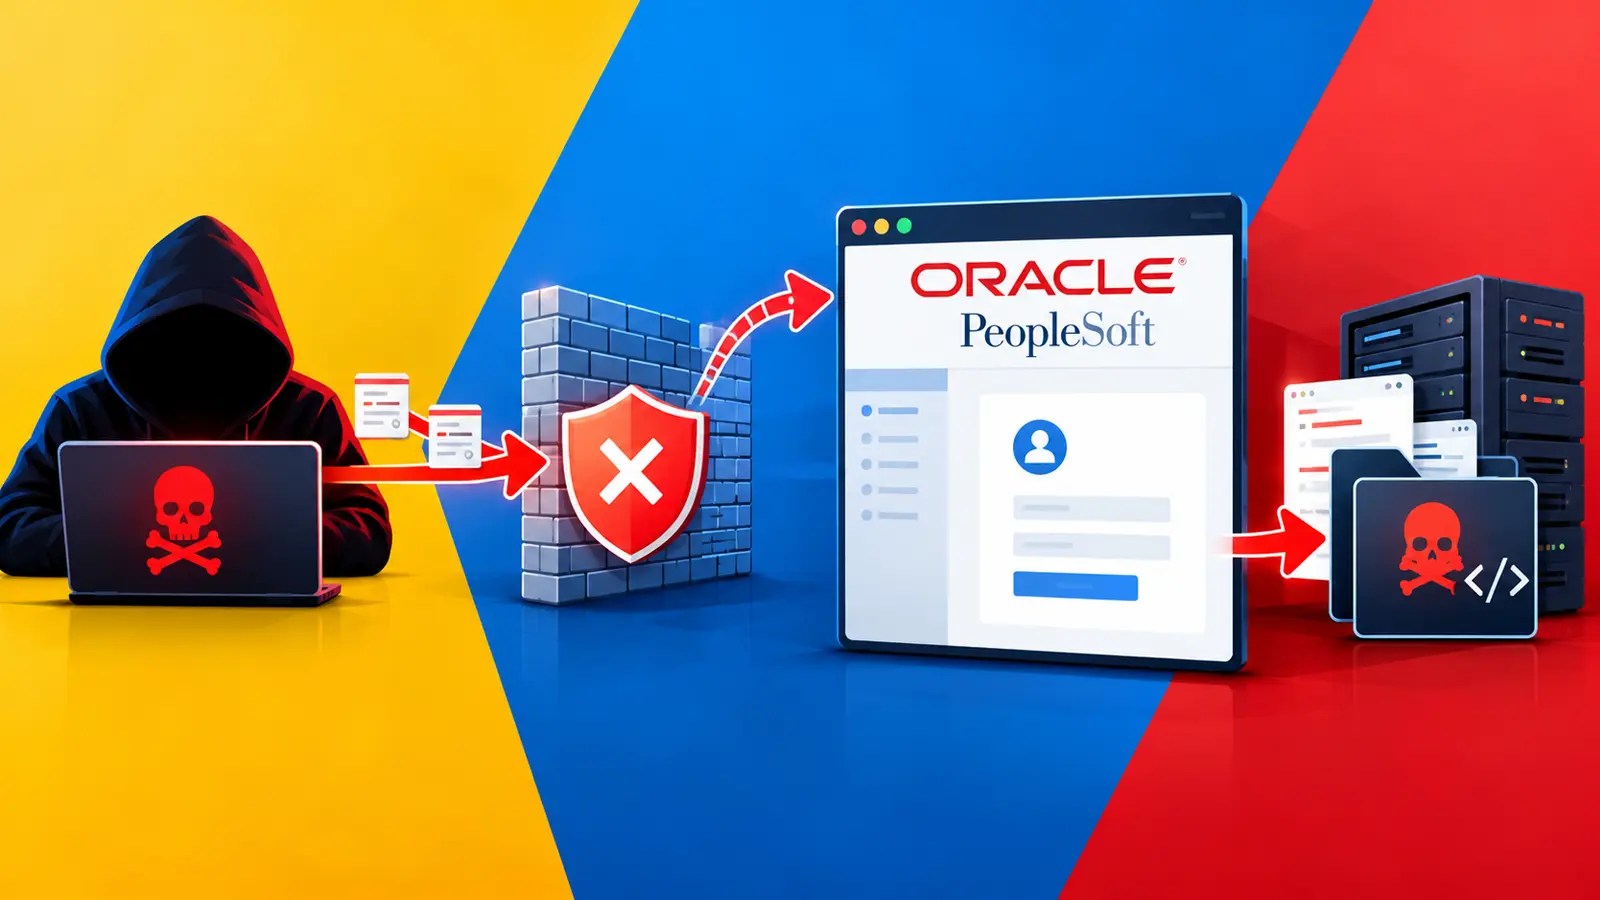
Cybersecurity group ShinyHunters has reignited attacks on Oracle PeopleSoft platforms, cleverly evading web application firewall (WAF) defenses to deploy web shells. This maneuver exposes a vulnerability in CVE-2026-35273, a critical flaw that had been previously exploited, posing significant risks to multiple sectors.

Escalating Attacks on Multiple Industries

Initially targeting universities, the attackers have now broadened their scope to include sectors such as technology, healthcare, agriculture, and government. This expansion highlights the critical nature of the PeopleSoft vulnerability, as it endangers systems containing sensitive HR, payroll, and operational data.

Google Cloud’s security analysts have linked these renewed attacks to the group known as UNC6240, or ShinyHunters. According to a report shared with Cyber Security News, web shells were placed on numerous systems worldwide, indicating an extensive exploitation effort.

Technical Exploitation Tactics

The attackers effectively bypassed existing WAF protections by altering the request path encoding. This discrepancy between the encoding and the application server’s processing allowed malicious requests to bypass security measures. Once a system’s vulnerability was confirmed, attackers could either install JSP-based web shells or execute commands directly in memory, thereby avoiding detection by file-based security tools.

ShinyHunters utilized POST requests with serialized Java objects to identify potential targets. Even unsuccessful attempts provided valuable reconnaissance data, underscoring the need for thorough log reviews and analysis, especially in environments using load balancing.

Mitigation and Future Outlook

To counteract these threats, organizations must promptly apply security patches for CVE-2026-35273 and maintain updated PeopleTools versions. Disabling or removing unnecessary applications, such as the Environment Management Hub, further reduces risk. The necessity for rapid patching in internet-facing deployments is emphasized by the Oracle emergency security update.

Security teams are advised to scrutinize access logs for encoded routes and suspect external POST activities, and to monitor PeopleSoft web directories for unauthorized files. Affected organizations must prepare for potential data-theft extortion and conduct detailed audits of database access for any suspicious bulk exports.

The persistence of these attacks highlights the importance of treating detected web shells as indicators of full system compromise. By maintaining vigilance and implementing robust security measures, organizations can better protect against ongoing cybersecurity threats.
Cyber Security News Tags:CVE-2026-35273, cyber attack, Cybersecurity, data breach, Google Cloud, Information Security, IT services, Oracle PeopleSoft, PeopleSoft flaw, security update, ShinyHunters, UNC6240, vulnerability patch, WAF bypass, web shells

Post navigation

Previous Post: NeedyMantis Malware Ensures Long-Term Network Access
Next Post: RatHat Android Malware Uses AI for Victim Targeting

Related Posts

Formbricks Signature Verification Vulnerability Let Attackers Reset User Passwords Without Authorization Formbricks Signature Verification Vulnerability Let Attackers Reset User Passwords Without Authorization Cyber Security News
175,000 Exposed Ollama Hosts Enable Code Execution and External System Access 175,000 Exposed Ollama Hosts Enable Code Execution and External System Access Cyber Security News
Microsoft 365 North America Disruption Due to CDN Issue Microsoft 365 North America Disruption Due to CDN Issue Cyber Security News
Ransomware Threats Exploit Employee Monitoring Tools Ransomware Threats Exploit Employee Monitoring Tools Cyber Security News
New EDR-Redir Tool Breaks EDR Exploiting Bind Filter and Cloud Filter Driver New EDR-Redir Tool Breaks EDR Exploiting Bind Filter and Cloud Filter Driver Cyber Security News
Malicious Joyfill npm Packages Compromise Developer Security Malicious Joyfill npm Packages Compromise Developer Security Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Microsoft 365 Services Disrupted by Global Outage
  • FBI Seizes $1.2 Billion in Cryptocurrency from Binance Heist
  • Lenovo Highlights Critical Server Security Vulnerability
  • Critical PTC Software Vulnerability Allows Remote Code Execution
  • Russian Hacker Linked to Qilin Ransomware Operations

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Microsoft 365 Services Disrupted by Global Outage
  • FBI Seizes $1.2 Billion in Cryptocurrency from Binance Heist
  • Lenovo Highlights Critical Server Security Vulnerability
  • Critical PTC Software Vulnerability Allows Remote Code Execution
  • Russian Hacker Linked to Qilin Ransomware Operations

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark