Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical Flaws in Claude Code Enable RCE and API Key Theft

Critical Flaws in Claude Code Enable RCE and API Key Theft

Posted on February 27, 2026 By CWS

Recent findings by Check Point Research (CPR) have uncovered critical vulnerabilities in Claude Code, an AI-driven development tool from Anthropic. These security flaws could potentially lead to Remote Code Execution (RCE) and unauthorized access to Anthropic’s API keys through manipulated project files.

Security Gaps in AI Development Tools

Anthropic’s Claude Code has been updated to patch all identified vulnerabilities before public disclosure, as reported by CPR. The incident underscores the increasing risks associated with AI-enabled development solutions, particularly how configuration files in repositories can be exploited to breach developer systems and collective workspaces.

Claude Code facilitates task delegation from the command line and supports collaboration through project settings saved in a .claude/settings.json file within repositories. Any changes to this file are inherited upon repository cloning, allowing contributors with commit access to potentially modify it to execute unintended actions on other developers’ machines.

Exploiting Untrusted Project Hooks

One of the vulnerabilities involved Claude Code’s “Hooks” feature, which permits automatic command execution at certain lifecycle stages. These hooks, defined within the repository-controlled configuration file, were found to execute immediately upon initializing a cloned repository, as demonstrated by CPR.

This automatic execution, including opening applications like a calculator without warnings, allows malicious actors to run arbitrary shell commands. Despite a general trust dialog, users were not explicitly informed of background command executions, which could lead to establishing unauthorized connections.

API Key Exposure and Consent Bypass

Another significant issue was found in the Model Context Protocol (MCP) settings, where CPR identified methods to bypass user consent dialogs. Even after Anthropic’s implementation of warning dialogs, malicious commands could be executed by manipulating settings to auto-approve MCP servers, enabling RCE.

Additionally, CPR noted vulnerabilities in the handling of environment variables within the settings file. By directing the ANTHROPIC_BASE_URL to a rogue server, attackers could capture API keys transmitted in plaintext, potentially leading to billing abuse and unauthorized access to shared workspaces.

This series of vulnerabilities presents serious supply chain threats, as harmful configurations can be introduced through pull requests or compromised accounts. To mitigate these risks, Anthropic has enhanced its security measures, including stricter warning dialogs and ensuring user consent before executing network operations.

Developers are strongly advised to update to the latest version of Claude Code and consider project files with the same diligence as executable code. For ongoing cybersecurity news, follow us on various platforms and contact us to share your stories.
Cyber Security News Tags:AI tools, Anthropic, API key theft, Check Point Research, Claude Code, Cybersecurity, developer security, RCE, software vulnerabilities, supply chain risk

Post navigation

Previous Post: Google API Keys Risk Exposure to Private Data
Next Post: Gardyn Smart Gardens: Vulnerabilities and Security Patches

Related Posts

Critical AVEVA Software Vulnerabilities Enables Remote Code Execution Under System Privileges Critical AVEVA Software Vulnerabilities Enables Remote Code Execution Under System Privileges Cyber Security News
Microsoft Asks IT Admins to Contact for Fix Related to Windows IIS Failure Issues Microsoft Asks IT Admins to Contact for Fix Related to Windows IIS Failure Issues Cyber Security News
Google Patches Android 0-Day Vulnerabilities Exploited in the Wild Google Patches Android 0-Day Vulnerabilities Exploited in the Wild Cyber Security News
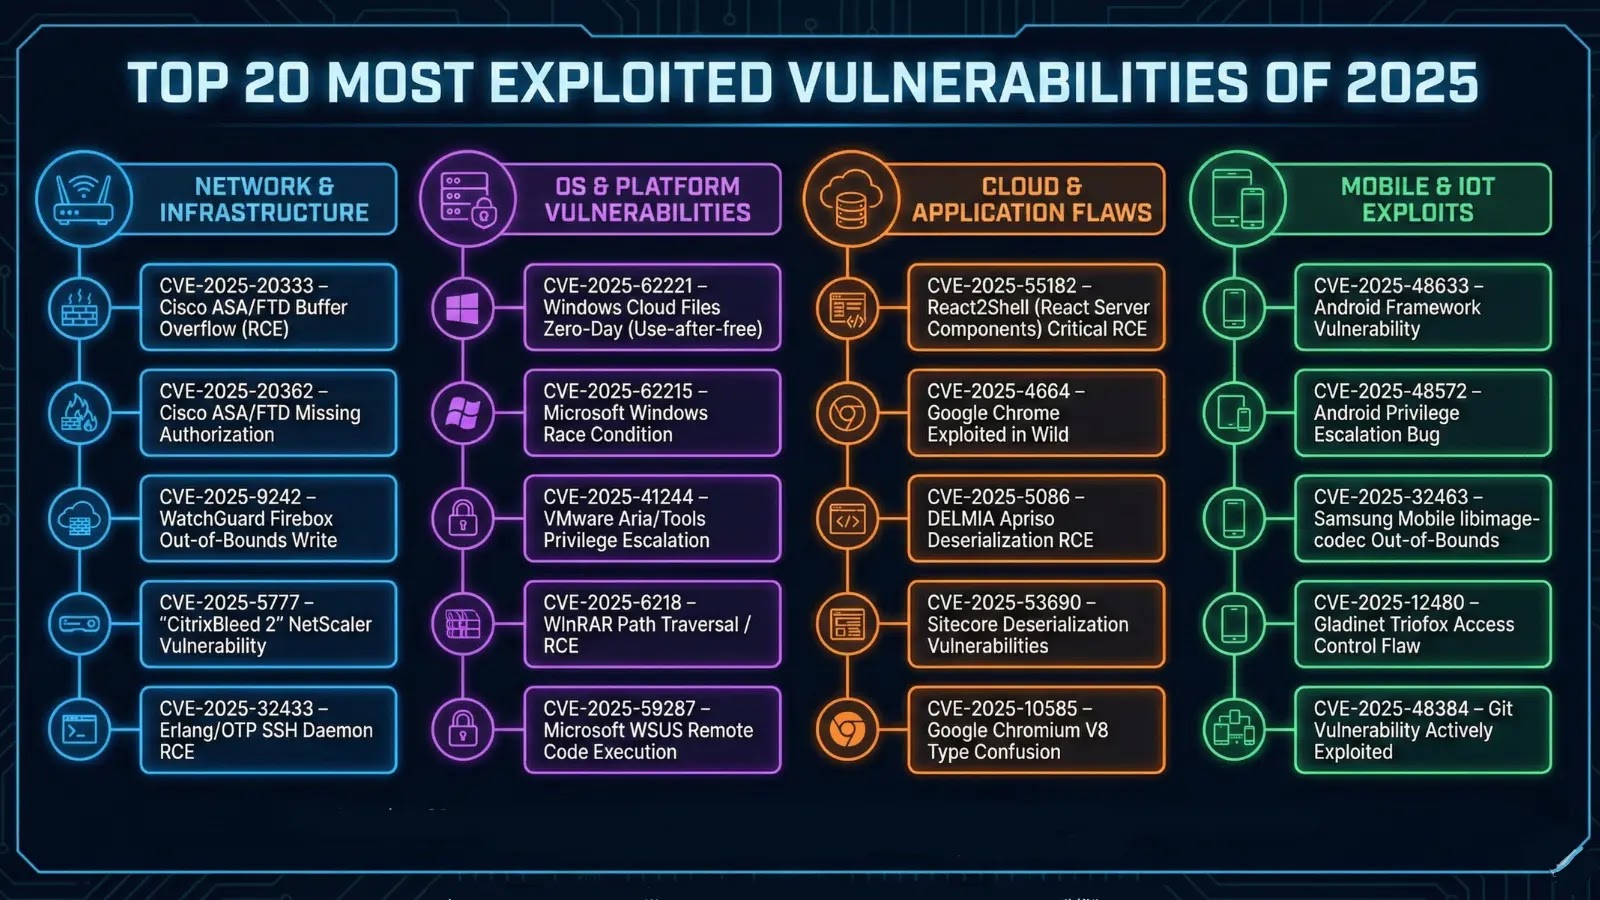
Top 20 Most Exploited Vulnerabilities of 2025 Top 20 Most Exploited Vulnerabilities of 2025 Cyber Security News
Lampion Banking Malware Employs ClickFix Lures To Steal Banking Information Lampion Banking Malware Employs ClickFix Lures To Steal Banking Information Cyber Security News
New Semantic Chaining Jailbreak Attack Bypasses Grok 4 and Gemini Nano Security Filters New Semantic Chaining Jailbreak Attack Bypasses Grok 4 and Gemini Nano Security Filters Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • OpenAI Employee Charged for Planting Hidden Recorder
  • Microsoft Disrupts Major Phishing Kits Behind Global Scams
  • Critical NGINX Vulnerabilities Risk Server Stability
  • Critical Flaw in Collabora CODE App Exploited by Hackers
  • Windows 11 Update Disrupts Remote Desktop Connectivity

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • OpenAI Employee Charged for Planting Hidden Recorder
  • Microsoft Disrupts Major Phishing Kits Behind Global Scams
  • Critical NGINX Vulnerabilities Risk Server Stability
  • Critical Flaw in Collabora CODE App Exploited by Hackers
  • Windows 11 Update Disrupts Remote Desktop Connectivity

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark