Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Hackers Target Critical Quest KACE SMA Vulnerability

Hackers Target Critical Quest KACE SMA Vulnerability

Posted on March 23, 2026 By CWS

Cybersecurity experts have raised alarms over a critical vulnerability in Quest KACE Systems Management Appliance (SMA) being actively exploited by hackers. This flaw, identified as CVE-2025-32975 with a CVSS score of 10.0, allows attackers to bypass authentication, posing a significant risk to unpatched systems.

Details of the Vulnerability

Arctic Wolf, a leading cybersecurity firm, detected suspicious activities in early March 2026, indicating that threat actors are leveraging this vulnerability. The exploit allows unauthorized users to impersonate legitimate ones, leading to full administrative control if the system remains unpatched. Quest addressed this issue in May 2025, but many systems appear to be still vulnerable.

The attackers have reportedly used the vulnerability to gain administrative privileges and execute remote commands. They have been observed deploying Base64-encoded payloads through external servers, indicating a well-coordinated attack strategy.

Method of Exploitation

Once in control, the attackers created additional administrative accounts using a process called “runkbot.exe,” associated with the SMA Agent. This allows them to manage installations and execute scripts, further deepening their access. Moreover, Windows Registry changes were made using PowerShell scripts, likely for persistence and configuration manipulation.

Additional malicious activities included harvesting credentials through tools like Mimikatz, and conducting reconnaissance by listing logged-in users and running specific network commands. The attackers also sought remote desktop protocol (RDP) access to key infrastructure components such as backup systems and domain controllers.

Preventive Measures

To mitigate this critical threat, cybersecurity experts strongly advise applying the latest patches provided by Quest. Administrators should ensure that SMA instances are not exposed to the internet. The issue is resolved in software versions 13.0.385, 13.1.81, 13.2.183, 14.0.341 (Patch 5), and 14.1.101 (Patch 4).

By implementing these measures, organizations can protect their systems from being compromised by these sophisticated attacks. Continuous monitoring and prompt application of security updates are crucial in maintaining robust cybersecurity defenses.

The Hacker News Tags:authentication bypass, CVE-2025-32975, Cybersecurity, endpoint security, patch update, Quest KACE, security flaw, system management, Threat Actors, Vulnerability

Post navigation

Previous Post: Microsoft Releases Urgent Windows 11 Update for Account Sign-In Bug
Next Post: New Stealth Malware Campaign Targets Key Sectors

Related Posts

WordPress Patch Fixes Critical Comment2Shell Vulnerability WordPress Patch Fixes Critical Comment2Shell Vulnerability The Hacker News
OceanLotus Targets Vietnamese Firms with SPECTRALVIPER OceanLotus Targets Vietnamese Firms with SPECTRALVIPER The Hacker News
ERMAC V3.0 Banking Trojan Source Code Leak Exposes Full Malware Infrastructure ERMAC V3.0 Banking Trojan Source Code Leak Exposes Full Malware Infrastructure The Hacker News
Salesforce Flags Unauthorized Data Access via Gainsight-Linked OAuth Activity Salesforce Flags Unauthorized Data Access via Gainsight-Linked OAuth Activity The Hacker News
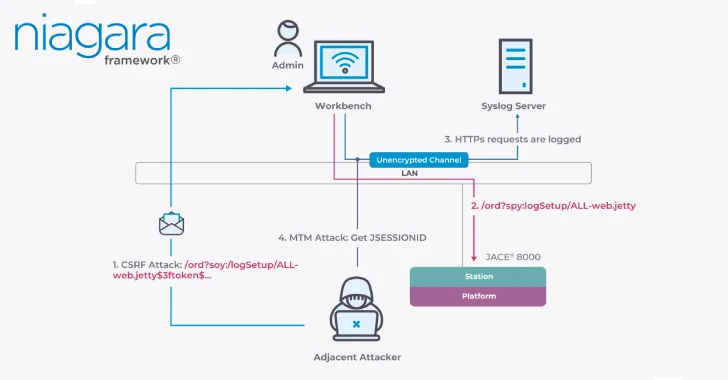
Critical Flaws in Niagara Framework Threaten Smart Buildings and Industrial Systems Worldwide Critical Flaws in Niagara Framework Threaten Smart Buildings and Industrial Systems Worldwide The Hacker News
Hugging Face Diffusers Security Flaws Threaten AI Systems Hugging Face Diffusers Security Flaws Threaten AI Systems The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark