
Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Exchange Exploits and npm Worms: This Week’s Cyber Threats

Exchange Exploits and npm Worms: This Week’s Cyber Threats

Posted on May 18, 2026 By CWS

This week in cybersecurity, significant vulnerabilities have surfaced, affecting multiple platforms and services. From Exchange Server exploits to npm worms, organizations must remain vigilant. The rise of AI in speeding up vulnerability discovery adds an urgent layer to this evolving threat landscape.

Exchange Server Vulnerability Exploited

Microsoft’s Exchange Server has become the focal point of a new security vulnerability, actively exploited in the wild. This issue, identified as CVE-2026-42897, stems from a cross-site scripting flaw, allowing for potential spoofing attacks. The vulnerability has a CVSS score of 8.1, indicating its critical nature. While Microsoft has released a temporary mitigation via its Exchange Emergency Mitigation Service, a permanent fix is still in development. The identity of the attackers and the scope of this exploitation remain unclear, highlighting the need for immediate patching and monitoring by affected entities.

Supply Chain Attacks and npm Worms

Supply chain attacks continue to escalate, with TeamPCP orchestrating a new wave of attacks through compromised npm packages. These attacks target open-source projects by inserting malicious code that harvests sensitive information like credentials and API keys. The rapid propagation of such threats underscores the importance of scrutinizing dependencies and maintaining robust security practices within developer ecosystems.

Advancements and Risks in AI Security

AI is playing a dual role in cybersecurity, aiding both defense and attack mechanisms. OpenAI’s initiative, Daybreak, aims to enhance software security by leveraging AI to detect and fix vulnerabilities. However, this technology can be a double-edged sword, potentially exploited by attackers to enhance the sophistication and speed of their operations. Organizations are advised to prepare for an increase in AI-driven vulnerability discoveries and to implement stringent security measures to mitigate these risks.

As the cybersecurity landscape becomes increasingly complex, the message is clear: proactive measures are essential. Regular patching, key management, and a thorough review of software and dependencies are crucial steps in safeguarding systems against these evolving threats. Staying informed and prepared is the best defense against a rapidly changing threat environment.

The Hacker News Tags:AI vulnerabilities, Cisco exploit, Cybersecurity, Exchange Server, npm worm, Ransomware, RCS messaging, Software Security, supply chain attacks

Post navigation

Previous Post: Healthcare Data Breaches Affect Millions Across the U.S.
Next Post: Critical n8n Security Flaws Risk Remote Code Execution

Related Posts

OpenAI Addresses Malicious Axios Incident in macOS Apps OpenAI Addresses Malicious Axios Incident in macOS Apps The Hacker News
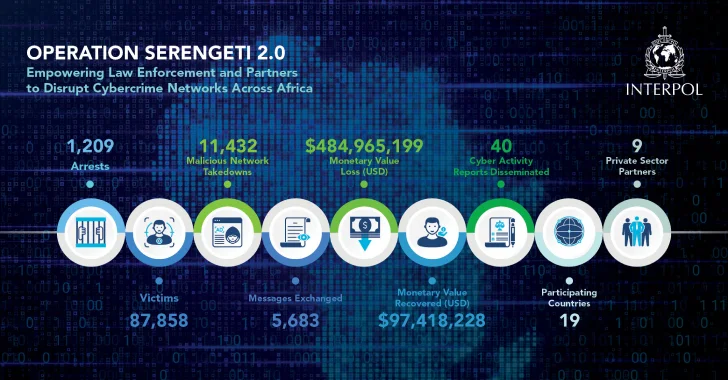
INTERPOL Arrests 1,209 Cybercriminals Across 18 African Nations in Global Crackdown INTERPOL Arrests 1,209 Cybercriminals Across 18 African Nations in Global Crackdown The Hacker News
Critical cPanel Vulnerability Exploited by Cybercriminals Critical cPanel Vulnerability Exploited by Cybercriminals The Hacker News
OpenAI Enhances Cybersecurity with GPT-5.5-Cyber OpenAI Enhances Cybersecurity with GPT-5.5-Cyber The Hacker News
NGate Malware Exploits HandyPay App in Brazil for NFC Data Theft NGate Malware Exploits HandyPay App in Brazil for NFC Data Theft The Hacker News
Geopolitical Tensions Fuel Cyber Conflict Geopolitical Tensions Fuel Cyber Conflict The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Red Hat Satellite Flaw: Risk of Root Password Theft
  • Hackers Exploit Software Updates for Credential Theft
  • Major Cybersecurity Breaches and AI Threats Uncovered
  • Hackers Exploit Microsoft SQL Server for Data Exfiltration
  • iCloud Email Flaws Allowed Spoofing of Any Address

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Red Hat Satellite Flaw: Risk of Root Password Theft
  • Hackers Exploit Software Updates for Credential Theft
  • Major Cybersecurity Breaches and AI Threats Uncovered
  • Hackers Exploit Microsoft SQL Server for Data Exfiltration
  • iCloud Email Flaws Allowed Spoofing of Any Address

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark