Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical Vulnerabilities in Angular Extension Pose RCE Risk

Critical Vulnerabilities in Angular Extension Pose RCE Risk

Posted on May 26, 2026 By CWS

A series of significant security flaws have been discovered in the Angular Language Service extension for Visual Studio Code, known as Angular.ng-template. These vulnerabilities could allow attackers to execute remote code on developers’ systems through several exploitation techniques.

Understanding the Vulnerabilities

The identified vulnerabilities stem from the unsafe handling of user input and insecure configuration management within the extension. Security researchers have highlighted that attackers can leverage trusted development activities, such as project opening or source code review, to run arbitrary commands on a developer’s computer.

Key Exploitation Pathways

One major exploitation method involves injecting commands via JSDoc comments. The extension’s Markdown rendering engine is configured with “isTrusted: true,” which permits the execution of embedded command URIs. Unfortunately, the Angular language server does not adequately sanitize JSDoc comments before they are processed by the renderer. This oversight allows attackers to embed malicious command links within TypeScript or JavaScript files. If a developer hovers over the affected symbol and clicks the link, the command is executed on the system.

Another critical issue lies in the insecure management of the TypeScript SDK (tsdk) configuration. The extension reads tsdk settings directly from the workspace’s .vscode/settings.json file without verifying the workspace’s trustworthiness. This configuration is then used by the language server, which loads the tsserverlibrary.js file using Node.js require(). An attacker can exploit this by placing a harmful tsserverlibrary.js file in a project directory and referencing it in the workspace configuration. When the project is opened, the extension executes the malicious code without user interaction.

Mitigation and Recommendations

These vulnerabilities circumvent VS Code’s Workspace Trust model, designed to prevent untrusted code execution. The tsdk-based attack occurs automatically upon project opening, while the JSDoc-based attack requires minimal user interaction, making both methods viable for real-world attacks.

Successful exploitation can lead to complete system takeover, unauthorized command execution, data access, and persistence. Developers could unknowingly trigger these exploits by opening seemingly legitimate repositories in VS Code, allowing attackers immediate control through malicious configuration files.

The issues, detailed in GitHub advisory GHSA-ccq4-xmxr-8hcq, affect versions before 21.2.4 and have been resolved in the latest update. Classified as high severity under CVSS v4, these flaws have low attack complexity and require no special privileges. They involve multiple weaknesses, such as cross-site scripting and code injection. Developers are urged to upgrade to version 21.2.4 or later promptly.

Moreover, developers should avoid opening untrusted repositories, thoroughly review workspace configurations, and adopt secure development practices when handling third-party code.
Cyber Security News Tags:Angular, code injection, CVSS, Github Advisory, JSDoc, RCE, Security, TypeScript, Visual Studio Code, Vulnerabilities

Post navigation

Previous Post: Lithuania Probes International Link in Major Data Breach
Next Post: Enhancing Alert Triage Efficiency for Tier 1 Teams

Related Posts

Microsoft Bookings Vulnerability Let Attackers Alter the Meeting Details Microsoft Bookings Vulnerability Let Attackers Alter the Meeting Details Cyber Security News
AI-Driven Penetration Testing Tool Enhances Linux Security AI-Driven Penetration Testing Tool Enhances Linux Security Cyber Security News
Red Hat Data Breach – Threat Actors Claim Breach of 28K Private GitHub Repositories Red Hat Data Breach – Threat Actors Claim Breach of 28K Private GitHub Repositories Cyber Security News
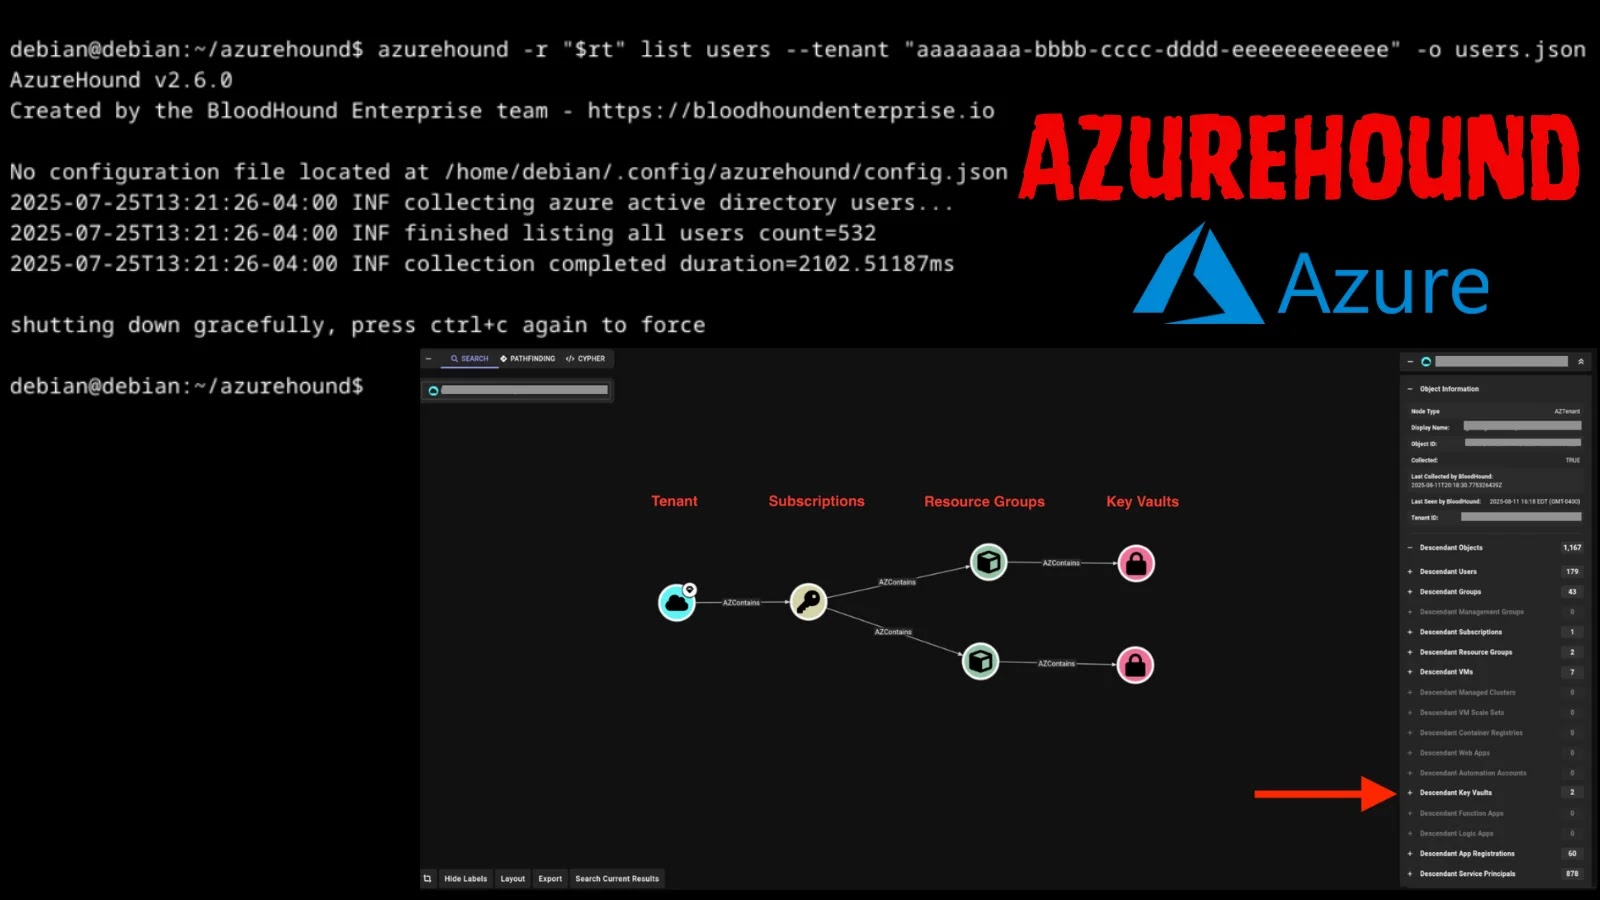
AzureHound Penetration Testing Tool Exploited by Threat Actors to Enumerate Azure and Entra ID AzureHound Penetration Testing Tool Exploited by Threat Actors to Enumerate Azure and Entra ID Cyber Security News
BlackLock Ransomware Attacking Windows, Linux, and VMware ESXi Environments BlackLock Ransomware Attacking Windows, Linux, and VMware ESXi Environments Cyber Security News
Checkmarx Data Leak on Dark Web After Security Breach Checkmarx Data Leak on Dark Web After Security Breach Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Critical NGINX Vulnerabilities Risk Server Stability
  • Critical Flaw in Collabora CODE App Exploited by Hackers
  • Windows 11 Update Disrupts Remote Desktop Connectivity
  • Cisco Alerts on Exploited Vulnerability in Email Gateway
  • Optimize MSSP Efficiency by Reducing Tier 1 Bottlenecks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Critical NGINX Vulnerabilities Risk Server Stability
  • Critical Flaw in Collabora CODE App Exploited by Hackers
  • Windows 11 Update Disrupts Remote Desktop Connectivity
  • Cisco Alerts on Exploited Vulnerability in Email Gateway
  • Optimize MSSP Efficiency by Reducing Tier 1 Bottlenecks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark