Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
NodeBB Vulnerabilities Expose Private Chats and Forums

NodeBB Vulnerabilities Expose Private Chats and Forums

Posted on July 27, 2026 By CWS

NodeBB’s Security Risks Exposed

Recent cybersecurity research has unveiled eight critical vulnerabilities in NodeBB, a widely used forum platform built on Node.js. These vulnerabilities expose millions of users to potential risks such as unauthorized access to private messages and complete forum takeovers.

All versions of NodeBB prior to 4.14.0 are affected by these issues, which were identified during an AI-assisted penetration test by security firm Aikido. This discovery showcases how AI-driven security testing can swiftly uncover complex vulnerabilities that might be overlooked by manual analysis.

Core Vulnerabilities in NodeBB

The investigation highlighted three significant cross-site scripting (XSS) vulnerabilities. A primary issue involves improper data sanitization within federated profiles, where attackers can manipulate profile image URLs to execute malicious JavaScript.

Additionally, vulnerabilities within the admin panel’s error logs allow attackers to insert malicious HTML through specially crafted ActivityPub messages. This loophole enables attackers to execute scripts and potentially gain full administrative control over the forum.

Another identified flaw permits attackers to manipulate template and translation processing, allowing unauthorized JavaScript execution via crafted links.

Additional Security Concerns

Beyond XSS issues, the research uncovered several authorization bypass vulnerabilities. A notable flaw enables attackers to impersonate any user by exploiting weaknesses in ActivityPub signature validation, giving them access to private messages.

Unauthorized admin page access and a mass assignment flaw further compound the risks, allowing attackers to access sensitive data and overwrite existing forum posts without proper authorization checks.

Furthermore, a logic flaw in the upvote system allows attackers to artificially boost post visibility by submitting unauthorized “Like” activities.

Patch and Recommendations

All vulnerabilities have been addressed and patched as of early July 2026 in NodeBB version 4.14.0. The update includes enhanced input sanitization, stricter authorization protocols, and improved translation handling mechanisms.

Security specialists urge forum administrators to upgrade immediately to the latest version to mitigate these risks. Tools like Aikido can assist in identifying vulnerable instances quickly, providing an additional layer of protection.

These findings emphasize the broader security challenges associated with federated protocols like ActivityPub, where inconsistent security measures can lead to vulnerabilities. They also highlight the increasing importance of AI in cybersecurity, offering a more comprehensive approach to threat detection.
Cyber Security News Tags:ActivityPub, AI pentesting, AI security, authorization bypass, cyber threats, Cybersecurity, forum security, NodeBB, private messages, security update, software patch, Vulnerabilities, XSS

Post navigation

Previous Post: MCBS Cyberattack Exposes Data of Over 1.2 Million
Next Post: Critical ChatGPT AgentForger Exploit Fixed by OpenAI

Related Posts

Critical FFmpeg Vulnerabilities Demand Urgent Updates Critical FFmpeg Vulnerabilities Demand Urgent Updates Cyber Security News
Massive Android Ad Fraud Uncovered with 455 Apps Massive Android Ad Fraud Uncovered with 455 Apps Cyber Security News
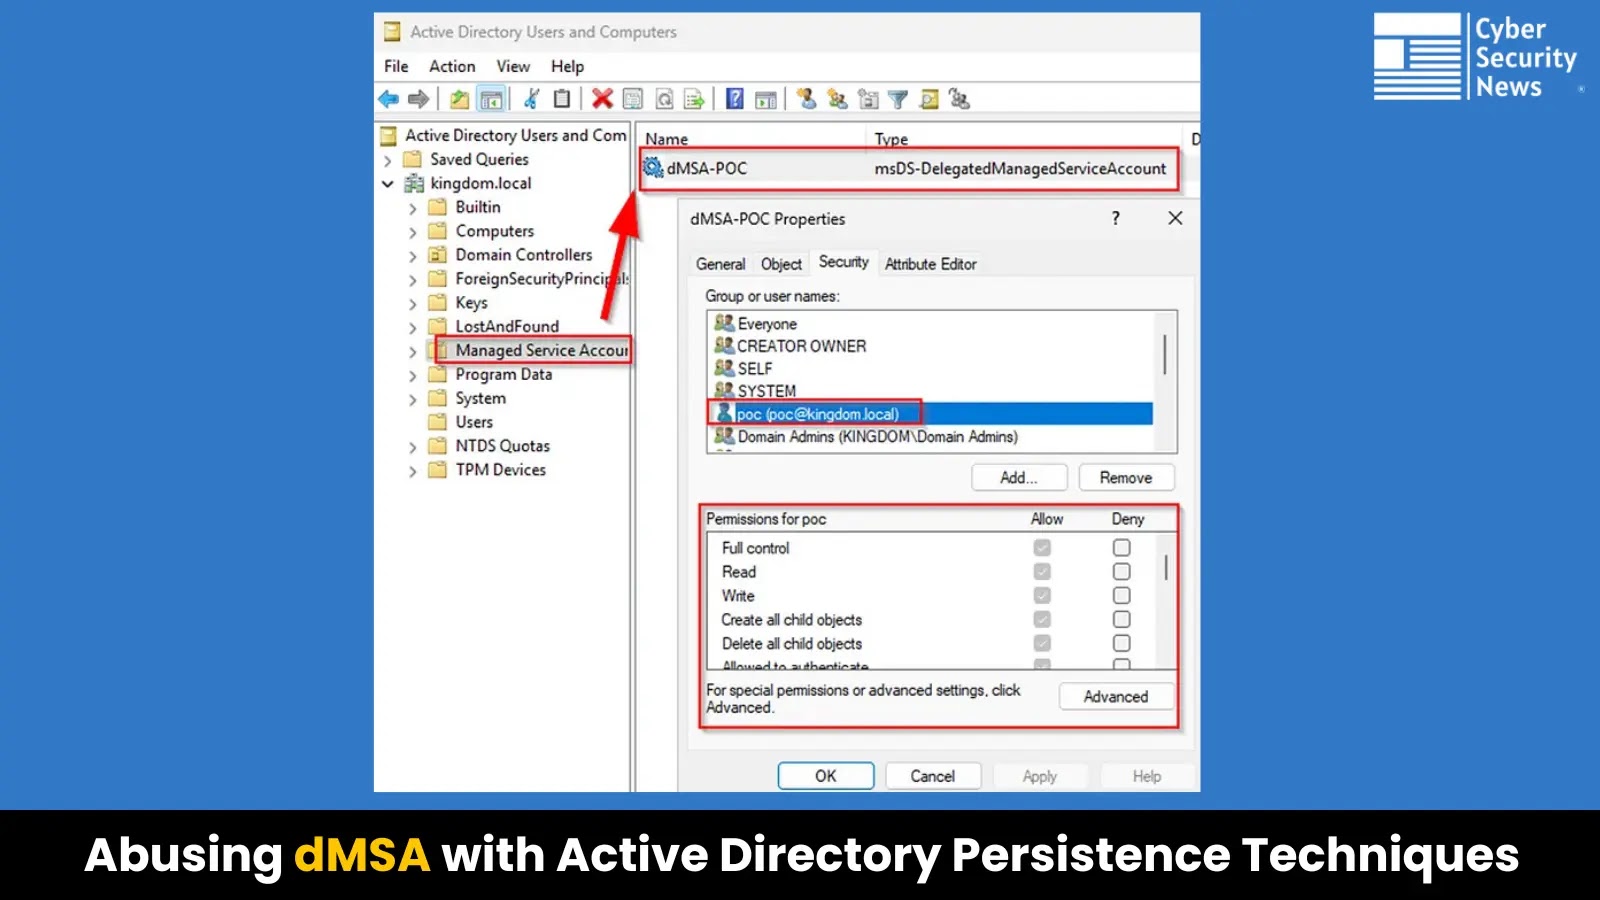
Abusing dMSA with Advanced Active Directory Persistence Techniques  Abusing dMSA with Advanced Active Directory Persistence Techniques  Cyber Security News
Ivanti Patches 13 Vulnerabilities in Endpoint Manager Allowing Remote Code Execution Ivanti Patches 13 Vulnerabilities in Endpoint Manager Allowing Remote Code Execution Cyber Security News
Chrome 153 Updates Address 230 Security Flaws, Including Critical 0-Day Chrome 153 Updates Address 230 Security Flaws, Including Critical 0-Day Cyber Security News
X/Twitter The Most Aggressive Social Media App Collecting Users Location Information X/Twitter The Most Aggressive Social Media App Collecting Users Location Information Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Cloudflare Updates WAF Rules Amid Brotli Vulnerability
  • PHP Updates Windows Builds to Address Critical HTTP2Shell Flaw
  • Emperador Ransomware Claims Data Breach at AB InBev
  • PHP2Shell Exploit Targets University and Business Websites
  • OpenBSD 8.0 Enhances Security and Post-Quantum SSH

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Cloudflare Updates WAF Rules Amid Brotli Vulnerability
  • PHP Updates Windows Builds to Address Critical HTTP2Shell Flaw
  • Emperador Ransomware Claims Data Breach at AB InBev
  • PHP2Shell Exploit Targets University and Business Websites
  • OpenBSD 8.0 Enhances Security and Post-Quantum SSH

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark