Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical TP-Link Router Flaw Allows Remote Attacks

Critical TP-Link Router Flaw Allows Remote Attacks

Posted on August 3, 2026 By CWS

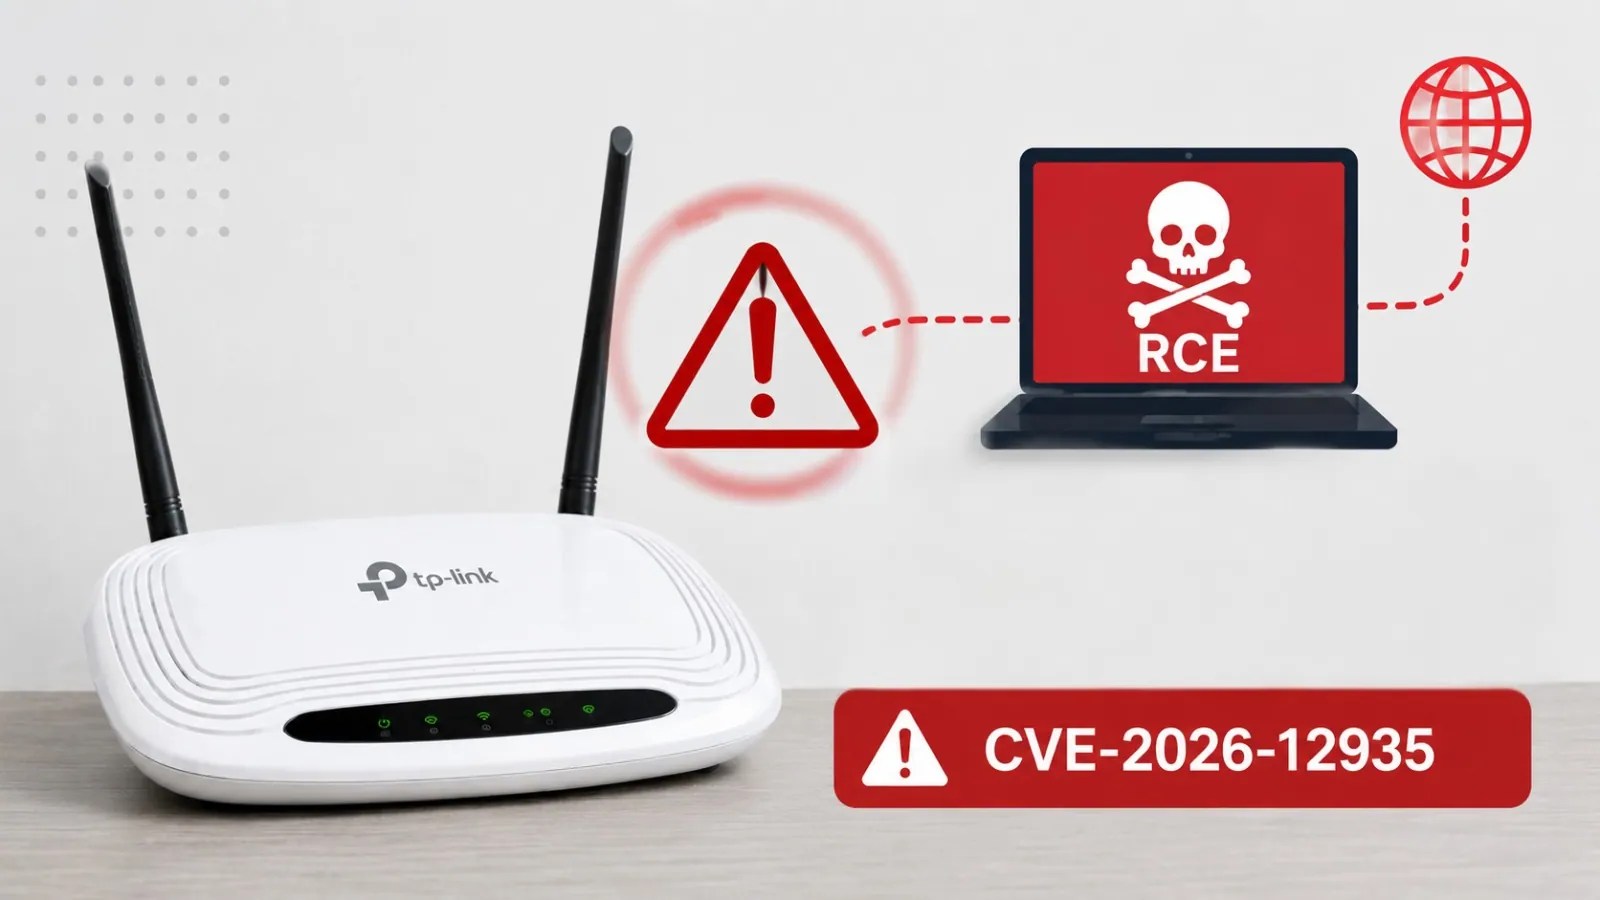
TP-Link has disclosed a significant security vulnerability in its TL-WR940N V6 wireless router that poses a serious threat to users. The flaw, identified as CVE-2026-12935, enables remote code execution and denial-of-service attacks on affected devices. This vulnerability is a critical concern for both individual users and organizations relying on these routers for network connectivity.

Understanding the Vulnerability

The core issue resides in the router’s RTSP connection tracking feature. RTSP, or Real-Time Streaming Protocol, facilitates control over multimedia streaming. In this instance, the vulnerability stems from a stack-based buffer overflow within the RTSP kernel module. When excessively crafted data surpasses the allocated buffer, it leads to memory corruption.

Exploitation occurs when an attacker operates a malicious RTSP server, tricking a local network device into connecting. This connection can result in the delivery of harmful RTSP messages, which the vulnerable module incorrectly processes, causing memory corruption and potential remote code execution.

Implications of Remote Exploitation

Executing code remotely on the TL-WR940N V6 router has severe security implications. Attackers could manipulate network settings, intercept traffic, alter DNS configurations, or install persistent malware. Furthermore, compromised routers might serve as launch points for attacks on other network devices, amplifying the threat.

With a CVSS v4.0 score of 8.7, this vulnerability is classified as High risk. It has a network-based attack vector requiring minimal complexity and no authentication. However, exploitation necessitates user interaction, specifically a LAN client initiating contact with the rogue RTSP server.

Mitigation and Recommendations

TP-Link has addressed this issue by releasing firmware updates tailored to specific regions and hardware versions. Users should ensure their router’s hardware version and regional firmware match before installation. The updated firmware versions are (EN)_V6_260528 for English, (US)_V6_260528 for the US, and (JP)_V6_260527 for Japanese models.

Until updates are applied, users should restrict unnecessary RTSP connections and monitor for unusual network activity. This includes unexpected reboots or configuration changes indicative of potential exploitation attempts.

TP-Link acknowledges Ryo Shimada of Powder Keg Technologies, Inc. for the responsible disclosure of this vulnerability. Timely firmware updates remain the best defense against this threat, ensuring network safety.

Cyber Security News Tags:attack vector, buffer overflow, CVE-2026-12935, Cybersecurity, denial of service, firmware update, network safety, network security, remote code execution, router security, router settings, RTSP, TP-Link, Vulnerability

Post navigation

Previous Post: Highlights from Black Hat USA 2026: Key Vendor Announcements
Next Post: Malware Threats to Google Password Manager Accounts Revealed

Related Posts

Critical SimpleHelp Vulnerability Poses Security Risks Critical SimpleHelp Vulnerability Poses Security Risks Cyber Security News
Malicious npm Package Exploits Hugging Face for Cyber Attacks Malicious npm Package Exploits Hugging Face for Cyber Attacks Cyber Security News
Hackers Exploit Shopify’s Shop App with Phony Invoices Hackers Exploit Shopify’s Shop App with Phony Invoices Cyber Security News
Critical ServiceNow Flaw Under Active Exploitation Critical ServiceNow Flaw Under Active Exploitation Cyber Security News
Boosting SOC Efficiency with Threat Intelligence Boosting SOC Efficiency with Threat Intelligence Cyber Security News
Leading ASPM Platforms of 2026: A Comprehensive Overview Leading ASPM Platforms of 2026: A Comprehensive Overview Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Northflank Urges Secret Rotation After Security Breach
  • Florida Education Site Breach Risks Data of Millions
  • AI-Driven Cyber Attacks Target Government Linux Servers
  • Hackers Exploit Microsoft Teams for Remote Access
  • October 2026 Cybersecurity M&A: Key Deals Overview

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Northflank Urges Secret Rotation After Security Breach
  • Florida Education Site Breach Risks Data of Millions
  • AI-Driven Cyber Attacks Target Government Linux Servers
  • Hackers Exploit Microsoft Teams for Remote Access
  • October 2026 Cybersecurity M&A: Key Deals Overview

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark