Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Exploit Released for Splunk Secure Gateway Vulnerability

Exploit Released for Splunk Secure Gateway Vulnerability

Posted on June 29, 2026 By CWS

A recent public disclosure highlights a significant security flaw, identified as CVE-2026-20251, in Splunk Secure Gateway (SSG). This vulnerability, which has been rated with a CVSS score of 8.8, poses a high-severity risk, allowing attackers to execute code on a Splunk server without high-level access.

Understanding the Vulnerability

The vulnerability is found in the alert processing pipeline of Splunk Secure Gateway. It involves the App Key Value Store (KV Store), notably the mobile_alerts collection, which inadvertently processes attacker-controlled documents. The flaw arises when these documents are processed by jsonpickle.decode(), a Python library designed to deserialize JSON.

Despite using the safe=True parameter, which is meant to block certain evaluations, critical tags such as py/reduce and py/object remain vulnerable. This oversight allows attackers to exploit these tags and execute arbitrary commands.

Exploiting the Flaw

To exploit this vulnerability, a low-privileged Splunk account is sufficient. Attackers can insert a malicious document into the mobile_alerts collection through the Splunk REST API. Upon request processing, the crafted document bypasses the check_alert_data_valid_json validator due to its structure, specifically a py/object key.

When the document is processed, jsonpickle.decode() reconstructs the malicious object, leading to the execution of arbitrary commands on the operating system. This method of exploitation effectively bypasses security checks, highlighting a major security concern.

Mitigation and Recommendations

Researcher Fady Oueslati of ReactiveZero Security Research released a proof-of-concept (PoC) for this vulnerability on June 26, 2026. This PoC, identified as 2026FO-SPLUNK-20251, demonstrates how the validator can be bypassed and commands executed even with safe=True enabled.

Organizations using Splunk Secure Gateway should upgrade to versions 3.9.20, 3.10.6, or 3.8.67. Additionally, Splunk Enterprise should be updated to versions 10.0.7 or higher. If immediate patching is not possible, disabling or removing the Splunk Secure Gateway app is advised as a temporary solution, though it will impact certain functionalities.

To further mitigate risk, security teams should enforce least-privilege principles, restrict write access to the mobile_alerts collection, and replace jsonpickle.decode() with more secure parsing methods.

In response to this vulnerability, integrating comprehensive threat detection tools into your security operations center (SOC) can enhance your organization’s security posture and ensure rapid response to potential threats.
Cyber Security News Tags:CVE-2026-20251, Cybersecurity, Deserialization, Exploit, IT, RCE, Security, Software, Splunk, Vulnerability

Post navigation

Previous Post: WhatsApp Introduces Usernames for Enhanced Privacy
Next Post: WhatsApp Introduces Usernames for Enhanced Privacy

Related Posts

Ransomware Actors Targeting Global Public Sectors and Critical Services in Targeted Attacks Ransomware Actors Targeting Global Public Sectors and Critical Services in Targeted Attacks Cyber Security News
Beware of Malicious Facebook Ads With Meta Verified Steals User Account Details Beware of Malicious Facebook Ads With Meta Verified Steals User Account Details Cyber Security News
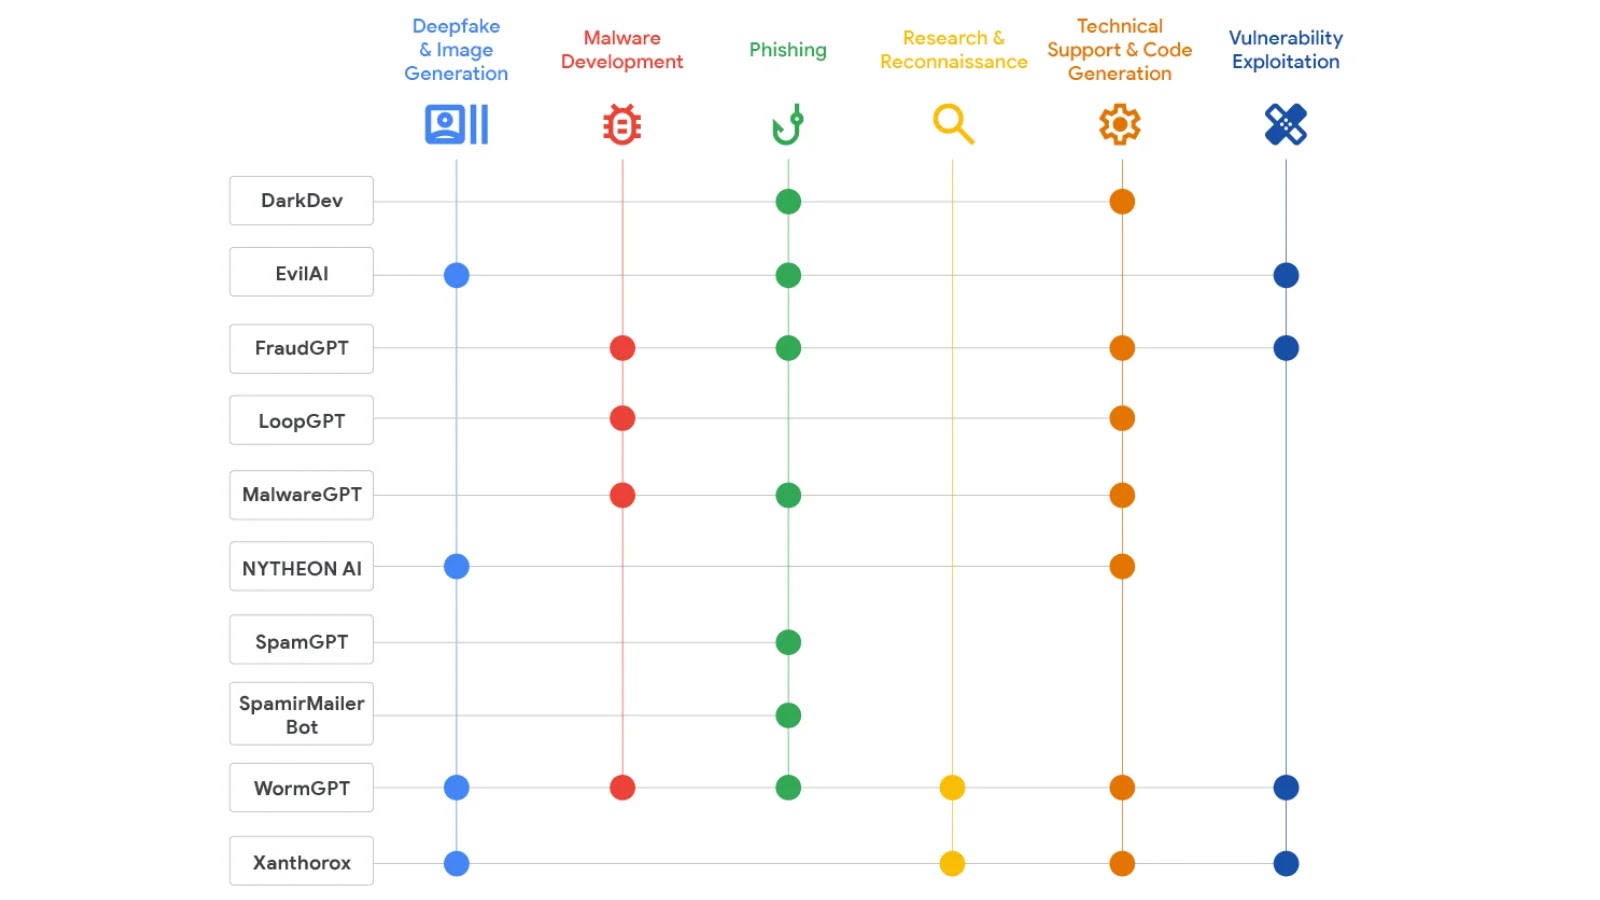
List of AI Tools Promoted by Threat Actors in Underground Forums and Their Capabilities List of AI Tools Promoted by Threat Actors in Underground Forums and Their Capabilities Cyber Security News
Malicious NuGet Packages Mimic as Popular Nethereum Project to Steal Wallet Keys Malicious NuGet Packages Mimic as Popular Nethereum Project to Steal Wallet Keys Cyber Security News
Iranian APTs Hackers Actively Attacking Transportation and Manufacturing Sectors Iranian APTs Hackers Actively Attacking Transportation and Manufacturing Sectors Cyber Security News
Payload Ransomware Threatens Global Systems with Advanced Encryption Payload Ransomware Threatens Global Systems with Advanced Encryption Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Wireshark 4.6.9: Security Enhancements Address 19 Flaws
  • New Windows Attack Bypasses EDR with Process Injection
  • Citrix Urges Immediate Update for NetScaler Vulnerabilities
  • Microsoft SharePoint Vulnerability CVE-2026-65660 Under Attack
  • Unpatched Citrix NetScaler Flaws Pose Security Threat

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Wireshark 4.6.9: Security Enhancements Address 19 Flaws
  • New Windows Attack Bypasses EDR with Process Injection
  • Citrix Urges Immediate Update for NetScaler Vulnerabilities
  • Microsoft SharePoint Vulnerability CVE-2026-65660 Under Attack
  • Unpatched Citrix NetScaler Flaws Pose Security Threat

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark