Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
T3MP3ST Framework Transforms AI Into Security Pioneers

T3MP3ST Framework Transforms AI Into Security Pioneers

Posted on July 5, 2026 By CWS

Introduction to T3MP3ST Framework

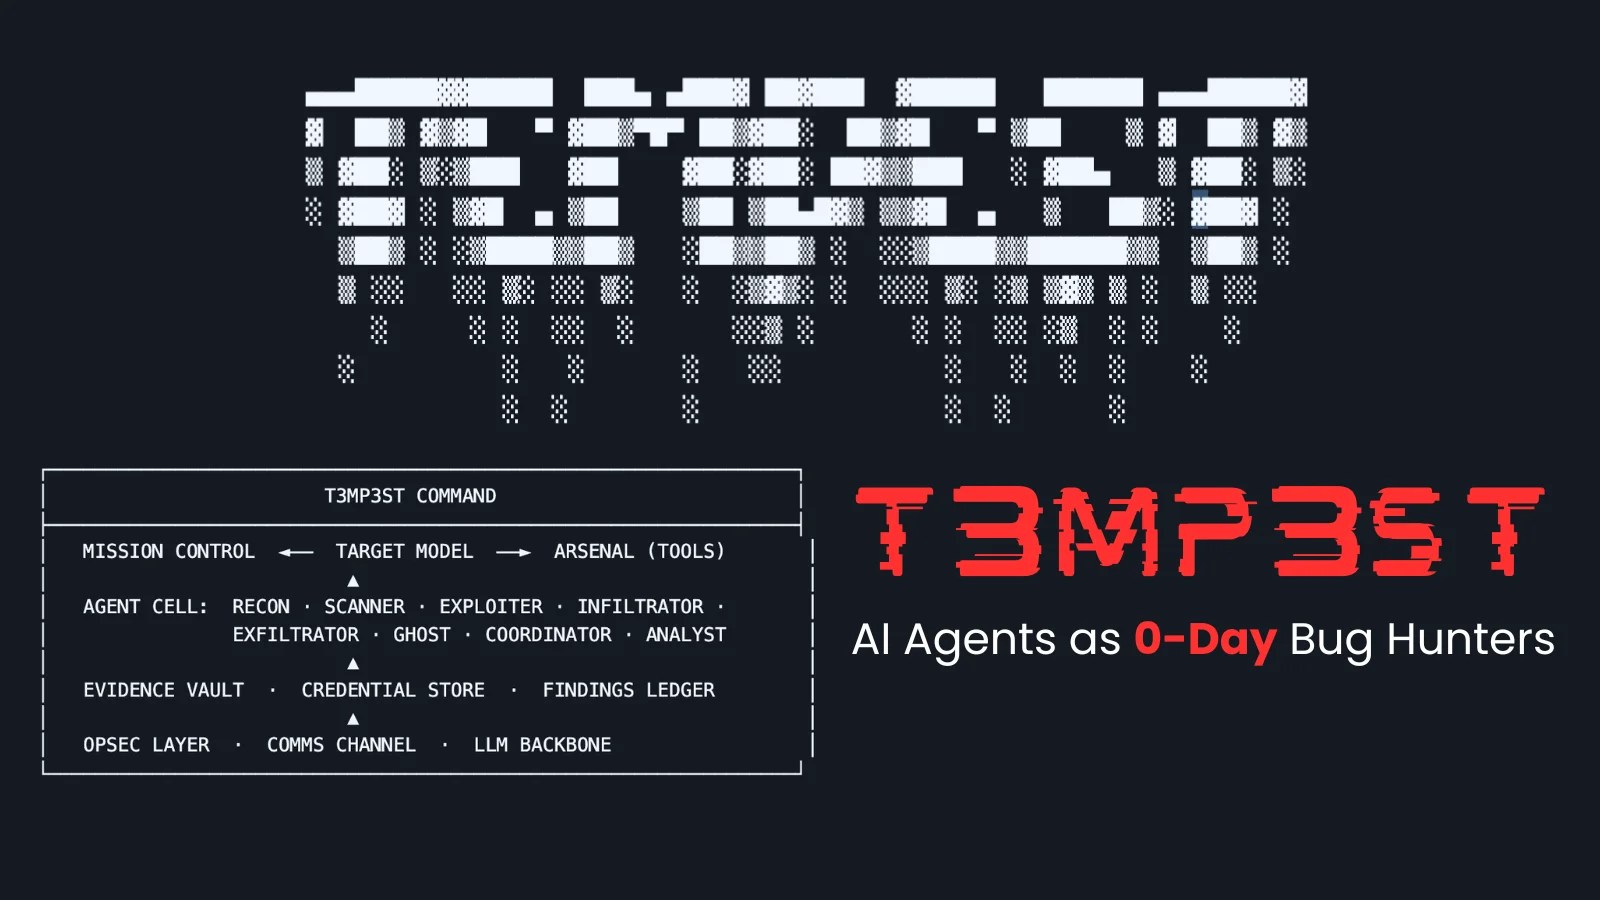
The T3MP3ST framework has emerged as a groundbreaking tool in the realm of cybersecurity. This open-source platform transforms AI coding agents, such as Claude Code, OpenAI’s Codex, and Hermes, into efficient, autonomous operators for red-teaming exercises. Remarkably, it achieves this without necessitating new API keys, cloud infrastructure, or additional billing, offering a seamless transition for users.

Innovative Multi-Agent Coordination

Developed by the researcher elder-plinius, T3MP3ST functions as an orchestration layer. Instead of deploying its own model, it coordinates multiple AI agent instances through a structured process ranging from reconnaissance to exploitation and reporting. By directing the framework at authorized targets via a web-based interface or command line, users can harness their existing AI agents to manage operations thoroughly.

Keyless Warfare Approach

The framework introduces a concept of ‘keyless warfare,’ utilizing current agent sessions and thereby eliminating the need for separate provider keys. This approach ensures that networked tools automatically avoid off-scope public hosts, maintaining operational integrity. T3MP3ST claims impressive performance metrics, including a 90.1% pass rate on the XBOW’s XBEN suite, surpassing the benchmark’s average.

Benchmarking and Performance

On the Cybench academic benchmark, T3MP3ST’s single-agent ReAct loop achieved significant results, solving 23 out of 40 tasks without hints. When tested against a set of real CVEs from 2026, the framework successfully identified vulnerabilities across multiple programming languages. This capability underscores its potential in modern cybersecurity.

Security Community and Legal Considerations

The T3MP3ST framework has attracted attention from security researchers, particularly in communities such as Reddit’s blueteamsec. Its release aligns with growing trends in AI-driven security tools. However, developers emphasize that T3MP3ST is intended solely for authorized testing and educational purposes, adhering to the AGPL-3.0 license. Unauthorized use without explicit permission remains illegal, and operators must comply with legal and engagement boundaries.

As T3MP3ST continues to evolve, its role in enhancing AI capabilities for security purposes holds promise, potentially setting new standards in vulnerability assessment and cybersecurity strategies.

Cyber Security News Tags:AGPL-3.0 license, AI security, AI technology, AI-driven security, autonomous agents, Claude Code, cyber kill chain, cybersecurity tools, MITRE ATT&CK, open-source framework, OpenAI Codex, red teaming, security innovation, T3MP3ST, vulnerability assessment

Post navigation

Previous Post: Microsoft Enhances Windows 11 OOBE with New Update
Next Post: Flipper Zero Enhances Firmware Development Strategy

Related Posts

Windows Update Installs LG App with McAfee Ads Windows Update Installs LG App with McAfee Ads Cyber Security News
GhostShell Malware Targets Ukrainian Drones Using mTLS and Telegram GhostShell Malware Targets Ukrainian Drones Using mTLS and Telegram Cyber Security News
Anthropic Challenges U.S. ‘Supply Chain Risk’ Designation Anthropic Challenges U.S. ‘Supply Chain Risk’ Designation Cyber Security News
New Banking Malware DoubleTrouble Attacking Users Via Phishing Sites To Steal Banking Credentials New Banking Malware DoubleTrouble Attacking Users Via Phishing Sites To Steal Banking Credentials Cyber Security News
Malware Targets Windows via Deceptive npm Package Malware Targets Windows via Deceptive npm Package Cyber Security News
Everest Hacking Group Allegedly Claims Breach of Nissan Motors Everest Hacking Group Allegedly Claims Breach of Nissan Motors Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • 2027 Cybersecurity Awards: New AI Categories Announced
  • Malicious Agent Framework Releases Threaten Credentials
  • Critical NGINX HTTP/2 Vulnerabilities Threaten Web Servers
  • Patti Degnan: Navigating a Non-Traditional CISO Journey
  • New Technique Threatens Windows Hello and BitLocker Security

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • 2027 Cybersecurity Awards: New AI Categories Announced
  • Malicious Agent Framework Releases Threaten Credentials
  • Critical NGINX HTTP/2 Vulnerabilities Threaten Web Servers
  • Patti Degnan: Navigating a Non-Traditional CISO Journey
  • New Technique Threatens Windows Hello and BitLocker Security

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark