Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Discord Bug Affects Over 8,000 Accounts in Security Mishap

Discord Bug Affects Over 8,000 Accounts in Security Mishap

Posted on July 8, 2026 By CWS

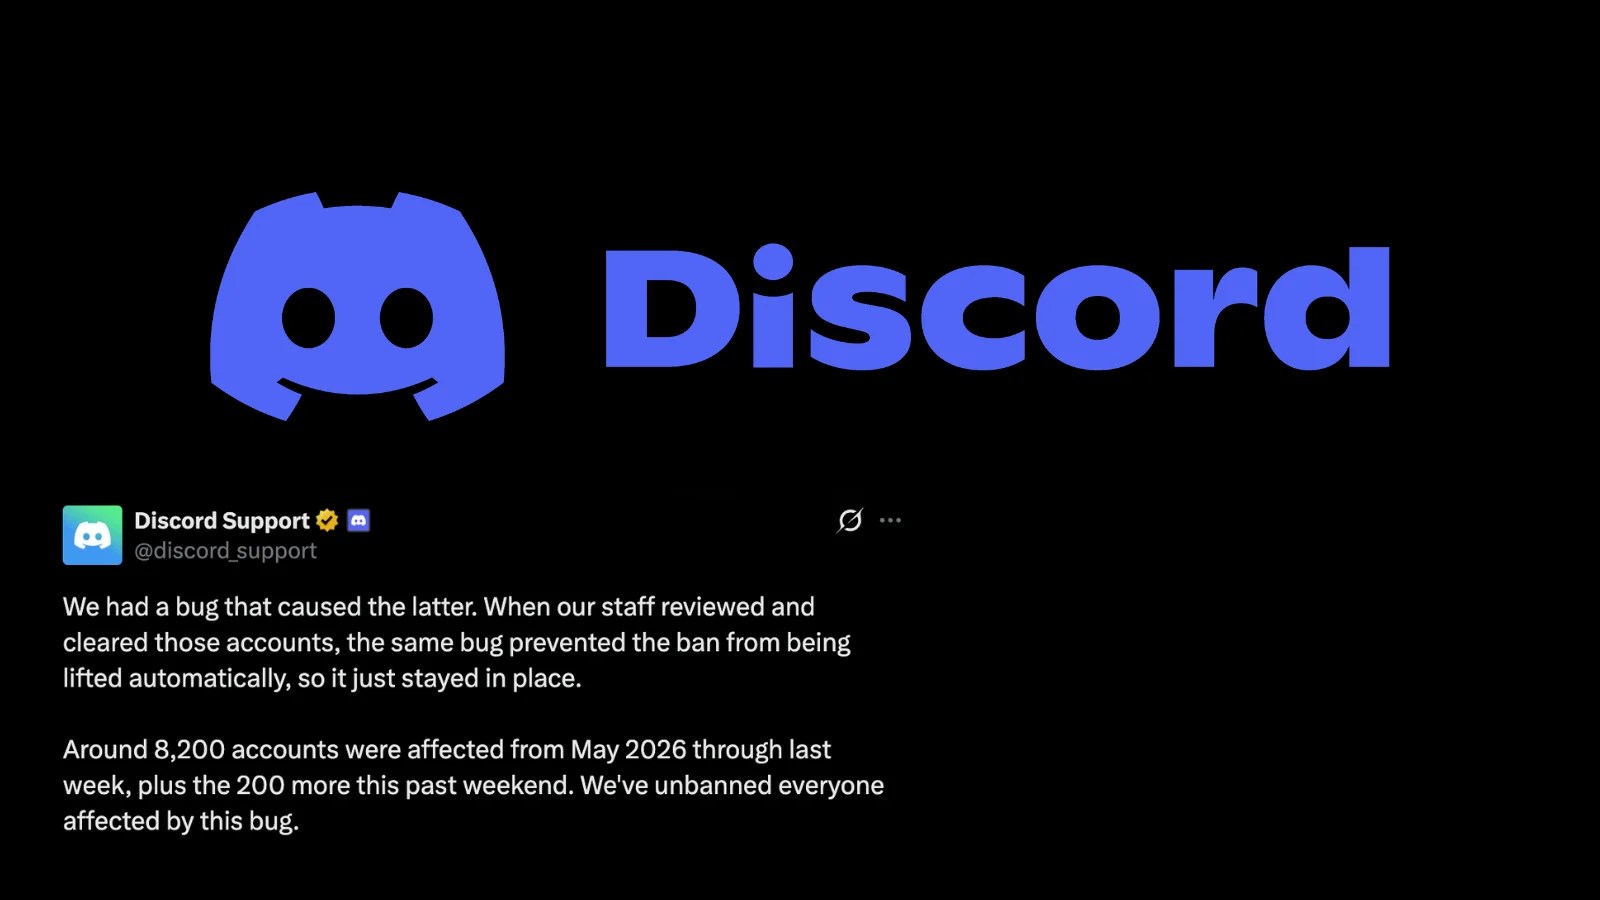
In a recent announcement, Discord revealed a significant error in its automated security systems, which inadvertently led to the suspension of over 8,000 user accounts between May and early July 2026. This issue was brought to light through Discord’s official support channel on X, where the company outlined the problem’s origin and the extent of its impact.

Root Cause and Initial Detection

The problem originated from a dual failure in Discord’s moderation system. Initially, the automated detection tools mistakenly identified normal user activities as violations of community guidelines, resulting in unwarranted suspensions. These detection mechanisms generally rely on algorithms designed to recognize spam or abusive behavior, though the exact trigger in this case remains unspecified.

The situation worsened when attempts to rectify the wrongful bans were thwarted by a secondary bug. Despite manual reviews by Discord’s Trust & Safety team, which cleared the flagged accounts, the system failed to execute the unban process, leaving affected users locked out.

Impact and Resolution Process

Discord Support acknowledged the significant lapse in their unban procedures, leading to prolonged account suspensions despite being cleared internally. Approximately 8,200 accounts were affected during the initial period, with an additional 200 accounts encountering issues the following weekend, totaling over 8,400 impacted users.

This incident suggests a delay in identifying and addressing the anomaly, raising questions about the effectiveness of Discord’s internal monitoring systems. Users faced extended periods without access to their accounts, negatively impacting their ability to interact with the community.

Systemic Implications and Future Measures

Discord has since unbanned all affected accounts, though they have not provided specific details on the technical adjustments made to their moderation framework. The company has not disclosed whether users will receive further communication or compensation beyond the public announcement.

This event highlights a systemic issue with automated moderation systems at scale. While false positives are a known risk, the inability to resolve flagged errors due to internal bugs underscores the need for robust appeal processes. Such failures can leave users unjustly locked out for extended periods, even after manual corrections.

For Discord, a platform serving hundreds of millions of users, the impact on 8,000 accounts may seem minor statistically. However, it underscores the critical need for resilient and transparent systems to prevent and quickly address such errors in the future.
Cyber Security News Tags:2026, Automation, Bug, Discord, false positives, Moderation, platform scale, Security, trust and safety, user accounts

Post navigation

Previous Post: China-Based APT UAT-7810 Enhances ORB Network with LONGLEASH
Next Post: CISA Demands Urgent Patch for Critical Software Vulnerabilities

Related Posts

Developers Frustrated by ‘No Server Available’ Message Developers Frustrated by ‘No Server Available’ Message Cyber Security News
Salmon Launches EVI to Secure AI and Autonomous Systems Salmon Launches EVI to Secure AI and Autonomous Systems Cyber Security News
LANSCOPE Endpoint Manager Vulnerability Let Attackers Execute Remote Code LANSCOPE Endpoint Manager Vulnerability Let Attackers Execute Remote Code Cyber Security News
Chinese Hackers Weaponized Nezha Tool to Execute Commands on Web Server Chinese Hackers Weaponized Nezha Tool to Execute Commands on Web Server Cyber Security News
Graphite Spyware Exploits Apple iOS Zero-Click Vulnerability to Attack Journalists Graphite Spyware Exploits Apple iOS Zero-Click Vulnerability to Attack Journalists Cyber Security News
Germany Urges Apple, Google to Block Chinese AI App DeepSeek Over Privacy Rules Germany Urges Apple, Google to Block Chinese AI App DeepSeek Over Privacy Rules Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • CrowdStrike Considers Zscaler Acquisition in Major Cybersecurity Move
  • AI Exploits Zero-Day in Medical Imaging Software
  • Chinese AI Exploits Zero-Day Vulnerability in Medical Software
  • Critical Flaw in GPGME Poses Data Risk Via Malicious Keys
  • Researchers Expose Meta Muse Vulnerability Allowing Chat Hijacking

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • CrowdStrike Considers Zscaler Acquisition in Major Cybersecurity Move
  • AI Exploits Zero-Day in Medical Imaging Software
  • Chinese AI Exploits Zero-Day Vulnerability in Medical Software
  • Critical Flaw in GPGME Poses Data Risk Via Malicious Keys
  • Researchers Expose Meta Muse Vulnerability Allowing Chat Hijacking

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark