Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical Veeam ONE Flaws Enable Remote Code Execution

Critical Veeam ONE Flaws Enable Remote Code Execution

Posted on August 5, 2026 By CWS

Veeam has announced urgent security patches for Veeam ONE version 13.1, addressing several vulnerabilities that pose significant security risks. These flaws could allow malicious actors to execute unauthorized code, access confidential files, and elevate user privileges.

Critical Vulnerability Details

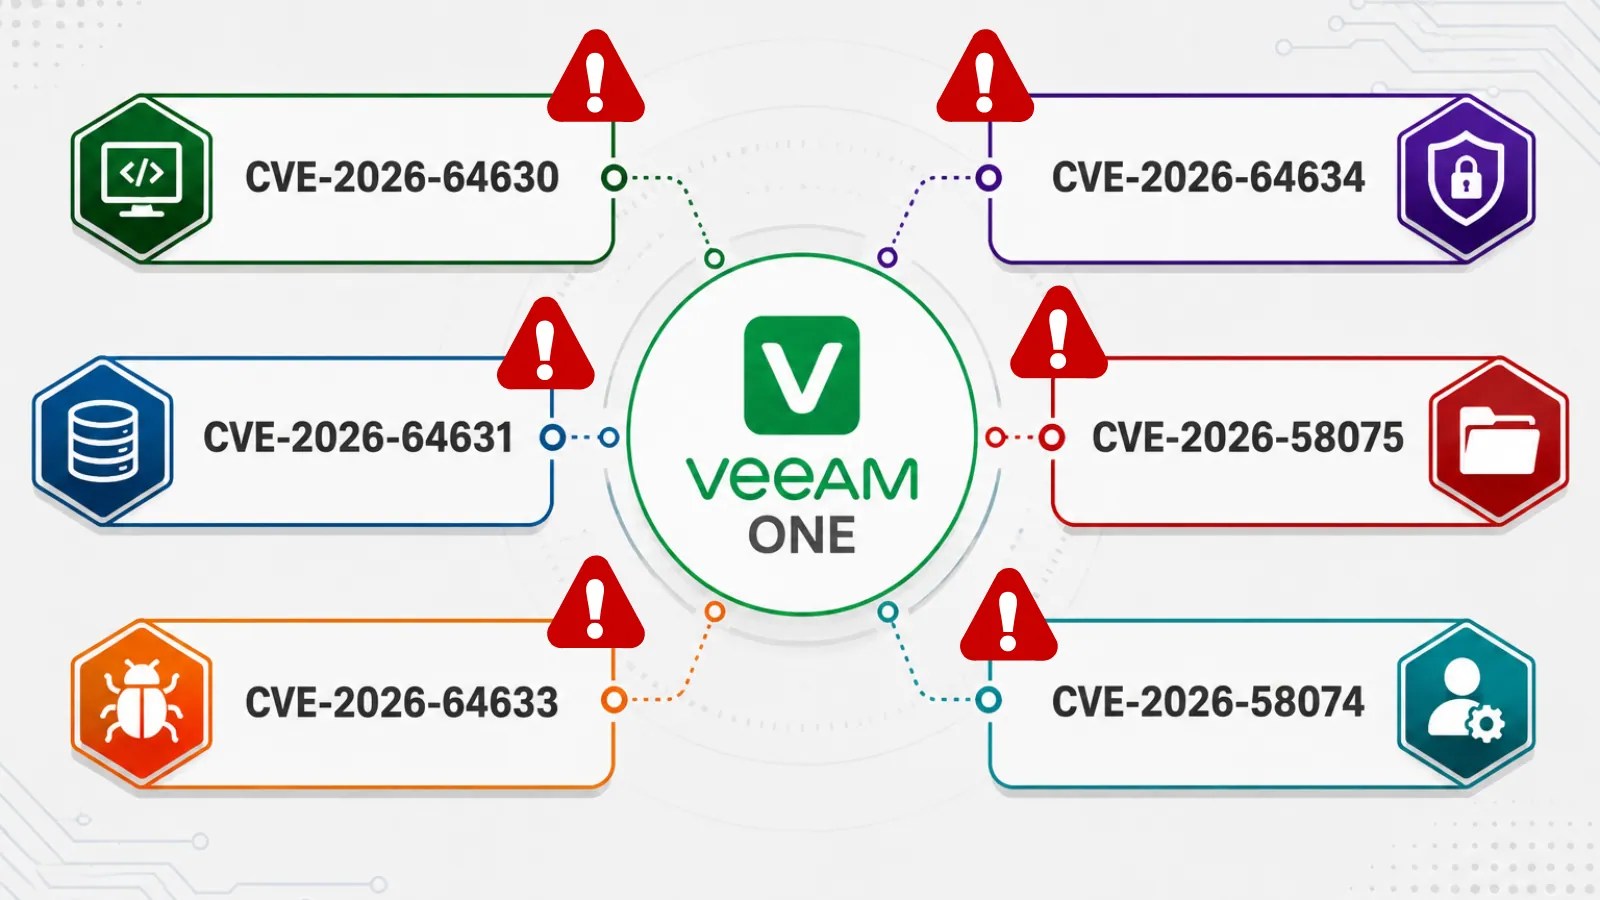
Among the issues addressed, the vulnerability identified as CVE-2026-64633 stands out with a critical CVSS v4.0 score of 10.0. This flaw permits unauthenticated remote code execution on the Veeam ONE agent host, presenting a severe threat to affected systems.

The vulnerabilities impact Veeam ONE 13.0.2.6723 and earlier 13 series builds. It is imperative for organizations utilizing these versions to upgrade to Veeam ONE 13.1.0.7034, which resolves the vulnerabilities detailed in Veeam’s Knowledge Base article KB4892.

Additional High-Risk Vulnerabilities

Another significant issue, CVE-2026-58075, allows attackers to read arbitrary files without authentication. This could lead to unauthorized access to sensitive information such as configuration files and credentials. Additionally, CVE-2026-58074, which targets high-privileged users, enables arbitrary code execution on the Veeam ONE server, posing a risk of increased control for attackers.

Furthermore, the advisory addresses CVE-2026-64631, a SQL injection vulnerability that allows low-privileged users to extract database information, potentially aiding attackers in mapping valuable infrastructure details.

Mitigation and Response Measures

Veeam also patched CVE-2026-64634, a flaw that can be exploited for local privilege escalation within the Reporter service, and CVE-2026-64630, which allows unauthorized report access. The latter was reported as a medium-severity issue.

Several vulnerabilities were identified through HackerOne, while CVE-2026-58074 was discovered internally. Veeam cautions that attackers may reverse-engineer patches post-disclosure to target unpatched systems.

Recommendations for Organizations

Security teams are advised to verify all Veeam ONE version 13 deployments and ensure updates to version 13.1.0.7034 are applied promptly. It is essential to review server and agent exposure, limit access to trusted personnel, and monitor for unusual activity.

Organizations should remain vigilant in investigating anomalous database queries, unauthorized report access, or unexpected code execution events to safeguard against potential breaches.

Enhance your Security Operations Center by integrating threat detection tools and accelerating response strategies to address these vulnerabilities effectively.
Cyber Security News Tags:code execution, CVE-2026-58074, CVE-2026-58075, CVE-2026-64633, cyber threats, Cybersecurity, data protection, HackerOne, local privilege escalation, security update, software patch, SQL injection, threat detection, Veeam ONE, Vulnerabilities

Post navigation

Previous Post: QuickFox VPN Targeted in Supply Chain Attack Exposing Users
Next Post: Cyberattacks on Water Systems Impact Multiple US States

Related Posts

81% Router Usres Have Not Changed Default Admin Passwords, Exposing Devices to Hackers 81% Router Usres Have Not Changed Default Admin Passwords, Exposing Devices to Hackers Cyber Security News
Remote File Upload Vulnerability in Cisco Meeting Management Remote File Upload Vulnerability in Cisco Meeting Management Cyber Security News
Microsoft to Cancel Plans Imposing Daily Limit For Exchange Online Bulk E-mails Microsoft to Cancel Plans Imposing Daily Limit For Exchange Online Bulk E-mails Cyber Security News
Best Network Security Providers for Healthcare Best Network Security Providers for Healthcare Cyber Security News
New MacSync Stealer Uses Signed macOS App to Evade Gatekeeper and Steal Data New MacSync Stealer Uses Signed macOS App to Evade Gatekeeper and Steal Data Cyber Security News
ModernStealer: Allegations of Government Data Leaks ModernStealer: Allegations of Government Data Leaks Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • CISA Alerts on Linux Kernel Flaws Under Active Attack
  • TigerByte Cyber Launches with $3M Funding to Enhance Security
  • Identity Visibility: Key to Secure IAM by 2026
  • SolarWinds Fixes Critical ARM Security Flaw
  • Hackers Exploit TanStack to Steal GitHub Repositories

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • CISA Alerts on Linux Kernel Flaws Under Active Attack
  • TigerByte Cyber Launches with $3M Funding to Enhance Security
  • Identity Visibility: Key to Secure IAM by 2026
  • SolarWinds Fixes Critical ARM Security Flaw
  • Hackers Exploit TanStack to Steal GitHub Repositories

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark