Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Anthropic Enhances Security with Claude Code Auto Mode

Anthropic Enhances Security with Claude Code Auto Mode

Posted on August 10, 2026 By CWS

Anthropic has introduced a significant shift in security for its Claude Code platform, moving towards an automated system known as auto mode to handle potentially risky commands. This change aims to reduce reliance on continuous human approval, enhancing both efficiency and safety.

Implementation of Auto Mode

Starting on August 14, 2026, auto mode will become the default for new sessions under Claude Code’s Pro, Max, and Team plans. This transition signifies a pivotal change in balancing autonomy with security for AI coding agents.

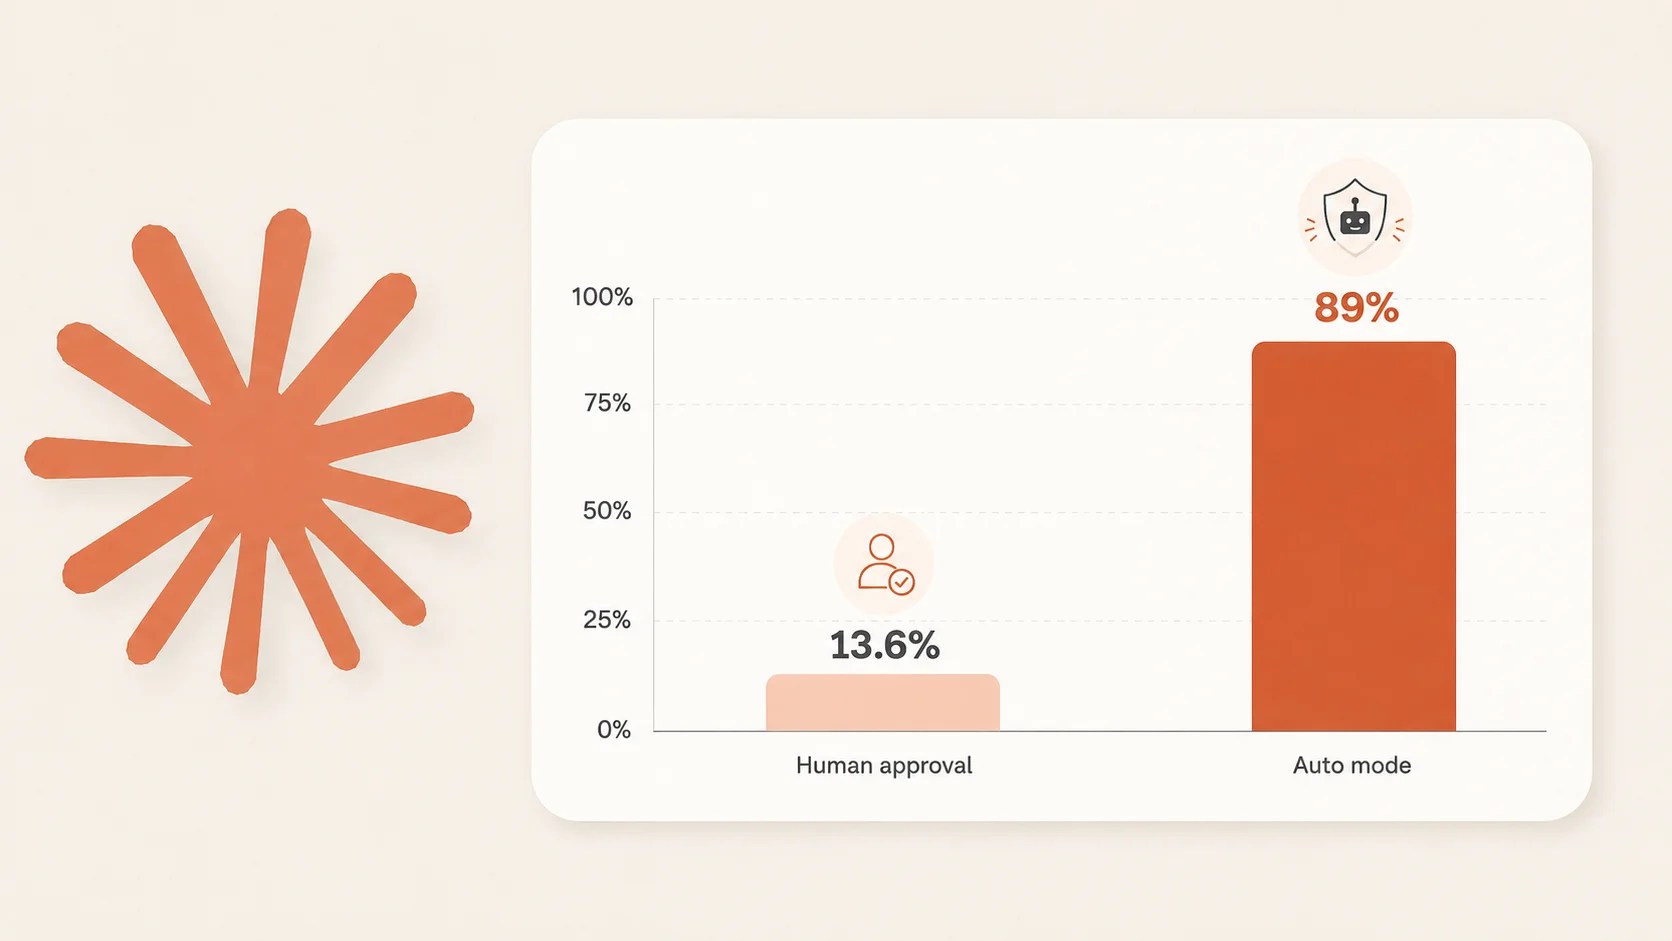
Months of rigorous testing compared manual approval processes with automated reviews. Results indicated that human reviewers often approved requests without thorough examination, approving 97% of them. This complacency resulted in a security gap, where human reviewers detected only 13.6% of dangerous commands, while auto mode identified 89% of these threats.

Performance and Reliability

During the evaluation, auto mode successfully blocked 800 commands that would have otherwise been approved by human reviewers, who only blocked 6 commands that auto mode missed. The human detection rate decreased significantly over time, whereas auto mode maintained a consistent performance.

Auto mode is designed to classify and block commands that are destructive or exceed the user’s environment. If risky actions are detected, Claude Code suggests safer alternatives or requests user confirmation. Upon encountering multiple risky instances, the system reverts to manual approvals.

Industry Adoption and Benefits

Auto mode has demonstrated resilience against advanced threats, reducing the miss rate during adversarial tests and successfully preventing real incidents at Anthropic. This includes stopping potential data leaks and unauthorized access attempts.

The feature allows Claude to operate autonomously for extended periods, which is beneficial for long-duration projects. Companies like Adobe and Nuro have adopted auto mode, reporting increased productivity and streamlined workflows.

While auto mode is currently an opt-in feature for Claude Enterprise and related platforms, Anthropic plans to expand its default application. The move is part of a growing trend towards automated risk management in AI development, offering a more reliable alternative to human oversight.

Anthropic’s decision to not charge additional fees for the auto mode’s token usage reflects their commitment to advancing AI security. This advancement highlights the potential for automated systems to enhance AI coding practices, paving the way for future innovations.

Cyber Security News Tags:AI development, AI security, Anthropic, auto mode, automated safety, Claude Code, coding agents, Cybersecurity, enterprise solutions, Innovation, machine learning, risk management, Software, Technology

Post navigation

Previous Post: Windows 11 Vulnerabilities Expose MFA Flaws
Next Post: GitHub Enhances Malware Detection Across Multiple Ecosystems

Related Posts

Crédit Mutuel Arkéa Hit by Cyberattack, Security Strengthened Crédit Mutuel Arkéa Hit by Cyberattack, Security Strengthened Cyber Security News
New Security Guidelines Released to Combat Rogue AI Agents New Security Guidelines Released to Combat Rogue AI Agents Cyber Security News
Critical WordPress RCE Vulnerability Discovered by AI Critical WordPress RCE Vulnerability Discovered by AI Cyber Security News
Critical Microsoft SCCM Flaws Enable Remote Code Execution Critical Microsoft SCCM Flaws Enable Remote Code Execution Cyber Security News
PoC Published For Fortinet 0-Day Vulnerability That Being Exploited in the Wild PoC Published For Fortinet 0-Day Vulnerability That Being Exploited in the Wild Cyber Security News
Cl0p Ransomware Actively Exploiting Oracle E-Business Suite 0-Day Vulnerability in the Wild Cl0p Ransomware Actively Exploiting Oracle E-Business Suite 0-Day Vulnerability in the Wild Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • CISA Highlights SonicOS SSLVPN Security Weakness
  • GhostAction Campaign Targets 500 GitHub Accounts for Credentials
  • Notepad++ 8.9.9 Update Resolves Critical Security Flaws
  • Ethersphere Tools Breached, Malware Targets Wallets
  • Abe Office Malware Circumvents Chrome Security to Steal Data

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • CISA Highlights SonicOS SSLVPN Security Weakness
  • GhostAction Campaign Targets 500 GitHub Accounts for Credentials
  • Notepad++ 8.9.9 Update Resolves Critical Security Flaws
  • Ethersphere Tools Breached, Malware Targets Wallets
  • Abe Office Malware Circumvents Chrome Security to Steal Data

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark