Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
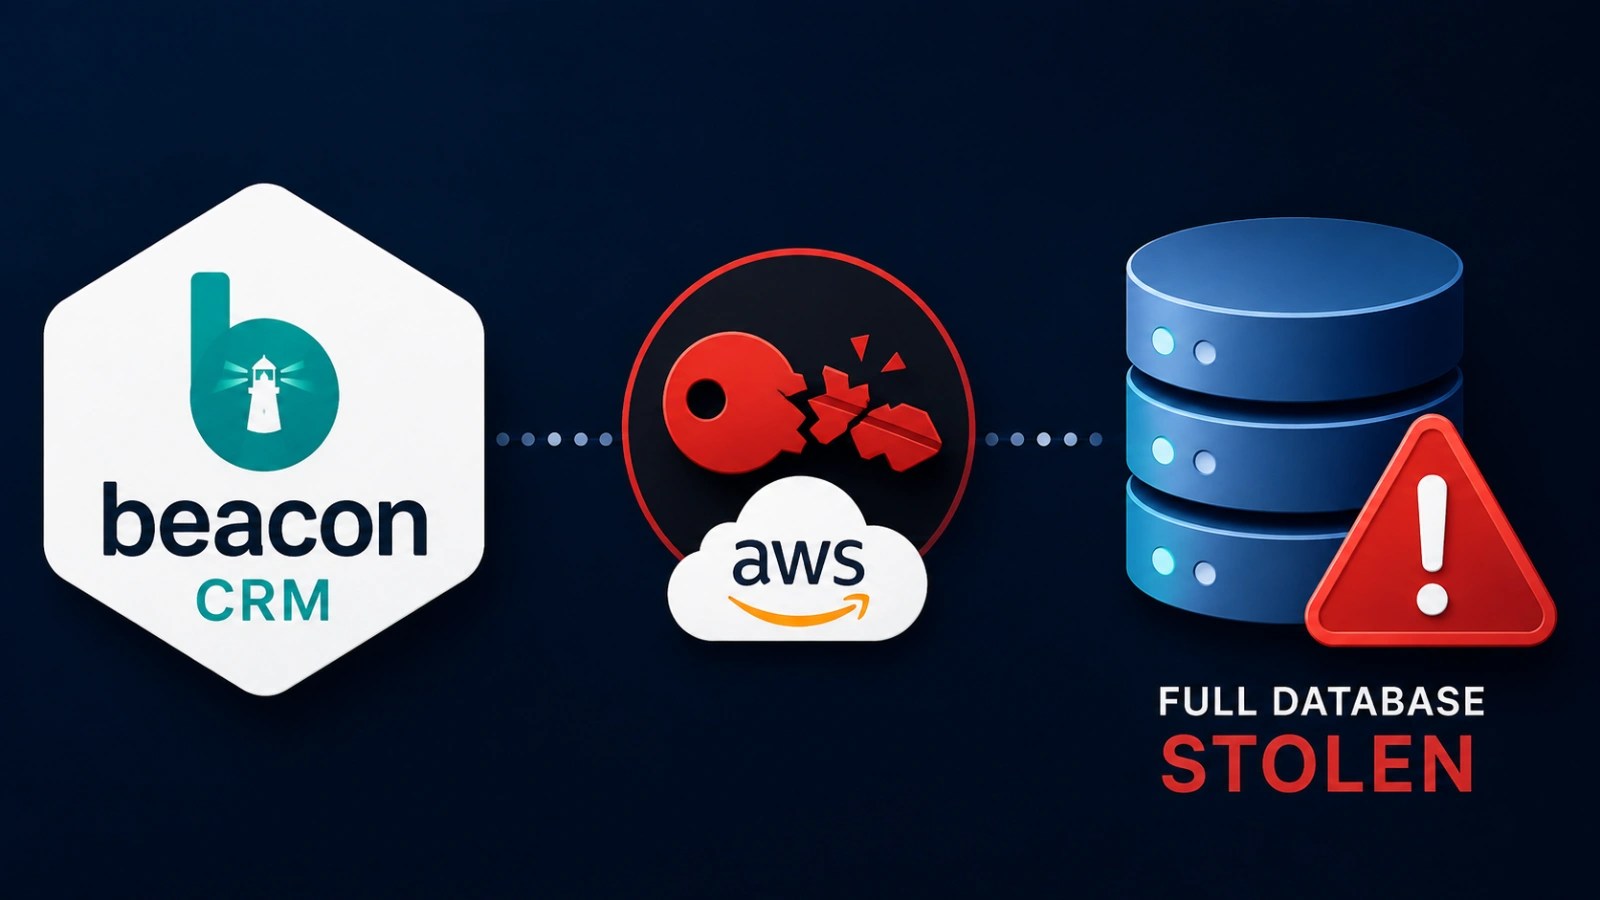
Beacon CRM Data Breach: Full Database Stolen After AWS Key Leak

Beacon CRM Data Breach: Full Database Stolen After AWS Key Leak

Posted on August 13, 2026 By CWS

Beacon, a CRM platform utilized by over a thousand UK charities, has revealed a significant data breach involving the theft of its entire customer database. This disclosure was made by CTO David Simpson on August 12, 2026, marking a critical update from previous communications.

Investigation and Breach Details

A thorough forensic investigation, conducted with cybersecurity experts, traced the breach to a compromised Amazon Web Services (AWS) access key. The key was inadvertently made public through JavaScript build artifacts on Beacon’s website. Such leaks can occur when environment variables or secret keys are included in code that becomes publicly accessible.

This exposure allowed unauthorized access, enabling the attacker to exfiltrate the database. The breach aligns with patterns seen in credential phishing attacks and automated scans targeting exposed cloud resources.

Timeline and Impact of the Data Theft

The official incident report from Beacon CRM indicates that the attack commenced on July 27, 2026. The unauthorized access lasted approximately 87 minutes, during which the entire database, including attachment files, was exfiltrated. AWS Cost and Usage reports confirmed a spike in data transfer on July 27 and 28, 2026, corroborating the database theft.

Despite maintaining data encryption at rest, the stolen AWS access key enabled the attacker to decrypt and download the data, as AWS decrypts data for valid credential holders automatically.

Response Actions and Regulatory Involvement

Beacon has taken several measures to address the breach: all AWS keys were revoked and rotated, sensitive data was removed from client-side scripts, and enhanced security tools were deployed across the enterprise. These actions aim to prevent future breaches and secure the infrastructure.

The incident has prompted investigations by the UK Charity Commission, the ICO, and Action Fraud. Affected organizations like Justice for Colombia and the Center for Sustainable Energy have started informing stakeholders about potential data exposure.

Beacon continues to monitor for any signs of the stolen data being sold or misused and advises clients to assess their notification obligations. A comprehensive report on the breach is forthcoming.
Cyber Security News Tags:AWS key, Beacon CRM, cloud security, credential theft, Cybersecurity, data theft, database breach, incident response, security breach, UK charities

Post navigation

Previous Post: Fortinet Addresses Critical Security Flaws in Key Products
Next Post: AmnesiaStealer Malware Targets macOS Through Fake Sites

Related Posts

OnePlus OxygenOS Vulnerability Allows Any App to Read SMS Data Without Permission OnePlus OxygenOS Vulnerability Allows Any App to Read SMS Data Without Permission Cyber Security News
UNC6692 Exploits Microsoft Teams for SNOW Malware Attack UNC6692 Exploits Microsoft Teams for SNOW Malware Attack Cyber Security News
Elephant APT Group Attacking Defense Industry Leveraging VLC Player, and Encrypted Shellcode Elephant APT Group Attacking Defense Industry Leveraging VLC Player, and Encrypted Shellcode Cyber Security News
PyPI Package Compromised by Malicious Scripts PyPI Package Compromised by Malicious Scripts Cyber Security News
Critical Johnson Controls Products Vulnerabilities Enables Remote SQL Injection Attacks Critical Johnson Controls Products Vulnerabilities Enables Remote SQL Injection Attacks Cyber Security News
5 Malicious Chrome Extensions Attacking Enterprise HR and ERP Platforms for Complete Takeover 5 Malicious Chrome Extensions Attacking Enterprise HR and ERP Platforms for Complete Takeover Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • CISA Alerts on Citrix NetScaler Vulnerabilities Exploitation
  • DC Health Data Breach Affects Nearly 400,000 Records
  • Critical Citrix NetScaler Flaws Exploited Globally, Warns CISA
  • PHP Addresses Security Flaw Exposing Sensitive Data
  • Jury Rules Facebook Misled Users on Privacy in New Mexico

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • CISA Alerts on Citrix NetScaler Vulnerabilities Exploitation
  • DC Health Data Breach Affects Nearly 400,000 Records
  • Critical Citrix NetScaler Flaws Exploited Globally, Warns CISA
  • PHP Addresses Security Flaw Exposing Sensitive Data
  • Jury Rules Facebook Misled Users on Privacy in New Mexico

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark