Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Web3 Job Scam Delivers NeedleStealer and hVNC RAT

Web3 Job Scam Delivers NeedleStealer and hVNC RAT

Posted on August 17, 2026 By CWS

Cybersecurity experts have uncovered a sophisticated scheme targeting cryptocurrency professionals through fake Web3 job interviews. This tactic involves deploying malware such as NeedleStealer and hVNC RAT, capitalizing on job seekers’ vulnerability.

Deceptive Recruitment Tactics

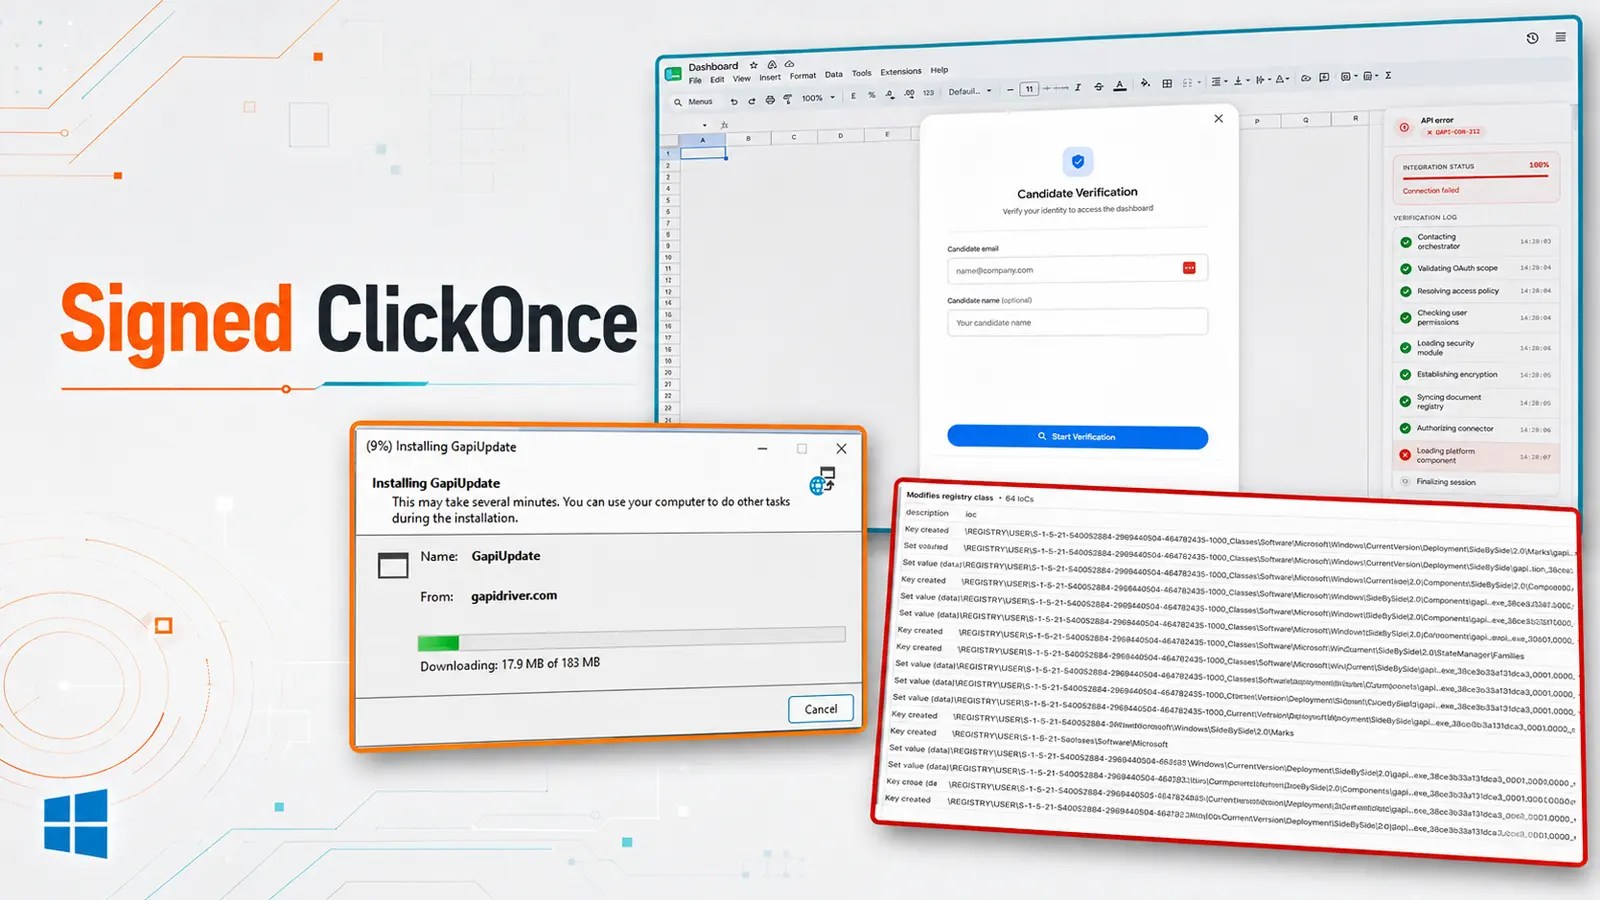
The attack begins with a LinkedIn recruiter approach, followed by scheduled interviews via Calendly and a technical test presented as a Google Sheet. However, instead of a benign document, the victim is led to a signed Microsoft ClickOnce application, often perceived as secure by Windows users. This approach successfully duped a cryptocurrency organization in July 2026, highlighting how real career transitions are exploited over generic spam tactics.

Malware Deployment Details

The malicious scheme was identified by Have I Been Squatted analysts, who reported that attackers quickly compromised private keys and assets across multiple cryptocurrency chains. The malware also exposed passwords, browser sessions, and cloud tokens. The fake assessment used a Google Apps Script to gather device and browser wallet data, then misled the victim into downloading a supposed Google API helper.

Technical Insights and Prevention

The attack’s technical aspects involve a signed GapiUpdate.application package that creates a seamless illusion of a standard workspace. Once engaged, it connects to attacker servers, downloading a password-protected archive disguised as PNG files, which are actually Windows executables. The NeedleStealer malware targets browser credentials, developer tools, and more, while the Go RAT provides remote control capabilities.

To mitigate such threats, experts advise verifying recruiters through official channels and using isolated environments for handling interview-related software. Monitoring for ClickOnce activity and unexpected processes is crucial, along with updating passwords and access tokens regularly.

The broader context suggests that recruitment conversations are increasingly becoming conduits for malware distribution, with this particular campaign fitting a pattern of targeted attacks on blockchain professionals. Despite overlaps with other campaigns, analysts caution against attributing these attacks to a single entity.

Overall, this incident underscores the need for heightened vigilance in cybersecurity practices, especially within the cryptocurrency sector, where sensitive information can be quickly compromised by such sophisticated phishing strategies.

Cyber Security News Tags:ClickOnce, Cryptocurrency, cyber attack, Cybersecurity, fake interviews, hVNC RAT, Malware, NeedleStealer, Phishing, Web3

Post navigation

Previous Post: Data Breach Hits Fortune 500 Firms via Azure
Next Post: Evooo1Bot Botnet Exploits Edge Devices with DDoS Attacks

Related Posts

Malware Campaign Targets Crypto Pros with Fake LinkedIn VCs Malware Campaign Targets Crypto Pros with Fake LinkedIn VCs Cyber Security News
Windows Remote Desktop Services Vulnerability Let Attacker Deny Services Over Network Windows Remote Desktop Services Vulnerability Let Attacker Deny Services Over Network Cyber Security News
Germany Urges Apple, Google to Block Chinese AI App DeepSeek Over Privacy Rules Germany Urges Apple, Google to Block Chinese AI App DeepSeek Over Privacy Rules Cyber Security News
46,000+ Grafana Instances Exposed to Malicious Account Takeover Attacks 46,000+ Grafana Instances Exposed to Malicious Account Takeover Attacks Cyber Security News
ADT Faces Data Breach After ShinyHunters Claim ADT Faces Data Breach After ShinyHunters Claim Cyber Security News
UniFi OS Server Vulnerability Allows Root Access UniFi OS Server Vulnerability Allows Root Access Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Zimbra Mail Server Vulnerability Exploited by Hackers
  • Hackers Exploit Zimbra Flaw Before Official Disclosure
  • Modernizing Software Supply Chains in Finance
  • TeamViewer Urges Update Due to Critical Security Flaws
  • Armadin Secures $255 Million, Now Valued at $2.5 Billion

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Zimbra Mail Server Vulnerability Exploited by Hackers
  • Hackers Exploit Zimbra Flaw Before Official Disclosure
  • Modernizing Software Supply Chains in Finance
  • TeamViewer Urges Update Due to Critical Security Flaws
  • Armadin Secures $255 Million, Now Valued at $2.5 Billion

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark