Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Urgent GitLab Security Update Fixes Critical GraphQL Flaw

Urgent GitLab Security Update Fixes Critical GraphQL Flaw

Posted on August 18, 2026 By CWS

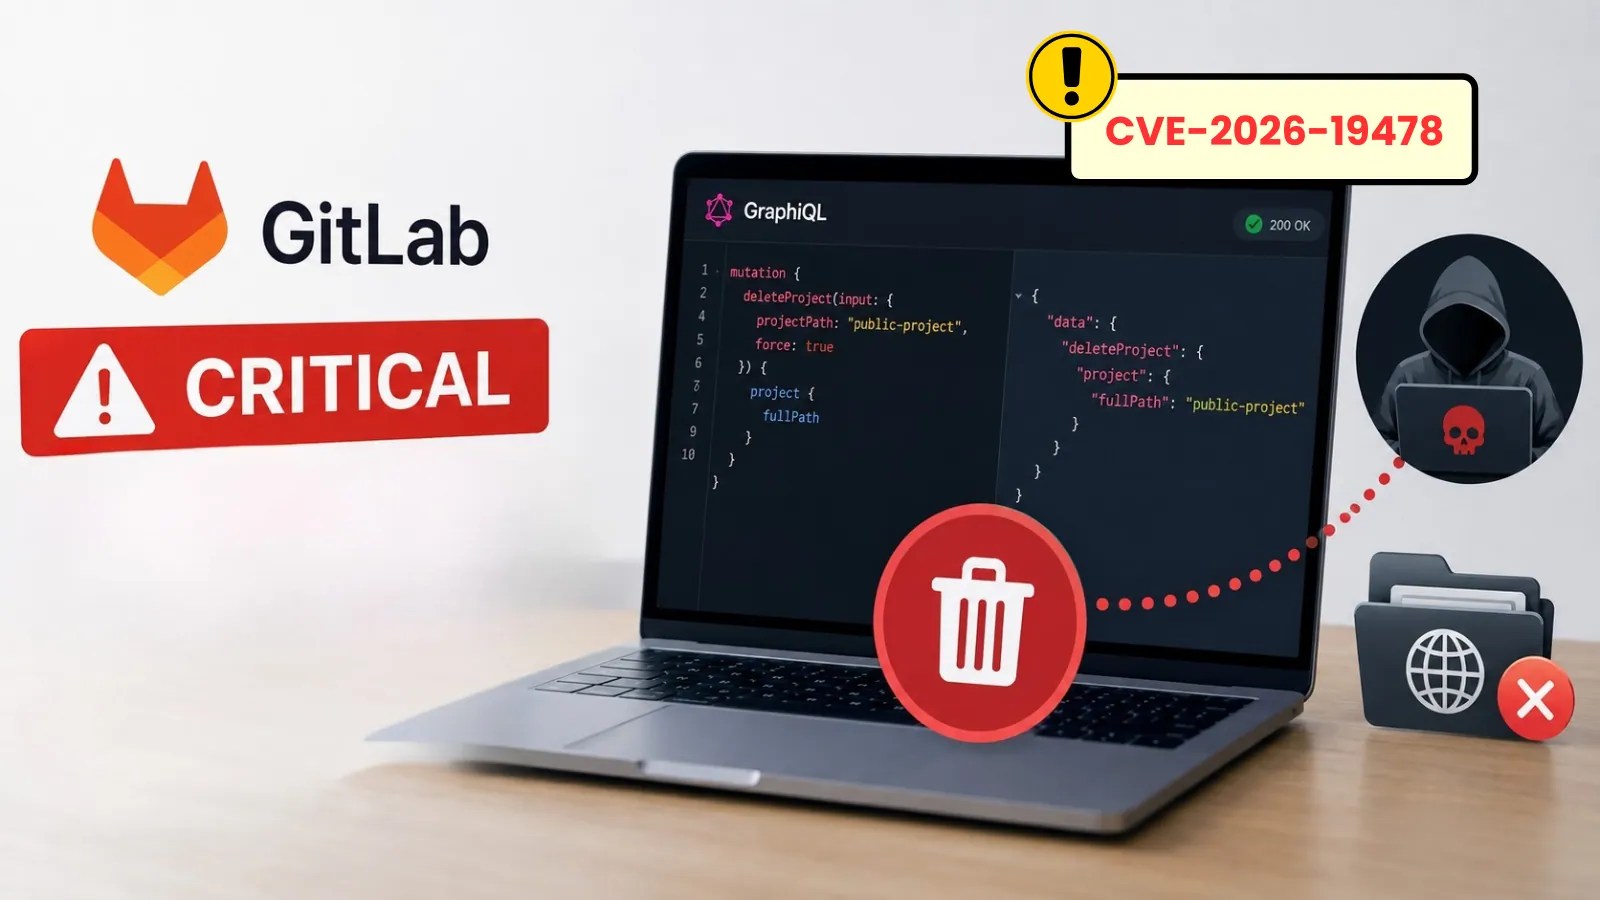
GitLab has issued an urgent security update to resolve a critical GraphQL vulnerability that enables attackers to remotely alter or delete public projects and user data without authentication.

This vulnerability, identified as CVE-2026-19478, affects both GitLab Community Edition and Enterprise Edition across several release branches. The issue was addressed in GitLab versions 19.2.4, 19.1.6, 19.0.8, and 18.11.11, released on August 17, 2026.

Understanding the GitLab Vulnerability

CVE-2026-19478 is a code injection flaw in a GraphQL directive, exploitable by unauthenticated remote attackers under specific conditions. This could result in unauthorized modifications or deletions of public GitLab resources.

The vulnerability has been assigned a CVSS score of 9.4, categorizing it as critical due to its potential to disrupt integrity and availability with minimal attack complexity and no prerequisite privileges.

Impact and Mitigation

Affected versions include all GitLab CE and EE releases from 18.2 before 18.11.11, 19.0 before 19.0.8, 19.1 before 19.1.6, and 19.2 before 19.2.4. Organizations using these versions should prioritize patching, especially if public projects are enabled.

GitLab has already implemented the fix on GitLab.com and GitLab Dedicated, requiring no further action from users. Administrators of self-managed instances are strongly advised to upgrade immediately to ensure protection.

Additional Security Concerns

The update also addresses CVE-2026-19650, a high-severity cross-site request forgery vulnerability in the GraphQL multiplex query handler, which could allow unauthorized GraphQL mutations through improperly validated GET requests. This flaw carries a CVSS score of 7.1.

Security teams are encouraged to upgrade to the latest GitLab versions to mitigate these vulnerabilities. No new database migrations are needed, and multi-node deployments should not require significant downtime.

Regularly reviewing GitLab audit logs for unusual activities, such as unexpected changes to public repositories or suspicious GraphQL actions, is recommended to ensure security. Internet-facing instances should be prioritized due to the remote exploitability of the vulnerability.

This incident underscores the importance of timely updates in maintaining the security and integrity of software development environments.
Cyber Security News Tags:CVE-2026-19478, Cybersecurity, data protection, enterprise software, GitLab, GraphQL, patch management, security update, software development, Vulnerability

Post navigation

Previous Post: GhostJacking AI Attacks and New Cyber Threats Unveiled
Next Post: SafePal Data Breach Exposes 40,000 Customer Records

Related Posts

Hackers Using CastleRAT Malware to Attack Windows Systems and Gain Remote Access Hackers Using CastleRAT Malware to Attack Windows Systems and Gain Remote Access Cyber Security News
Hackers Breaking Internet with 7.3 Tbps and 4.8 Billion Packets Per Second DDoS Attack Hackers Breaking Internet with 7.3 Tbps and 4.8 Billion Packets Per Second DDoS Attack Cyber Security News
8 New Malicious Firefox Extensions Steal OAuth Tokens, Passwords, and Spy on Users 8 New Malicious Firefox Extensions Steal OAuth Tokens, Passwords, and Spy on Users Cyber Security News
New Tactics by AMOS Malware Target Apple Users New Tactics by AMOS Malware Target Apple Users Cyber Security News
Cybersecurity News Weekly Newsletter – 29.7 Tbps DDoS Attack, Chrome 143, React2Shell Vulnerabilities and Cloudflare Outage Cybersecurity News Weekly Newsletter – 29.7 Tbps DDoS Attack, Chrome 143, React2Shell Vulnerabilities and Cloudflare Outage Cyber Security News
ModHeader Chrome Extension Pulled for Data Exfiltration Risk ModHeader Chrome Extension Pulled for Data Exfiltration Risk Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Retadup Worm Resurfaces with CoffeeLoader Malware
  • U.S. Imposes New Limits on China’s AI Chip Access
  • AI-Driven Marketplace Threatens Corporate Security
  • Top Patch Management Solutions for 2026
  • VS Code Extension Security Flaw Exposes Files Outside Workspaces

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Retadup Worm Resurfaces with CoffeeLoader Malware
  • U.S. Imposes New Limits on China’s AI Chip Access
  • AI-Driven Marketplace Threatens Corporate Security
  • Top Patch Management Solutions for 2026
  • VS Code Extension Security Flaw Exposes Files Outside Workspaces

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark