Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Hackers Exploit MFA to Hijack Microsoft 365 Sessions

Hackers Exploit MFA to Hijack Microsoft 365 Sessions

Posted on August 19, 2026 By CWS

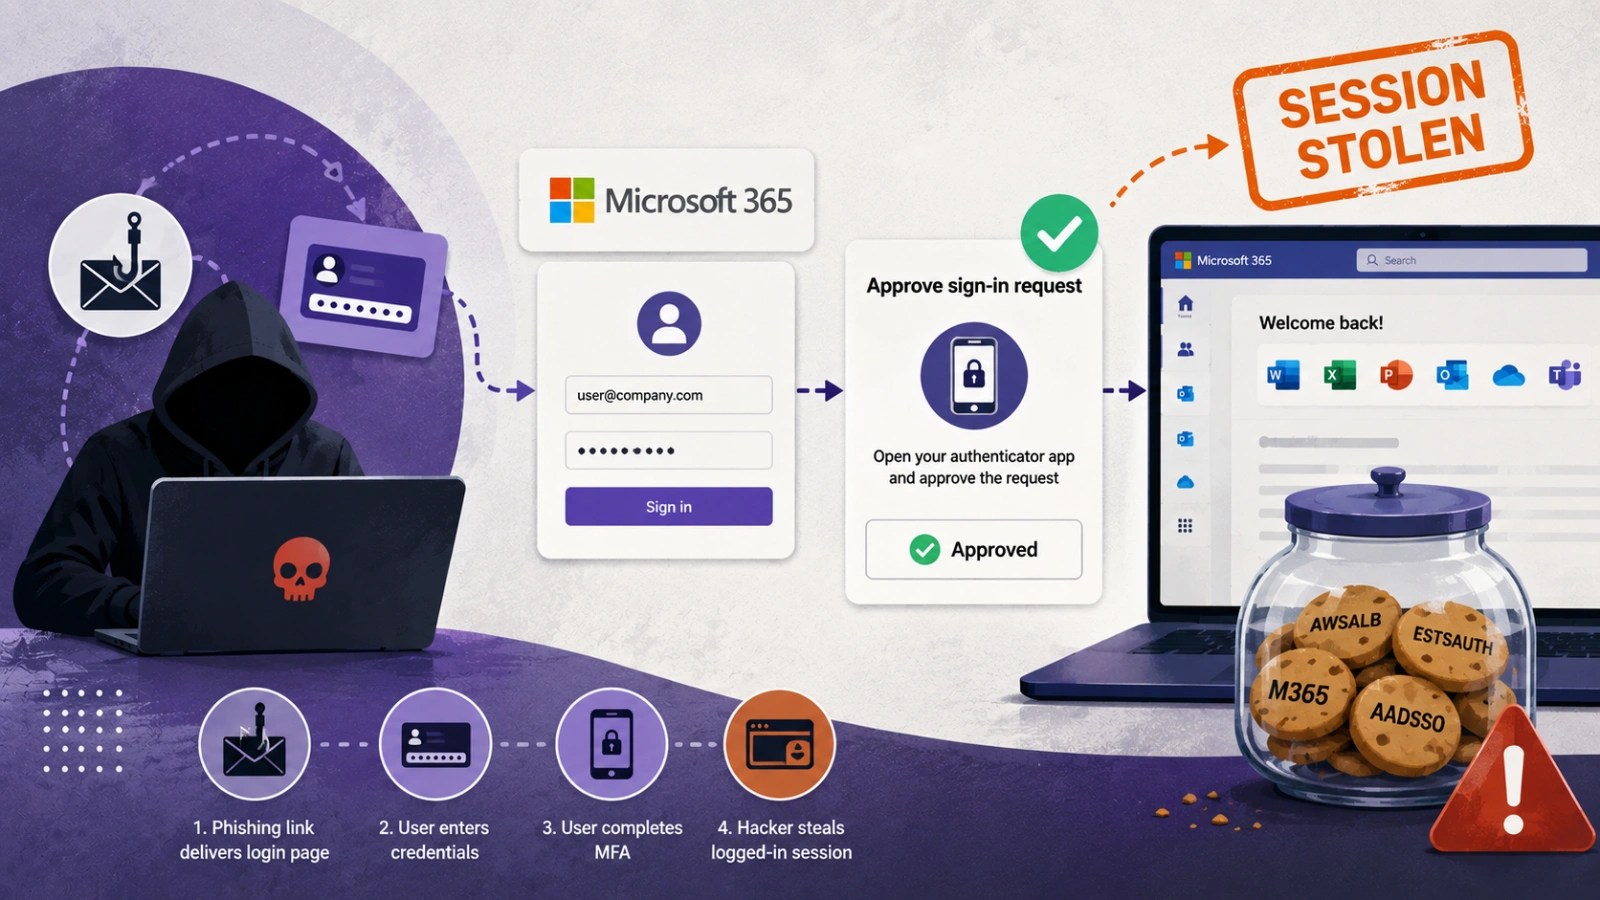
A new Phishing-as-a-Service platform called Mirage2FA is providing cybercriminals with the ability to bypass multi-factor authentication (MFA) in Microsoft 365 accounts. This sophisticated tool allows attackers to intercept authenticated sessions after users complete their login process, posing significant threats to enterprise security.

How Mirage2FA Compromises Security

Security researchers from ANY.RUN have uncovered how the Adversary-in-the-Middle (AiTM) framework employed by Mirage2FA leads to massive session cookie theft rather than merely targeting passwords. This method has been in effect since late 2024, resulting in a substantial number of compromised accounts.

The tool operates by positioning itself between users and legitimate authentication endpoints. When users enter their credentials and one-time passcodes into a fake login portal, the data is immediately relayed to the actual Microsoft 365 service. Once authentication is confirmed, the tool intercepts the session tokens, allowing unauthorized access.

Impact and Reach of Session Hijacking

Armed with intercepted session cookies, attackers can access various Microsoft 365 services without triggering additional authentication prompts. The group behind this operation, identified as LinX Coders, uses particular configurations and telemetry channels to manage the stolen sessions.

ANY.RUN’s analysis shows a vast exposure across enterprises, affecting 3,518 email domains and 9,426 accounts, with the United States being the most impacted. The campaign also hit countries like India, Singapore, and the UK, with the technology sector being the primary target.

Mitigation and Future Outlook

The infection chain operates entirely in the browser, often using obfuscated HTML and SVG attachments in phishing emails. Security experts stress the importance of focusing on structural attack patterns rather than domain names. Immediate actions include invalidating active sessions, revisiting OAuth permissions, and implementing hardware security solutions like FIDO2 keys.

Organizations must remain vigilant and proactive in addressing these threats. Traditional password resets are inadequate; comprehensive strategies must be adopted to ensure session security and prevent unauthorized access.

As the cybercrime landscape evolves, integrating advanced threat detection and investigation tools, such as ANY.RUN, is crucial for strengthening security operations centers (SOCs) and combating phishing campaigns effectively.

Cyber Security News Tags:ANY.RUN, Cybercrime, Cybersecurity, enterprise security, LinX Coders, MFA breach, Microsoft 365, Mirage2FA, phishing-as-a-service, session cookies, session hijacking, technology sector

Post navigation

Previous Post: Spectre Attack on Cloudflare Workers Leaks JWT
Next Post: OpenAI Enhances AI Security Amid Training Pause

Related Posts

Yoma Fleet Enhances Cybersecurity with AccuKnox SIEM Yoma Fleet Enhances Cybersecurity with AccuKnox SIEM Cyber Security News
Noodle RAT Targets Windows and Linux: A Growing Cyber Threat Noodle RAT Targets Windows and Linux: A Growing Cyber Threat Cyber Security News
NX Build Tool Hacked with Malware That Checks for Claude or Gemini to Find Wallets and Secrets NX Build Tool Hacked with Malware That Checks for Claude or Gemini to Find Wallets and Secrets Cyber Security News
IBM Patches Critical FTM Vulnerabilities Affecting Payment Systems IBM Patches Critical FTM Vulnerabilities Affecting Payment Systems Cyber Security News
Malware Targets Windows via Deceptive npm Package Malware Targets Windows via Deceptive npm Package Cyber Security News
Cybersecurity News Weekly Newsletter – Windows, Chrome, and Apple 0-days, Kali Linux 2025.4, and MITRE Top 25 Cybersecurity News Weekly Newsletter – Windows, Chrome, and Apple 0-days, Kali Linux 2025.4, and MITRE Top 25 Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Armornet Launches AI Security for Software Supply Chains
  • Critical NGINX HTTP/2 Vulnerability Allows Remote Code Execution
  • SpyCloud Predicts 2027 Cyber Threats: AI and Trusted Access Risks
  • 2027 Cybersecurity Awards: New AI Categories Announced
  • Malicious Agent Framework Releases Threaten Credentials

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Armornet Launches AI Security for Software Supply Chains
  • Critical NGINX HTTP/2 Vulnerability Allows Remote Code Execution
  • SpyCloud Predicts 2027 Cyber Threats: AI and Trusted Access Risks
  • 2027 Cybersecurity Awards: New AI Categories Announced
  • Malicious Agent Framework Releases Threaten Credentials

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark