Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Noodle RAT Targets Windows and Linux: A Growing Cyber Threat

Noodle RAT Targets Windows and Linux: A Growing Cyber Threat

Posted on September 16, 2026 By CWS

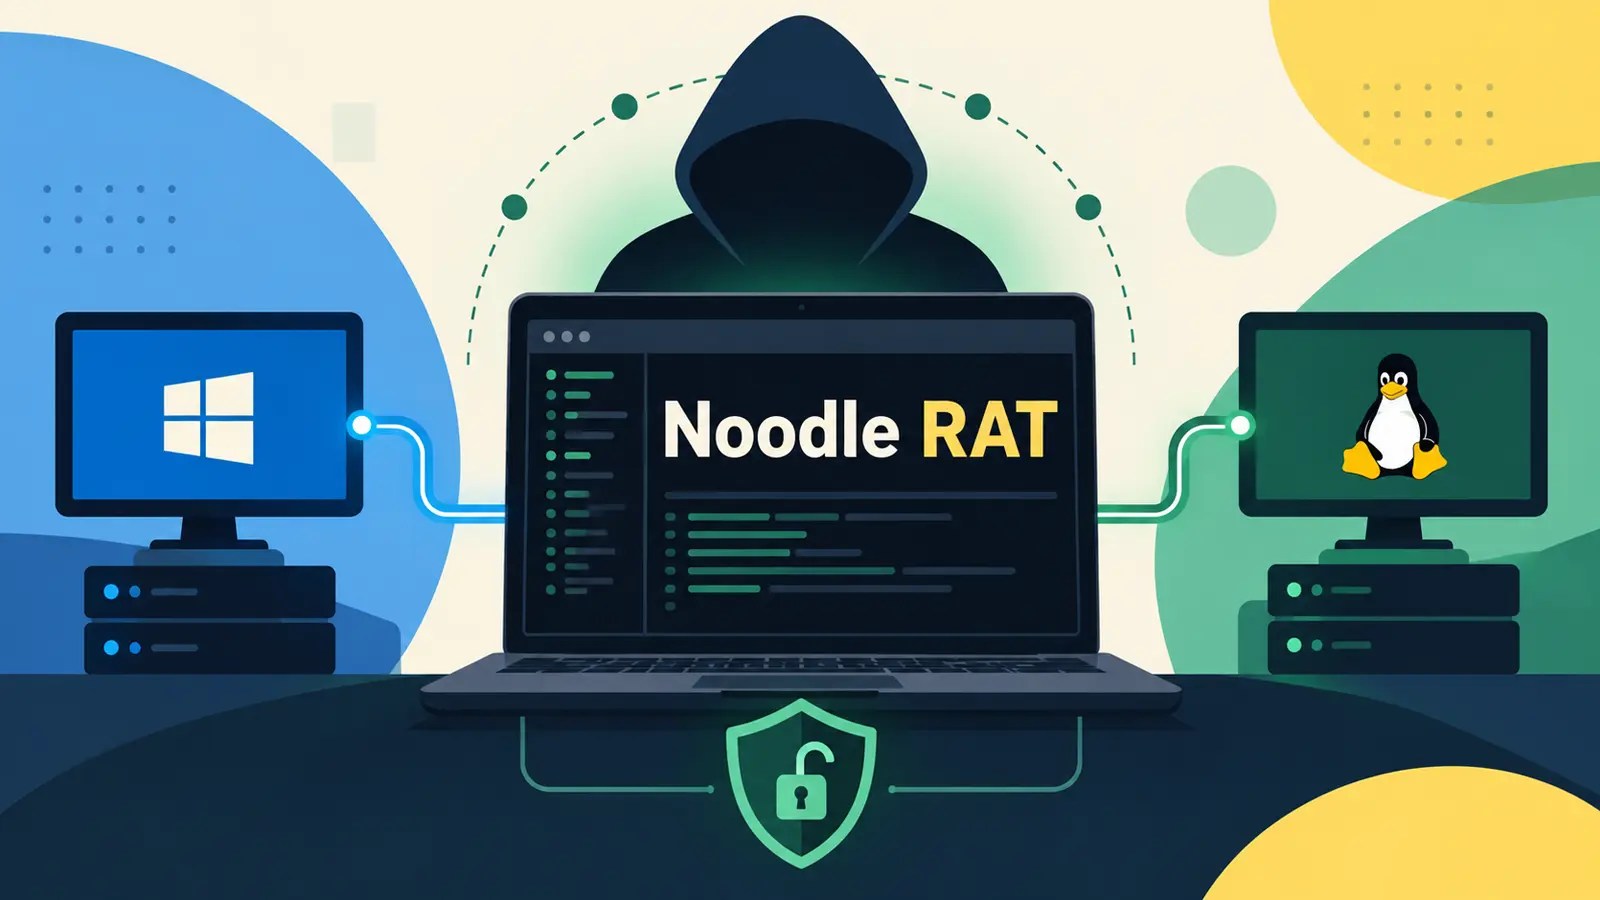
The emergence of Noodle RAT as a significant cyber threat is causing concern among cybersecurity experts. This remote-access trojan (RAT) grants attackers control over compromised systems, targeting both Windows and Linux environments. Its ability to operate cross-platform has increased its reach across corporate networks, making it a formidable tool for cybercriminals.

Impact Across Asia-Pacific

Noodle RAT has been observed in attacks on organizations throughout the Asia-Pacific region, including countries such as Thailand, India, Japan, Malaysia, and Taiwan. Hackers use this malware to steal files, execute commands, and reroute traffic through victim systems, transforming initial breaches into larger network threats.

According to Check Point analysts, Noodle RAT is a distinct malware family and not merely a variant of Gh0st RAT or Rekoobe. Known as ANGRYREBEL and Nood RAT, it has been associated with Chinese-speaking threat actors since mid-2016. This association suggests its deployment by both state-aligned groups and financially motivated criminals.

Technical Functionality and Encryption

Noodle RAT utilizes different techniques across operating systems but maintains a unified command-and-control structure. On Windows, it functions as a modular backdoor, executing in memory via shellcode, with loaders like MULTIDROP and MICROLOAD facilitating its stealth. Capable of uploading and downloading files, it acts as a TCP proxy, and can self-delete to avoid detection.

Conversely, on Linux, Noodle RAT emphasizes server-side access, enabling attackers to open reverse shells, manage files, and create SOCKS tunnels. These actions often follow exploitation or web-shell deployment on exposed servers. Both variants employ sophisticated encryption methods—RC4, XOR, and custom encryption on Windows, and HMAC-SHA1 and AES-128-CBC on Linux—making detection more challenging.

Defensive Strategies and Recommendations

The widespread deployment of Noodle RAT by groups like Iron Tiger and Calypso APT highlights its appeal as a versatile tool in cyber attacks. Organizations are encouraged to patch exposed services promptly, enforce multifactor authentication, and monitor for unusual outbound connections to mitigate risks.

Security teams must also focus on correlating suspicious activities, such as abnormal proxy behavior or task scheduling, to identify potential Noodle RAT infections. Maintaining robust backups and segregating critical servers from user networks are essential steps in minimizing the impact of a compromise.

Ultimately, the Noodle RAT threat underlines the importance of consistent visibility across mixed operating systems. By analyzing endpoint and server telemetry alongside indicators of compromise, organizations can enhance their defensive measures and respond more swiftly to threats.

Cyber Security News Tags:APT groups, Cybersecurity, Encryption, Linux, Malware, network security, Noodle RAT, remote access trojan, Threat Actors, Windows

Post navigation

Previous Post: Virtual Summit Explores Attack Surface Management

Related Posts

Fortinet Alerts on Credential Attack Targeting FortiGate Fortinet Alerts on Credential Attack Targeting FortiGate Cyber Security News
Paperclip Security Flaws Allow Admin Access to Hackers Paperclip Security Flaws Allow Admin Access to Hackers Cyber Security News
pnpm 11 Enhances Security with Default Release Age Setting pnpm 11 Enhances Security with Default Release Age Setting Cyber Security News
Sleeping Bouncer Vulnerability Impacts Motherboards from Gigabyte, MSI, ASRock and ASUS Sleeping Bouncer Vulnerability Impacts Motherboards from Gigabyte, MSI, ASRock and ASUS Cyber Security News
Severe Fiber v2 Vulnerability in Go Risks Security Breaches Severe Fiber v2 Vulnerability in Go Risks Security Breaches Cyber Security News
KATARU IoT Malware: Linux Exploits and DDoS Tactics KATARU IoT Malware: Linux Exploits and DDoS Tactics Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Noodle RAT Targets Windows and Linux: A Growing Cyber Threat
  • Virtual Summit Explores Attack Surface Management
  • AI Coding Assistant Breach Spreads Malware Across Repositories
  • Axoflow’s AxoDetect Revolutionizes Security Data Management
  • AIUC Secures $40M to Enhance AI Agent Certification

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Noodle RAT Targets Windows and Linux: A Growing Cyber Threat
  • Virtual Summit Explores Attack Surface Management
  • AI Coding Assistant Breach Spreads Malware Across Repositories
  • Axoflow’s AxoDetect Revolutionizes Security Data Management
  • AIUC Secures $40M to Enhance AI Agent Certification

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark