Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Bimbo Bakeries Hit by Oracle EBS Data Breach

Bimbo Bakeries Hit by Oracle EBS Data Breach

Posted on September 7, 2026 By CWS

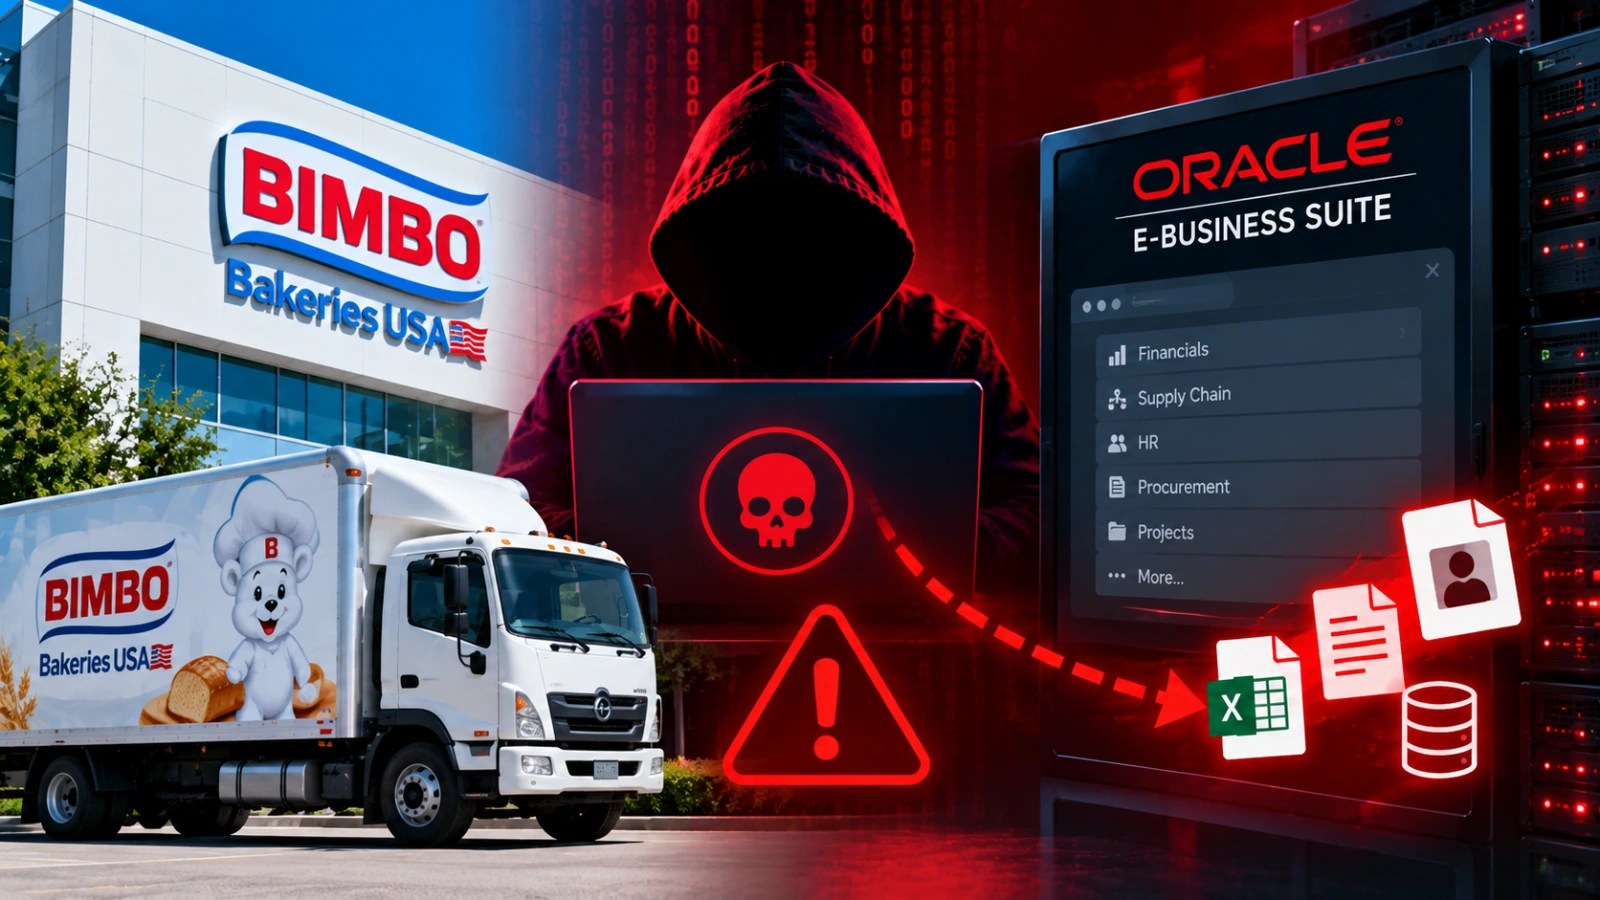
Bimbo Bakeries USA, a prominent entity in the global baking industry, has confirmed that a cyberattack led to the unauthorized access of employee data. This breach was facilitated through a zero-day vulnerability in Oracle’s E-Business Suite (EBS), putting Bimbo Bakeries among several organizations targeted by the Clop ransomware group.

Details of the Breach

On August 31, 2026, Bimbo Bakeries notified affected parties in a letter submitted to the California Attorney General. The breach is linked to a third-party vendor utilizing Oracle EBS, as noted in the official records with the Attorney General’s Office.

The bakery giant discovered on December 6, 2025, that hackers had exploited this vulnerability to access files within the platform. Immediate action was taken to apply Oracle’s emergency patches, followed by a forensic investigation to assess the data exposure.

Timeline and Vulnerability

After months of investigation, it was confirmed on August 19, 2026, that personal information, including names and Social Security numbers, was compromised. This finding initiated the formal notification process required by state laws.

While Bimbo Bakeries has not specified the exact flaw, the details align with a campaign associated with CVE-2025-61882. This critical vulnerability allowed attackers to execute code on EBS servers without credentials, rated 9.8 on the CVSS scale.

Google’s Mandiant traced the breach back to August 2025, preceding Oracle’s patch release on October 4, 2025. The Clop group exploited this flaw to steal data from several Oracle EBS users, including high-profile institutions.

Response and Recommendations

Bimbo Bakeries has not officially linked the attack to the Clop group, nor disclosed the number of individuals affected or any ransom demands received. The company is reassessing its vendor partnerships and offering affected employees a year of credit monitoring and fraud protection through Cyberscout.

Security specialists advise organizations using Oracle EBS versions 12.2.3 to 12.2.14 to ensure the October 2025 patch is implemented. They should also review logs for unusual BI Publisher activities and update credentials related to EBS integrations.

Given the sensitivity of the compromised data, affected individuals are urged to keep a close watch on their credit reports, activate fraud alerts, and be cautious of phishing attempts using the breach as a pretext.

Cyber Security News Tags:Bimbo Bakeries, Clop ransomware, credit monitoring, CVE-2025-61882, Cybersecurity, data breach, employee data, fraud assistance, Oracle EBS, Oracle patch, zero-day vulnerability

Post navigation

Previous Post: Critical Security Updates: Chrome 0-Day and More
Next Post: PEEP Exploits Chrome and Edge for Host Command Execution

Related Posts

Dark Caracal Hackers Leverage Ethereum for Malware Resilience Dark Caracal Hackers Leverage Ethereum for Malware Resilience Cyber Security News
Admin Behind LeakBase Hacker Forum Arrested in Russia Admin Behind LeakBase Hacker Forum Arrested in Russia Cyber Security News
Prompt Injection Vulnerability in GitHub Actions Hits Fortune 500 Firms Prompt Injection Vulnerability in GitHub Actions Hits Fortune 500 Firms Cyber Security News
Careto Hacker Group is Back After 10 Years of Silence with New Attack Tactics Careto Hacker Group is Back After 10 Years of Silence with New Attack Tactics Cyber Security News
Google Gemini Privacy Controls Bypassed to Access Private Meeting Data Using Calendar Invite Google Gemini Privacy Controls Bypassed to Access Private Meeting Data Using Calendar Invite Cyber Security News
Malware Targets Argentine Courts with Fake Documents Malware Targets Argentine Courts with Fake Documents Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Cisco Expressway Flaw Allows Remote Access as Root
  • LiteLLM Faces Supply Chain Breach, Compromised Packages Removed
  • Node.js Vulnerability Exploited with Brotli Data
  • Oracle Releases Critical Java Update for HTTPS Security Flaw
  • Iranian APT Group Uses US Server After Long Hiatus

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Cisco Expressway Flaw Allows Remote Access as Root
  • LiteLLM Faces Supply Chain Breach, Compromised Packages Removed
  • Node.js Vulnerability Exploited with Brotli Data
  • Oracle Releases Critical Java Update for HTTPS Security Flaw
  • Iranian APT Group Uses US Server After Long Hiatus

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark