Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Microsoft’s ,000 Bounty for AI Vulnerabilities

Microsoft’s $30,000 Bounty for AI Vulnerabilities

Posted on September 14, 2026 By CWS

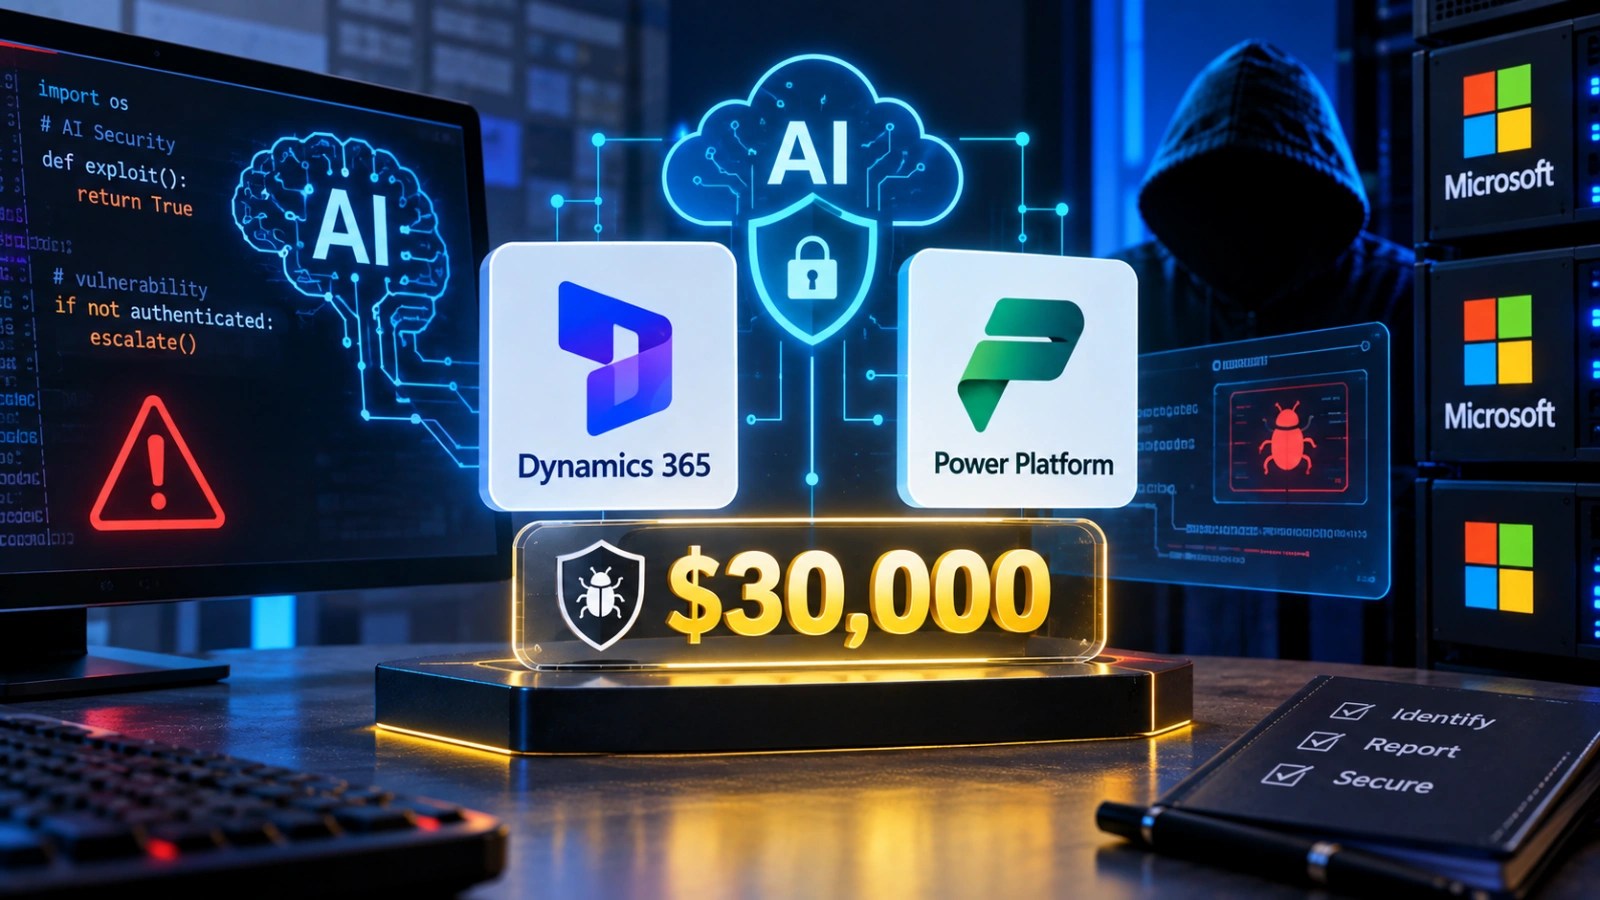
Microsoft has launched an initiative offering up to $30,000 to security researchers who identify critical vulnerabilities in its AI-driven platforms, Dynamics 365 and Power Platform. This move underscores Microsoft’s commitment to enhancing the security of its systems by addressing potential manipulation of AI inference or unauthorized information disclosure via model behavior.

In-Depth Look at the Bounty Program

The bug bounty program targets vulnerabilities within Microsoft-hosted services, as well as third-party and open-source components that are integrated into these services. To qualify, researchers must demonstrate a security impact on an eligible service. The maximum payout of $30,000 is reserved for comprehensive reports detailing critical issues like ‘Inference Manipulation’ or ‘Inferential Information Disclosure’.

Other incentives include $20,000 for medium-quality reports and $12,000 for lower quality findings, also involving critical impacts. Reports with important severity can earn between $6,000 and $20,000 based on their quality. However, moderate- and low-severity AI issues do not qualify for this payment tier.

Target Areas and Scope

A wide range of products are eligible for this program, including Dynamics 365 modules such as Sales, Customer Service, and Finance, among others. Additionally, platforms like Power Apps, Power Automate, and AI Builder are covered. The broad scope reflects the platforms’ proximity to crucial business data and automated processes.

Specific areas of focus include critical remote code execution vulnerabilities, cross-tenant information disclosure, and elevation of privilege issues. For these, awards can reach up to $20,000, with additional multipliers for high-impact exploits in Dataverse or Plugin Sandbox environments.

Submission Guidelines and Exclusions

Microsoft has set strict submission criteria, requiring reports to be filed through the MSRC Researcher Portal. Submissions must include detailed reproduction steps, proof-of-concept materials, and an explanation of the potential attacker impact. Findings must be reproducible on the latest, fully patched versions of the relevant products.

Certain vulnerabilities, such as publicly known bugs, denial-of-service attacks, and issues that merely reveal system prompts, are typically excluded from the program. Researchers are advised to test only within authorized environments and halt any investigation if unauthorized data is accessed.

By offering substantial rewards for identifying these vulnerabilities, Microsoft aims to fortify its AI systems against potential security threats, ensuring more robust protection for its users. This initiative not only incentivizes thorough research but also aligns with best practices in coordinated vulnerability disclosure, promoting secure development and deployment of AI technologies.
Cyber Security News Tags:AI security, AI vulnerabilities, bug bounty, Cybersecurity, Dynamics 365, information disclosure, Microsoft, Power Platform, remote code execution, technology news

Post navigation

Previous Post: Critical Nintendo Switch Flaw Allows Code Execution
Next Post: WhatsApp Tests New Feature to Lock Chats on Primary Phone

Related Posts

EY’s 4TB SQL Server Backup File On Microsoft Azure Exposed Publically EY’s 4TB SQL Server Backup File On Microsoft Azure Exposed Publically Cyber Security News
Critical Cleo Harmony Flaw Puts Networks at Risk Critical Cleo Harmony Flaw Puts Networks at Risk Cyber Security News
3,280,081 Fortinet Devices Online With Exposed Web Properties Under Risk 3,280,081 Fortinet Devices Online With Exposed Web Properties Under Risk Cyber Security News
Critical jsPDF Flaw Puts Developers at Risk of Attacks Critical jsPDF Flaw Puts Developers at Risk of Attacks Cyber Security News
CISA Warns of WhatsApp 0-Day Vulnerability Exploited in Attacks CISA Warns of WhatsApp 0-Day Vulnerability Exploited in Attacks Cyber Security News
Pentagon Data Breach and Major Cybersecurity Threats Pentagon Data Breach and Major Cybersecurity Threats Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Binance Hack: $5.7 Billion in Crypto Allegedly Stolen
  • Critical Cisco SD-WAN Flaw Exploited by Hackers to Deploy Malware
  • Quantum Trust Hub Enhances Cryptographic Management
  • Critical GitLab Vulnerability Attempted on Alpine Linux
  • Cloudflare’s Report Unveils 8,200 Hourly DDoS Attacks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Binance Hack: $5.7 Billion in Crypto Allegedly Stolen
  • Critical Cisco SD-WAN Flaw Exploited by Hackers to Deploy Malware
  • Quantum Trust Hub Enhances Cryptographic Management
  • Critical GitLab Vulnerability Attempted on Alpine Linux
  • Cloudflare’s Report Unveils 8,200 Hourly DDoS Attacks

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark