Cyclops Blink Returns with Enhanced Capabilities
The notorious Cyclops Blink malware is back with advanced features that allow cyber attackers to gain a comprehensive view of corporate networks. Recently detected on compromised Cisco Firewall Management Center devices, this malware facilitates remote access, traffic inspection, and mapping of internal systems.
The presence of Cyclops Blink on management appliances is particularly alarming due to their trusted network positions. Breaches at this level can expose critical configurations, credentials, and pathways to otherwise secure systems, highlighting the significant risk posed by such intrusions.
Identifying the Threat
In August, Sophos researchers uncovered the latest Cyclops Blink implant while analyzing a malicious 64-bit Linux executable on compromised devices. The analysis linked this malware to the Sandworm group associated with Russia, though attribution for recent deployments remains cautious.
The initial access point for the malware remains undetermined. However, the affected environments have faced significant web-management vulnerabilities, including the exploitation of embedded credentials that allowed unauthorized access, potentially compounding security risks.
Evolution of Cyclops Blink Malware
The updated Cyclops Blink sample is now a 64-bit x86-64 Linux executable, moving away from its previous PowerPC version found on WatchGuard devices. This new version leverages standard SysV startup services, enhancing its persistence across various Linux systems.
With elevated privileges, the implant relocates to a system directory, registering a startup script for automatic execution post-reboot. It disguises its controller as a regular Linux worker process, minimizing detection risk in process listings.
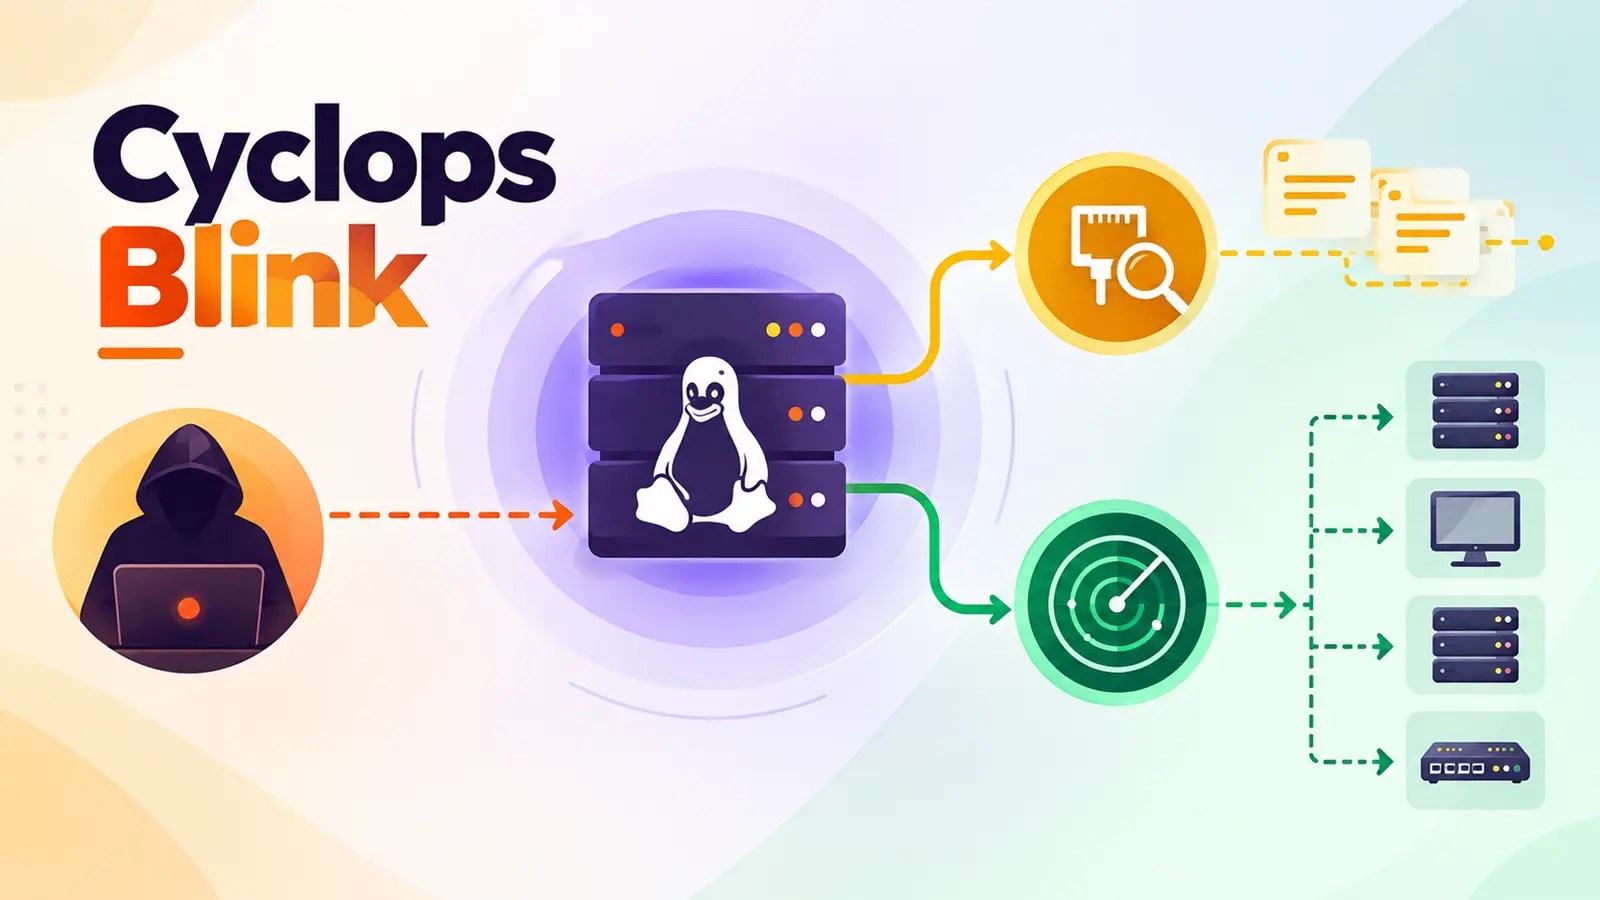
The malware operates through five child-process modules, each handling tasks like reconnaissance, file transfer, scanning, packet collection, and maintaining persistence, all managed by a parent controller.
Implications for Network Security
Cyclops Blink profiles host systems and their nearby networks, gathering data on operating systems, accounts, processes, storage, and more. When permissions allow, it can extract password hashes and exfiltrate accessible files, enhancing its threat to network management platforms.
Its command-and-control mechanism uses outbound TLS connections with a custom protocol, complicating network defense and incident response. Timing changes and destination tracking are crucial for effective mitigation.
The malware’s internal scanner identifies local IPv4 networks, testing ports related to administration, file sharing, and more. This functionality transforms infected devices into reconnaissance tools, aiding attackers in selecting subsequent targets.
Organizations must extend threat hunting beyond known affected devices, scrutinizing compatible Linux appliances for signs of compromise. Prompt security updates, restricted management access, and vigilant monitoring of encrypted connections are essential defensive measures.
For further protection, ensure your SOC is updated within 24 hours of malware emergence, utilizing platforms like ANYRUN for early detection.