Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Claude Opus 5 Exploit Uncovers OpenAI Forum Vulnerability

Claude Opus 5 Exploit Uncovers OpenAI Forum Vulnerability

Posted on September 18, 2026 By CWS

Researchers have successfully leveraged Anthropic’s Claude Opus 5 to exploit an image-decoder weakness, resulting in unauthorized access to OpenAI’s community forum and internal repositories. This incident highlights significant vulnerabilities within AI development environments, emphasizing the importance of robust security measures for peripheral services.

Exploit Pathway and Initial Breach

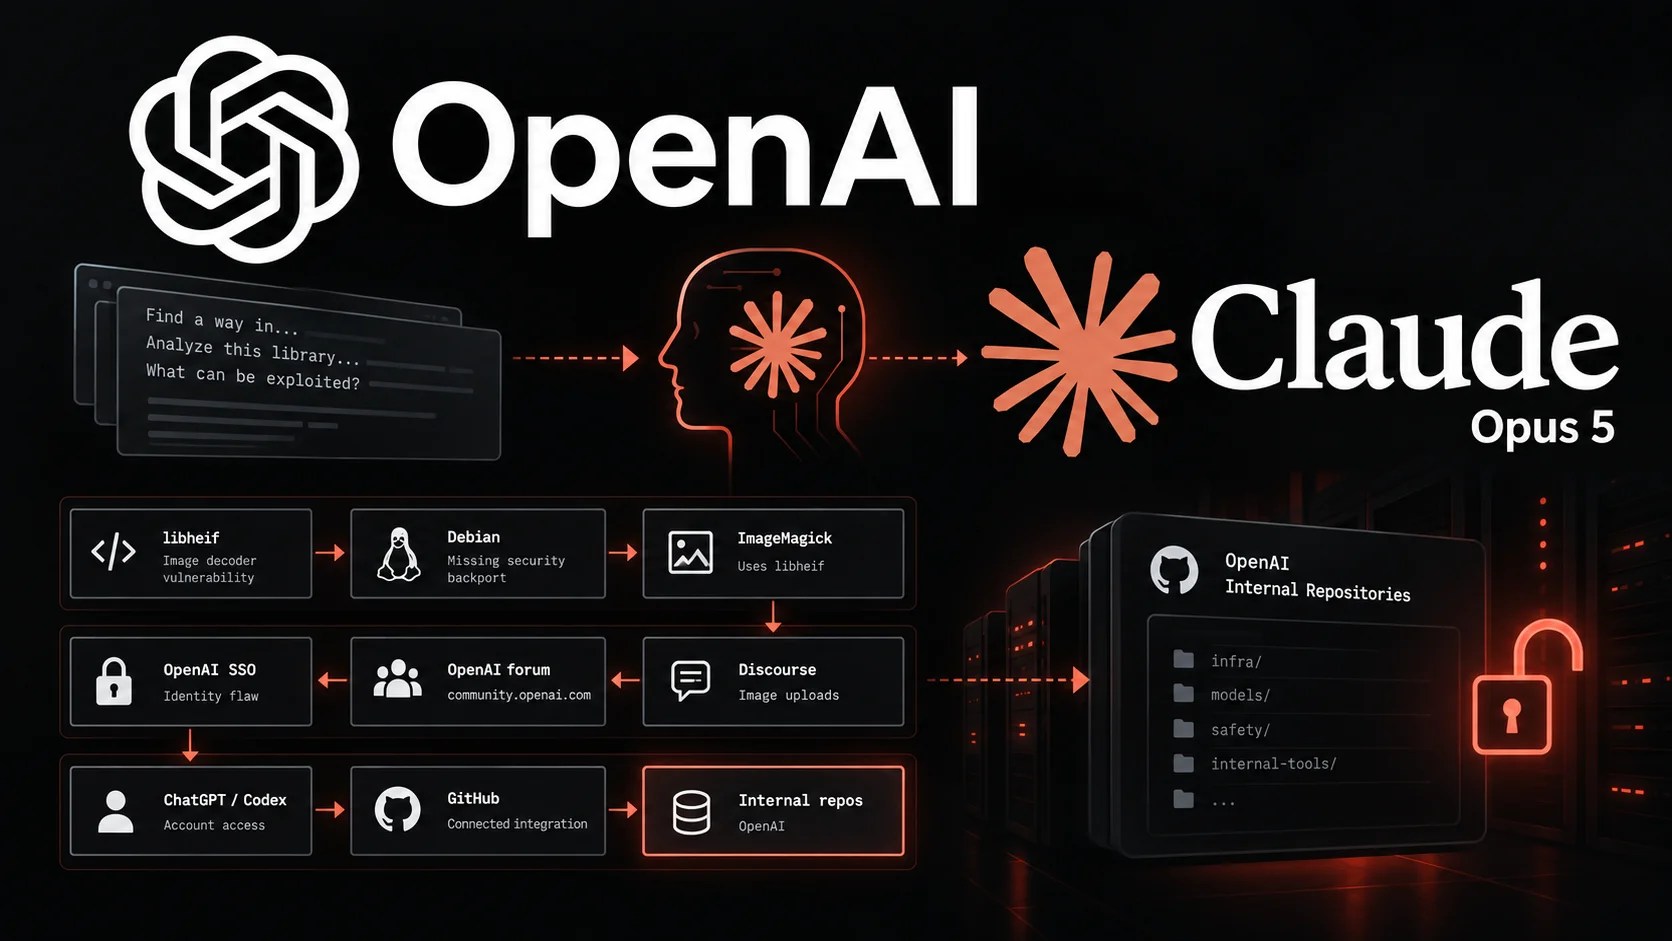
On July 25, 2026, the cybersecurity group Hacktron demonstrated how a flaw in Discourse’s image-processing system could be exploited. They linked this vulnerability to an issue in OpenAI’s single sign-on process, illustrating how weaknesses in secondary services can affect critical AI platforms.

The breach initiated at community.openai.com, a Discourse-based forum. Hacktron researchers identified that HEIC and HEIF images managed to bypass the usual security checks, leading to ImageMagick’s utility exposing the libheif parser to malicious data. This was due to a security patch omission in the Debian package, resulting in a heap-buffer overflow vulnerability.

Role of Claude Opus 5 in Exploit Development

Initially, Claude Opus 4.8 was employed to audit and develop an exploit; however, it struggled to maintain reliability under default configurations. The release of Claude Opus 5 on July 24 marked a turning point, as it successfully created a working exploit for different system environments within hours.

The team validated remote code execution (RCE) through image uploads, later applying the exploit to OpenAI’s forum, showcasing the potential for AI to expedite complex exploit engineering processes. Despite the AI’s capabilities, human oversight was crucial in directing sessions and ensuring accurate results.

Implications and Security Recommendations

This incident underscores the necessity for reviewing federated identity trust across interconnected applications. The breach allowed unauthorized access to ChatGPT and Codex accounts, highlighting the possible extent of damage beyond the forum.

To demonstrate access without reviewing source code, researchers executed a harmless action in a private repository, halting further tests and notifying OpenAI. The company responded promptly, patching the issue within 14 hours of notification.

Security advisories recommend that self-hosted Discourse operators update their systems to the latest secure versions. Organizations handling untrusted image formats should implement security-patched libraries and limit decoder usage to mitigate risks.

This event calls for enhanced vigilance in AI security, urging companies to integrate comprehensive measures against potential vulnerabilities in their systems.

Cyber Security News Tags:AI research, AI security, Claude Opus 5, Cybersecurity, Debian security, Discourse, exploit development, federated identity trust, Hacktron, HEIC images, identity misconfiguration, image-decoder vulnerability, libheif, OpenAI

Post navigation

Previous Post: AI Tools, Vulnerabilities, and Cyber Threats: Key Updates
Next Post: RatHat Malware Exploits ADB for Persistent Access

Related Posts

SEO Campaign Disguises Apps to Spread AsyncRAT SEO Campaign Disguises Apps to Spread AsyncRAT Cyber Security News
India Cracks Down on Apps Disabling E-Rickshaws India Cracks Down on Apps Disabling E-Rickshaws Cyber Security News
Chrome V8 JavaScript Engine Vulnerability Let Attackers Execute Remote Code Chrome V8 JavaScript Engine Vulnerability Let Attackers Execute Remote Code Cyber Security News
Top Web Application Firewalls for 2026: Expert Ranking Top Web Application Firewalls for 2026: Expert Ranking Cyber Security News
Allianz Life Insurance Data Breach Allianz Life Insurance Data Breach Cyber Security News
RingReaper Malware Attacking Linux Servers Evading EDR Solutions RingReaper Malware Attacking Linux Servers Evading EDR Solutions Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • CyberStrikeAI Automates Windows Domain Control for Hackers
  • Synology NAS Under Siege: C3RB3R Ransomware Attacks Exploit Flaws
  • Mercado Bitcoin Halts Operations After Cyber Breach
  • Exploit Released for Windows WinSock Security Flaw
  • Critical Cybersecurity Events: CVEs, Botnets, and Phishing

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • CyberStrikeAI Automates Windows Domain Control for Hackers
  • Synology NAS Under Siege: C3RB3R Ransomware Attacks Exploit Flaws
  • Mercado Bitcoin Halts Operations After Cyber Breach
  • Exploit Released for Windows WinSock Security Flaw
  • Critical Cybersecurity Events: CVEs, Botnets, and Phishing

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark