Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Brevo Attack Compromises Over 100,000 WordPress Sites

Brevo Attack Compromises Over 100,000 WordPress Sites

Posted on September 18, 2026 By CWS

A significant security breach occurred when a supply-chain attack involving Brevo transformed widely used web tools into vectors for malware distribution. The attackers embedded harmful JavaScript into services accessed by customer websites, potentially compromising both visitors and WordPress site administrators.

Widespread Impact Across Websites

The breach affected over 100,000 sites as of September 14. Users accessing impacted sites, including chat features, sign-up forms, or email unsubscribe pages, faced deceptive prompts urging them to run a command.

Researchers from Sansec uncovered this two-pronged operation by examining modified scripts across Brevo’s services and customer applications. The first approach targeted logged-in WordPress administrators, while the second used a ClickFix overlay on general site visitors.

Sansec’s report to Cyber Security News emphasized the rapid proliferation risk when a shared web component is compromised. The attack demonstrated how breaching a single service can swiftly affect a vast audience.

Details of the Brevo Supply Chain Attack

The offending code was distributed between 16:05 and 20:12 UTC on September 14, appearing on Brevo pages and in JavaScript utilized by website trackers and chat widgets. This posed risks wherever these components were integrated.

For WordPress administrators already logged in, the script attempted to install a plugin during their session. Though the plugin was not recovered, it is suspected to be a backdoor, a known threat with certain WordPress plugins offering covert access.

For other users, the script presented a full-page ClickFix prompt, masquerading as a human verification step. This trick placed a command on the clipboard, prompting users to execute it, thus turning a familiar web interaction into malware execution without exploiting browser vulnerabilities.

Response and Preventive Measures

The malicious hosts ceased operation on September 15, and the original code was reported clean. However, cached copies and compromised sites remain a concern, underscoring the need for vigilance.

Sansec’s findings suggest a second-stage event affecting shared infrastructure, highlighting that even sites without stolen credentials could be impacted by attacks on hosted assets. This incident underscores the importance of monitoring third-party scripts and limiting administrative access.

Site owners using the affected tools should inspect server logs for unauthorized WordPress uploads or activations from September 14. Visitors who executed the fake verification command should conduct comprehensive antivirus scans and report any unusual activity.

To mitigate future risks, security teams should preserve relevant logs, reset privileged accounts if necessary, and remain alert for unfamiliar changes. Monitoring third-party JavaScript can help prevent a single supplier compromise from escalating into a widespread site breach.

The evidence indicates potential access to Brevo’s Cloudflare environment, enabling DNS changes and altered responses across domains. Though not confirmed as the root cause, this highlights the critical need for stringent monitoring and rapid response capabilities post-incident.
Cyber Security News Tags:Brevo, ClickFix, Cloudflare, cyber attack, Cybersecurity, DNS changes, JavaScript, Malware, plugin backdoor, Sansec, security breach, supply chain attack, third-party scripts, website security, WordPress

Post navigation

Previous Post: Gyazo Data Breach Exposes 23 Million User Records
Next Post: Security Flaw Exposes OpenAI Code via AI-Generated Exploit

Related Posts

5 Must-Follow Rules of Every Elite SOC: CISO’s Checklist 5 Must-Follow Rules of Every Elite SOC: CISO’s Checklist Cyber Security News
Analog Devices Reports Cyber Intrusion and Data Breach Analog Devices Reports Cyber Intrusion and Data Breach Cyber Security News
Multiple Gitlab Security Vulnerabilities Let Attackers Trigger DoS Condition Multiple Gitlab Security Vulnerabilities Let Attackers Trigger DoS Condition Cyber Security News
30 Wind and Solar Farms in Poland Faced Coordinated Cyberattacks 30 Wind and Solar Farms in Poland Faced Coordinated Cyberattacks Cyber Security News
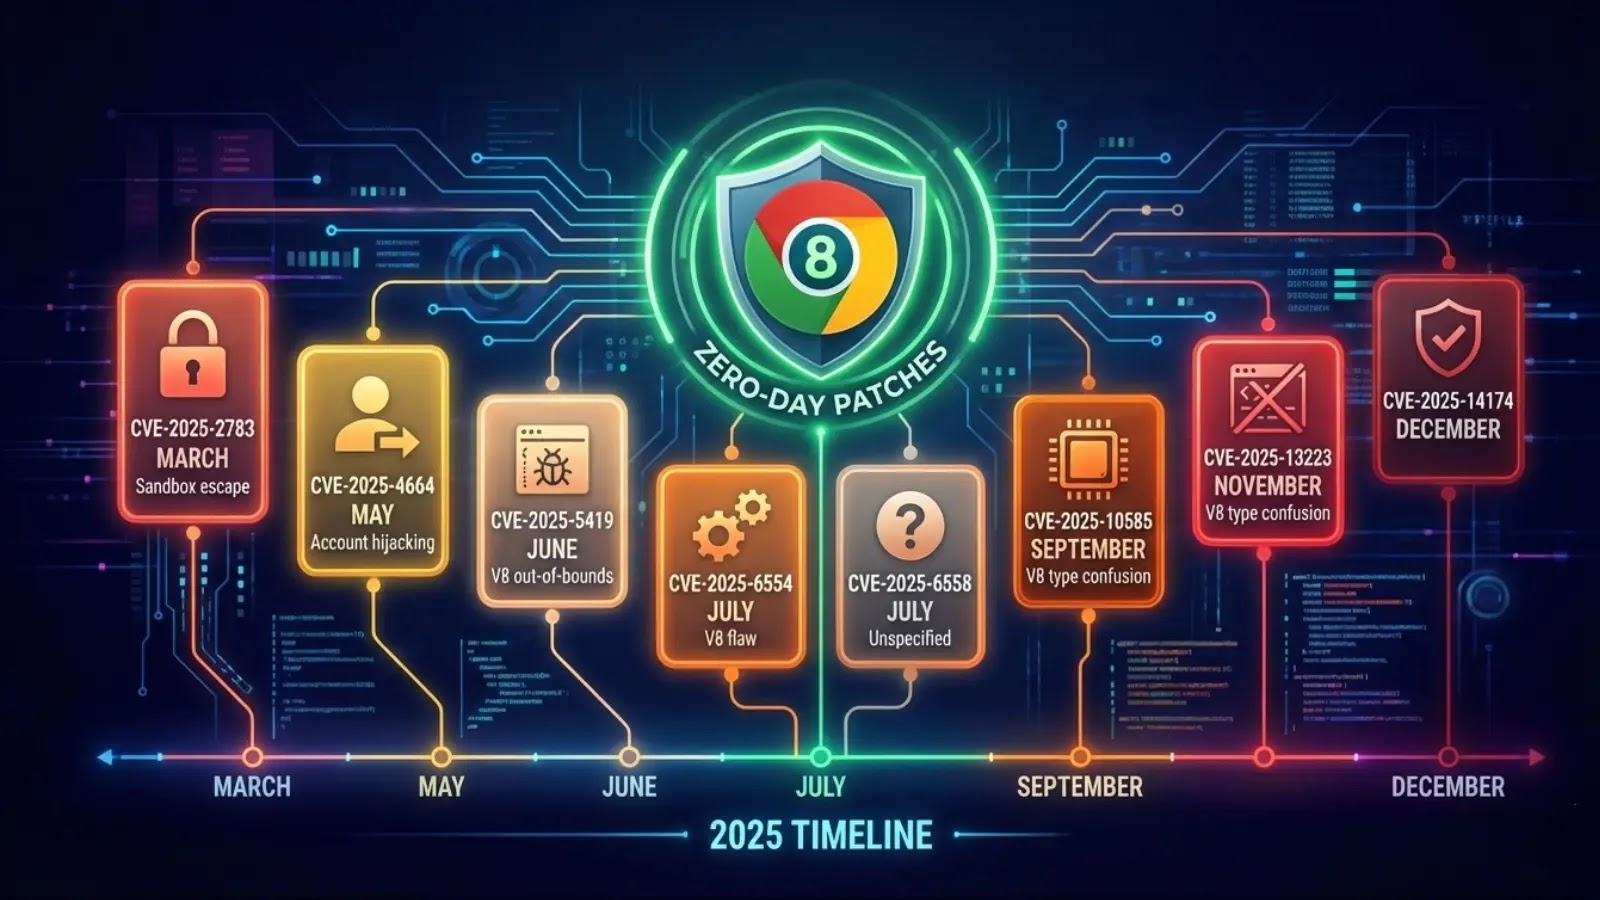
Chrome Zero-Day Vulnerabilities Exploited in 2025 Chrome Zero-Day Vulnerabilities Exploited in 2025 Cyber Security News
Lightship Security and OpenSSL Submit Version 3.5.4 for FIPS 140-3 Validation Lightship Security and OpenSSL Submit Version 3.5.4 for FIPS 140-3 Validation Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • CyberStrikeAI Automates Windows Domain Control for Hackers
  • Synology NAS Under Siege: C3RB3R Ransomware Attacks Exploit Flaws
  • Mercado Bitcoin Halts Operations After Cyber Breach
  • Exploit Released for Windows WinSock Security Flaw
  • Critical Cybersecurity Events: CVEs, Botnets, and Phishing

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • CyberStrikeAI Automates Windows Domain Control for Hackers
  • Synology NAS Under Siege: C3RB3R Ransomware Attacks Exploit Flaws
  • Mercado Bitcoin Halts Operations After Cyber Breach
  • Exploit Released for Windows WinSock Security Flaw
  • Critical Cybersecurity Events: CVEs, Botnets, and Phishing

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark