Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Linux Kernel Vulnerabilities Pose Root Access Risks

Linux Kernel Vulnerabilities Pose Root Access Risks

Posted on September 18, 2026 By CWS

Four vulnerabilities recently identified in the Linux kernel expose systems to potential privilege escalation and root access risks. These flaws, affecting longstanding networking components, have been patched by developers, but they highlight significant security concerns.

Details of the Vulnerabilities

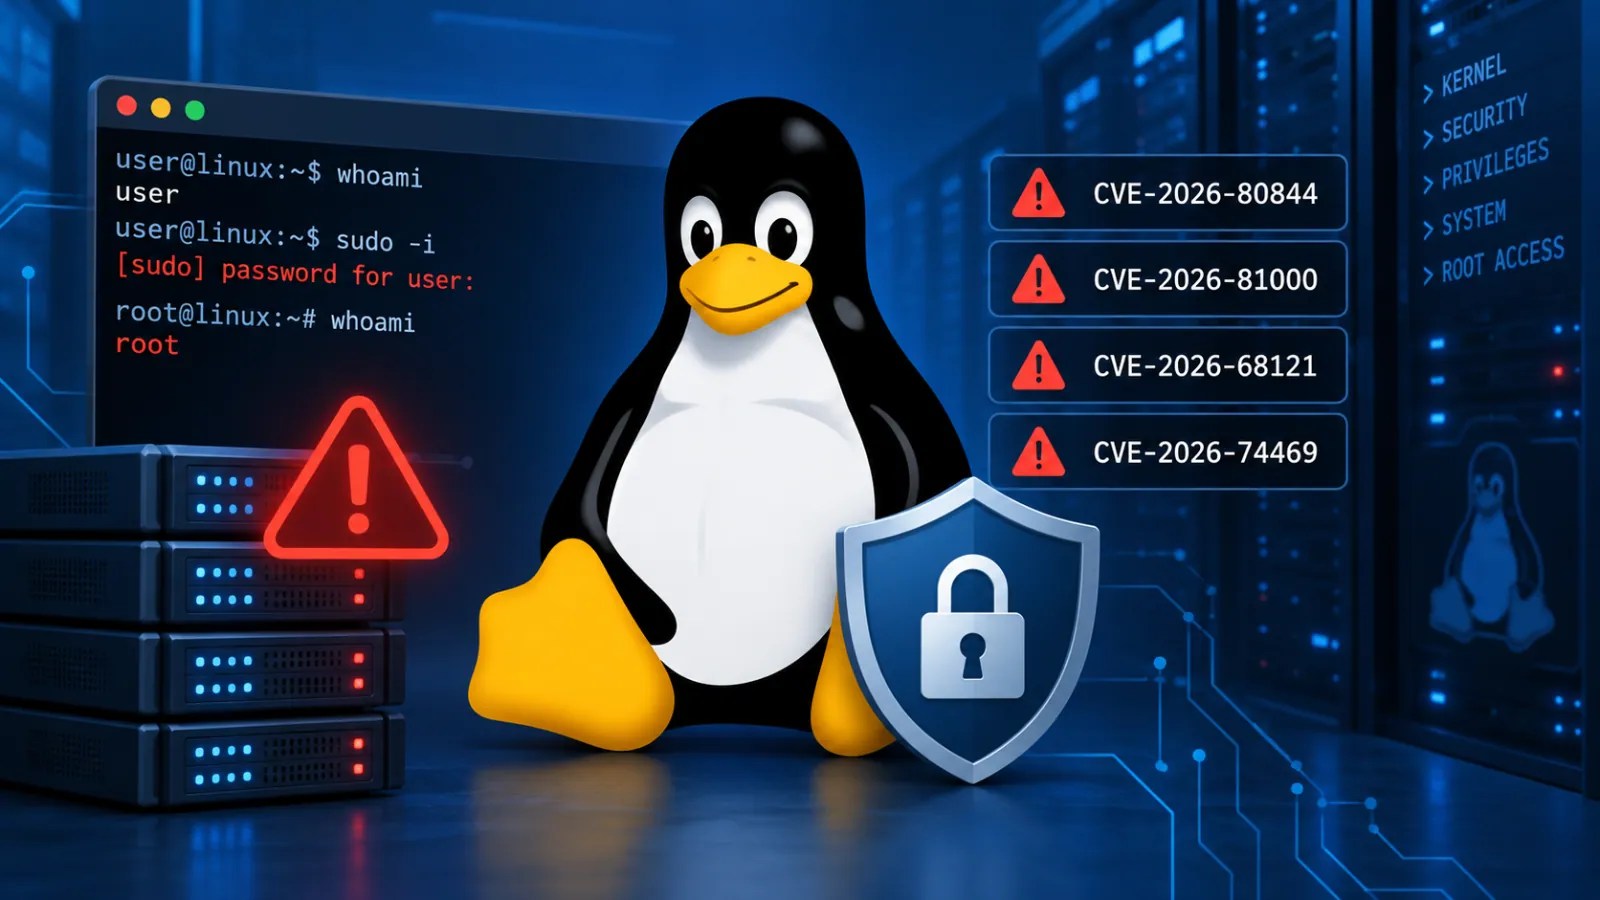
The vulnerabilities, labeled DirtyAH6, TUNderflow, PPPoEject, and DiagSpill, are associated with CVE identifiers CVE-2026-80844, CVE-2026-81000, CVE-2026-68121, and CVE-2026-74469. These issues target various aspects of the Linux networking code, where improper handling of data could lead to memory corruption.

DirtyAH6, in particular, affects IPv6 Authentication Header processing within the IPsec/XFRM code. The flaw arises when malformed IPv6 routing headers are processed without adequate validation, potentially leading to out-of-bounds memory operations. This vulnerability primarily concerns local privilege escalation, although remote denial-of-service attacks are possible under specific scenarios.

Impact and Exploitation Challenges

TUNderflow, identified as CVE-2026-81000, is another critical flaw found in the TUN/TAP virtual network-device subsystem. It allows attackers to exploit oversized receive-headroom values, leading to memory allocation errors. Exploiting this vulnerability could result in unauthorized out-of-bounds memory access.

PPPoEject, or CVE-2026-68121, presents a use-after-free issue in the PPP over Ethernet implementation, allowing stale pointers to potentially corrupt memory. DiagSpill, on the other hand, affects SCTP diagnostic reporting, where a counter overflow can lead to memory overwrites.

Mitigation and Recommendations

Researcher Asim Viladi Oglu Manizada brought these issues to the Linux kernel security team, prompting the release of patches through coordinated disclosure. Affected administrators are advised to upgrade to kernel versions 5.10.270, 5.15.221, 6.1.188, 6.6.157, 6.12.109, 6.18.50, and 7.2.4, which contain necessary fixes.

In environments where immediate patching is not feasible, limiting unprivileged user namespaces and disabling unused networking functions could reduce risk. However, these measures might not fully protect against DiagSpill, which requires direct kernel updates for effective mitigation.

As these vulnerabilities underline the ongoing security challenges in Linux environments, timely updates and system audits are crucial to maintaining robust security postures.
Cyber Security News Tags:CVE, Cybersecurity, IT security, Kernel, Linux, Linux security, network security, Networking, patch update, privilege escalation, root access, Security, system administration, system vulnerabilities, Vulnerabilities

Post navigation

Previous Post: AI Agents Lead New Wave of Ransomware Threats
Next Post: Public Exploits for Linux Kernel Flaws Released

Related Posts

Breaking Down Silos Aligning IT and Security Teams Breaking Down Silos Aligning IT and Security Teams Cyber Security News
BreachLock and Vanta Bridge the Gap Between Continuous Security Testing and Compliance with New Integration BreachLock and Vanta Bridge the Gap Between Continuous Security Testing and Compliance with New Integration Cyber Security News
Exploiting WSUS Servers: A New Malware Threat Exploiting WSUS Servers: A New Malware Threat Cyber Security News
Mac Users Targeted by Fake CAPTCHA for Data Theft Mac Users Targeted by Fake CAPTCHA for Data Theft Cyber Security News
How SOCs Triage Incidents in Seconds with Threat Intelligence How SOCs Triage Incidents in Seconds with Threat Intelligence Cyber Security News
GitHub RCE Flaw Threatens Server Security GitHub RCE Flaw Threatens Server Security Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Hackers Exploit ChatGPT Alerts for Credential Theft
  • Public Exploits for Linux Kernel Flaws Released
  • Linux Kernel Vulnerabilities Pose Root Access Risks
  • AI Agents Lead New Wave of Ransomware Threats
  • Security Flaw in AI Coding Agents Allows Malicious Plugin Swaps

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Hackers Exploit ChatGPT Alerts for Credential Theft
  • Public Exploits for Linux Kernel Flaws Released
  • Linux Kernel Vulnerabilities Pose Root Access Risks
  • AI Agents Lead New Wave of Ransomware Threats
  • Security Flaw in AI Coding Agents Allows Malicious Plugin Swaps

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark