Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
CISA Alerts on Linux Kernel Flaws Under Active Attack

CISA Alerts on Linux Kernel Flaws Under Active Attack

Posted on September 19, 2026 By CWS

The Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning concerning the active exploitation of three vulnerabilities within the Linux kernel. This alert necessitates immediate patching and investigation by affected organizations, as highlighted in their recent advisory.

Details of the Exploited Vulnerabilities

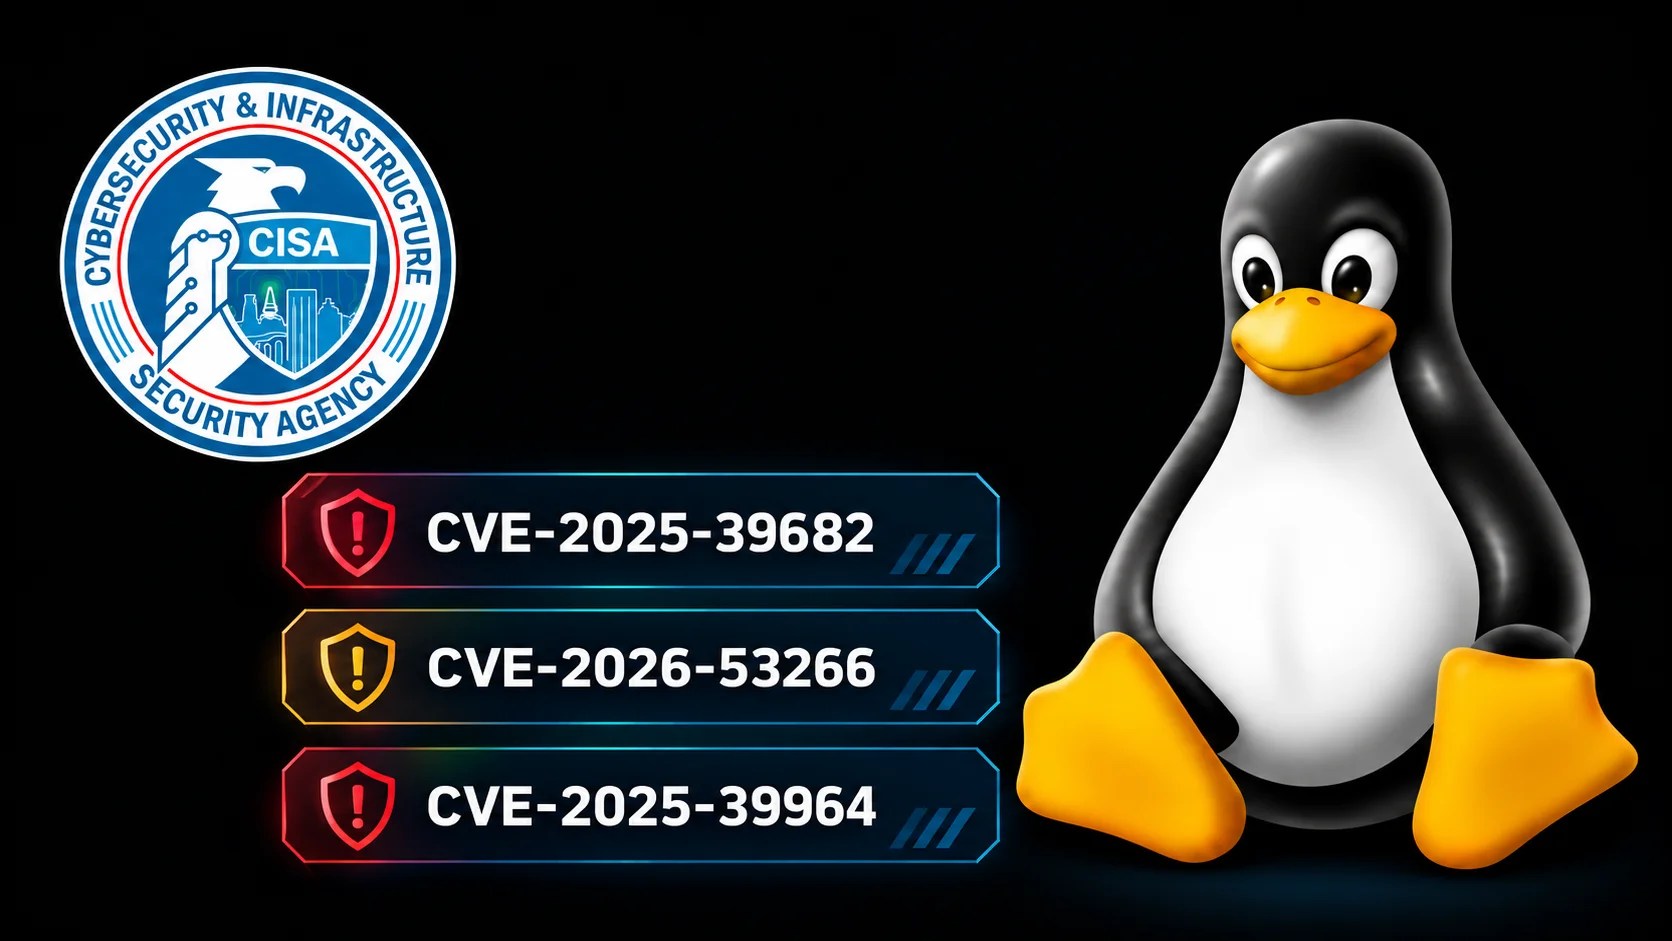
On September 18, 2026, CISA updated its Known Exploited Vulnerabilities (KEV) catalog to include CVE-2025-39682, CVE-2026-53266, and CVE-2025-39964, setting a remediation deadline of September 21 under Binding Operational Directive 26-04. This directive aims to enforce timely fixes based on operational risk assessments, particularly for federal civilian agencies.

The agency emphasized the necessity of forensic triage for these vulnerabilities, urging organizations to investigate any signs of compromise rather than solely relying on patch installation. This approach helps in identifying any potential breaches that might have occurred before patch deployment.

In-depth Analysis of the Vulnerabilities

The most critical of these issues, CVE-2025-39682, involves an improper-condition check in the Transport Layer Security (TLS) receive path of the Linux kernel. With a CVSS score of 9.8, this flaw can lead to incorrect processing of TLS records, potentially affecting systems with kernel TLS (kTLS) enabled. Red Hat has noted that this vulnerability could allow remote exploitation, particularly in internet-facing services utilizing kTLS.

Another significant flaw, CVE-2026-53266, is a high-severity out-of-bounds write issue associated with the netfilter bridge ebtables SNAT target, carrying a CVSS score of 8.8. It risks memory corruption and possible privilege escalation if exploited by local attackers, especially in systems with certain netfilter rules.

The third vulnerability, CVE-2025-39964, pertains to a race condition within the kernel’s AF_ALG cryptographic interface. With a CVSS score of 7.8, this flaw can lead to inconsistent internal states, posing risks to confidentiality and integrity through local, low-privilege attack vectors.

Recommended Actions and Future Outlook

While specific attackers and techniques remain unidentified, the inclusion of these vulnerabilities in the KEV catalog confirms their exploitation in the wild. CISA advises organizations to apply vendor-provided kernel updates promptly, ensuring systems reboot into the updated kernel versions. In cases where patches are unavailable, organizations should consider implementing vendor-recommended mitigations or discontinuing unsupported products.

Temporary measures, such as disabling unused kTLS functionality or adjusting netfilter rules, may offer interim protection. Organizations are also encouraged to preserve relevant telemetry and conduct thorough inspections of systems for any anomalies that may indicate past compromises.

As the September 21 deadline approaches, a combination of rapid patching and comprehensive forensic assessment is crucial in securing vulnerable Linux systems. Failure to address these threats could lead to significant security breaches, underscoring the importance of proactive cybersecurity measures.

Cyber Security News Tags:AF_ALG, CISA, CVE, Cybersecurity, forensic analysis, IT security, Linux kernel, netfilter, network security, Patching, risk management, system updates, TLS, Vulnerabilities

Post navigation

Previous Post: TigerByte Cyber Launches with $3M Funding to Enhance Security
Next Post: AI Security Breach: Hugging Face Incident Analysis

Related Posts

Chinese Hacker Linked to Cyber Espionage Extradited to U.S. Chinese Hacker Linked to Cyber Espionage Extradited to U.S. Cyber Security News
Top 10 Best Privileged Access Management (PAM) Tools in 2025 Top 10 Best Privileged Access Management (PAM) Tools in 2025 Cyber Security News
New ModStealer Evade Antivirus Detection to Attack macOS Users and Steal Sensitive Data New ModStealer Evade Antivirus Detection to Attack macOS Users and Steal Sensitive Data Cyber Security News
‘SyncFuture’ Campaign Weaponizing Legitimate Enterprise Security Software to Deploy Malware ‘SyncFuture’ Campaign Weaponizing Legitimate Enterprise Security Software to Deploy Malware Cyber Security News
Kiteworks Advises Server Shutdown Amid Threat Intelligence Kiteworks Advises Server Shutdown Amid Threat Intelligence Cyber Security News
Multiple GitLab Vulnerabilities Enables Account Takeover and Stored XSS Exploitation Multiple GitLab Vulnerabilities Enables Account Takeover and Stored XSS Exploitation Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Google Fixes 200+ Android Security Flaws, Including Zero-Click Risks
  • Chrome 157 Enhances Security with 213 Fixes
  • Rails Security Flaw Exposes Servers via ImageMagick Uploads
  • XLoader Malware Exploits Business Emails to Steal Data
  • OpsShield Faces cPGuard Supply Chain Cyberattack

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Google Fixes 200+ Android Security Flaws, Including Zero-Click Risks
  • Chrome 157 Enhances Security with 213 Fixes
  • Rails Security Flaw Exposes Servers via ImageMagick Uploads
  • XLoader Malware Exploits Business Emails to Steal Data
  • OpsShield Faces cPGuard Supply Chain Cyberattack

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark