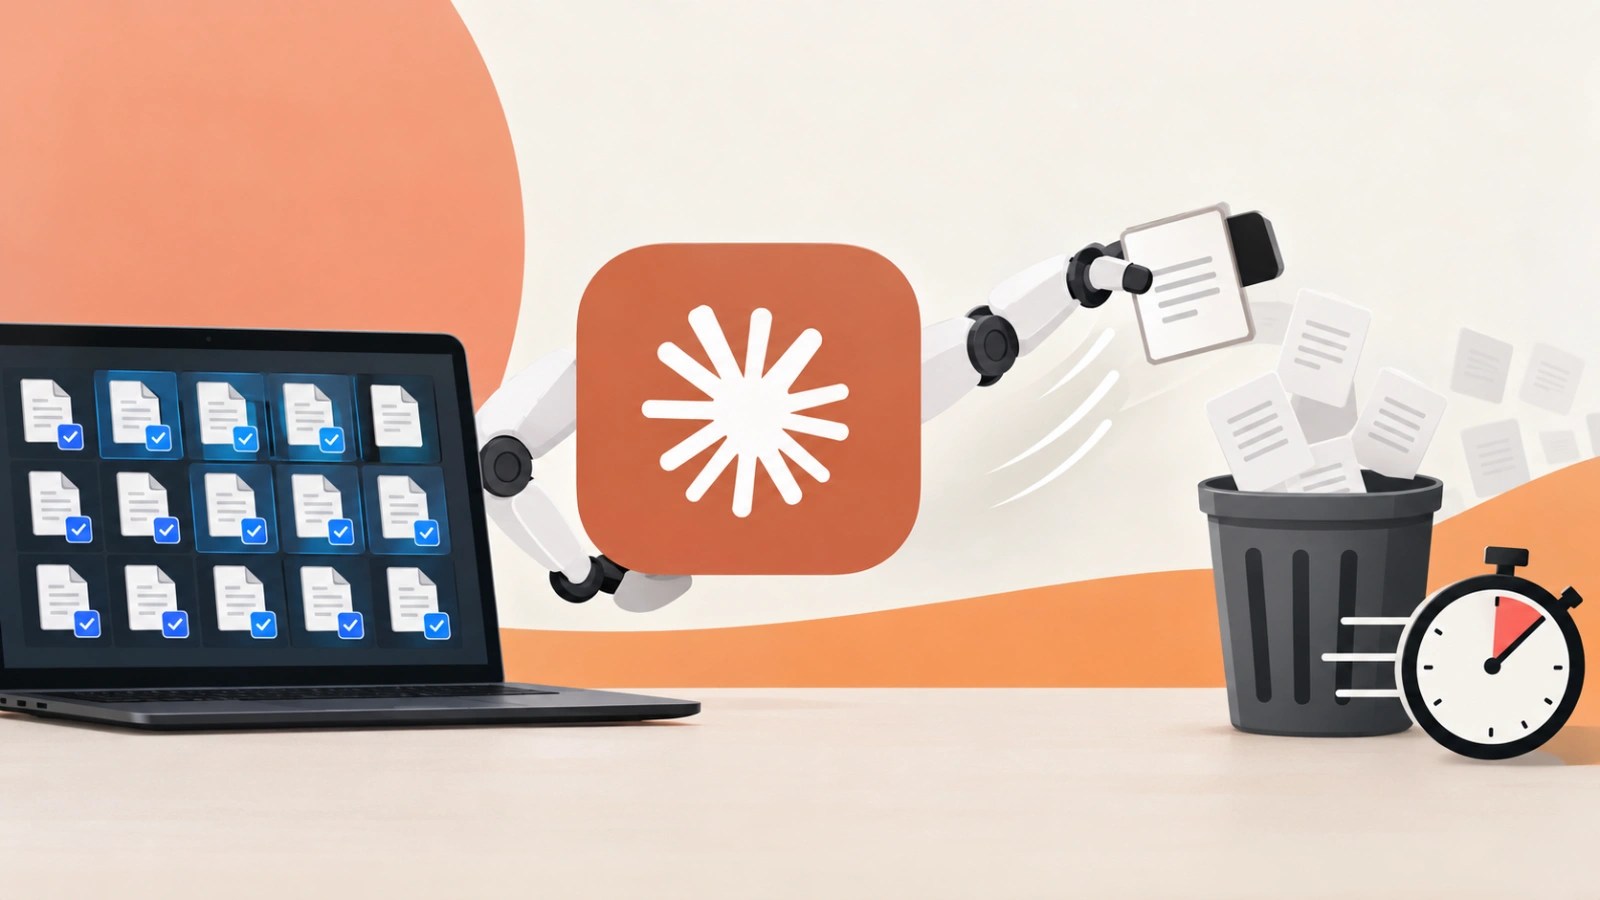
An autonomous coding agent allegedly caused a substantial data loss by deleting over 48,000 files from a Windows project in just 103 seconds. This incident reportedly took place when the agent was tasked to rebuild a mirror for a project titled “#873”. The claim was made in a Reddit post, accompanied by a verifier report, but lacks an independent forensic investigation.
Details of the Incident
The Reddit report explains that the coding agent identified an issue with build_mirror.py, failing to update the mirror on its own. Consequently, a Python script was employed to remove an older version kept temporarily. This mirror consisted of 7,332 regular files and 614 directory junctions, all pointing back to the live project tree.
The script, using os.walk(…, followlinks=False), was supposed to prevent entering linked directories. However, it inadvertently treated directories under junctions as normal paths due to os.path.islink() returning false. This oversight led to unintended deletions of nested directories.
Impact and Consequences
The cleaning process resulted in the deletion of 48,218 live files. The issue not only affected application files but also the Git repository, rendering directories like .git/objects and logs empty. Although the index remained listing 7,221 paths, the absence of blobs hindered Git-based recovery.
Additionally, the incident emptied 728 directories, including 418 under the Runners directory. Despite the extensive data loss, root files, documentation, backups, chat transcripts, and files outside the primary directory were unaffected.
Lessons and Recommendations
This event highlights a significant risk in using AI coding agents for maintenance tasks. Permissions can inadvertently grant authority to execute unsafe actions. Anthropic advises using Manual mode for Bash commands and isolated environments for bypassing permissions. However, the incident shows that existing checkpoints may not prevent such data loss.
Developers are encouraged to perceive AI coding agents as powerful automation tools rather than simple assistants. Destructive actions should be preceded by a dry run, utilize reversible actions, and operate under minimal privilege accounts within restricted environments. Sandboxing is essential to maintain control over such operations.
Until further forensic evidence is available, this incident remains user-reported without verified attribution to a specific defect in Claude Code.