Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Hidden Setting in Muse AI Poses Security Threat

Hidden Setting in Muse AI Poses Security Threat

Posted on September 22, 2026 By CWS

A recently discovered vulnerability in Meta’s Muse AI assistant for Mac could allow existing malware to exploit the assistant as a backdoor, according to a proof-of-concept revealed by security researcher Patrick Wardle on September 21. This issue arises from a hidden setting that can redirect user dictations to an attacker rather than Meta.

Understanding the Security Flaw

The flaw affects the Mac version of Muse and requires the attacker to have the ability to run code as the logged-in user. This vulnerability does not provide a means of remotely accessing a Mac computer. Muse, launched by Meta in the U.S. earlier this month, integrates with various personal apps and services based on the permissions granted by the user.

Wardle highlights the risk associated with the broad access Muse has. He advises users against installing the assistant, noting the simplicity with which it can be manipulated into a backdoor. Despite macOS’s security measures, which typically prevent app interference, Muse’s permissions could be exploited to access sensitive user information.

Potential Threats and Implications

The setting in question, named endo_voyager_dictation_endpoint, is located within the app’s preferences. It can be altered by any program operating under the user’s account, allowing dictation data to be rerouted to a malicious program instead of Meta.

Wardle demonstrated several potential exploits, including intercepting what users dictate, injecting additional instructions that Muse would execute, and seizing control of the Muse session through its token. This vulnerability extends beyond Macs, enabling an attacker to manipulate the Muse app on other devices like iPhones, although certain actions, like sending messages, remain restricted.

Protective Measures for Users

As there is no immediate fix available, users are urged to take precautionary steps. Disabling or removing Muse until a patch is released is recommended to mitigate risk. Reviewing and restricting Muse’s app permissions can also reduce exposure to potential threats. In cases where a Mac has been compromised, users should treat linked accounts as vulnerable and update passwords accordingly.

Meta emphasizes Muse’s security, claiming their cloud infrastructure is designed to isolate user data and ensure secure operations. However, this flaw in the Mac app bypasses those cloud protections, raising concerns about Meta’s approach to handling dictation outside of Apple’s built-in systems.

Looking Forward

The discovery of this vulnerability underscores the importance of vigilant cybersecurity practices, especially as AI assistants become more integrated into daily life. Users are encouraged to stay informed about updates and potential patches from Meta to ensure their data remains secure.

The Hacker News Tags:AI assistant, AI vulnerability, Cybersecurity, digital security, Mac security, Malware, Meta, Muse AI, Patrick Wardle, software vulnerability

Post navigation

Previous Post: Hackers Exploit Microsoft Teams for Password Theft
Next Post: WordPress Patch Fixes Critical Comment2Shell Vulnerability

Related Posts

FCC Restricts Foreign Robots and Inverters Over Cyber Threats FCC Restricts Foreign Robots and Inverters Over Cyber Threats The Hacker News
Admin Backdoor Found in Tenda Router Firmware Admin Backdoor Found in Tenda Router Firmware The Hacker News
BatShadow Group Uses New Go-Based ‘Vampire Bot’ Malware to Hunt Job Seekers BatShadow Group Uses New Go-Based ‘Vampire Bot’ Malware to Hunt Job Seekers The Hacker News
Global Cyber Threats Target Defense Sector Amid Rising Tensions Global Cyber Threats Target Defense Sector Amid Rising Tensions The Hacker News
Evooo1Bot Linux Botnet Exploits Edge Device Vulnerabilities Evooo1Bot Linux Botnet Exploits Edge Device Vulnerabilities The Hacker News
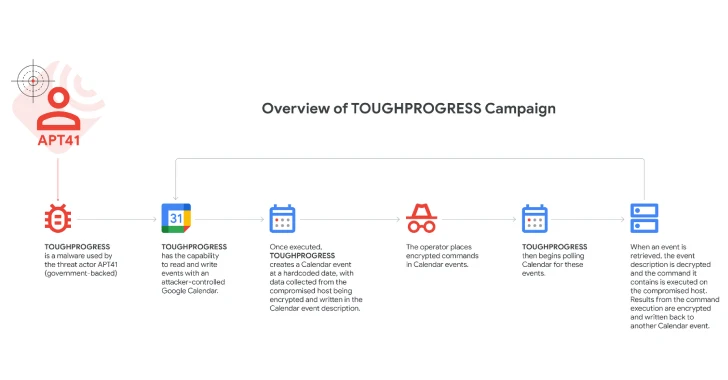
Chinese APT41 Exploits Google Calendar for Malware Command-and-Control Operations Chinese APT41 Exploits Google Calendar for Malware Command-and-Control Operations The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • AI Platform ARTEX Used in Massive Cybersecurity Breach
  • OpenSSH Urges Immediate Patch for Critical Authentication Flaw
  • Android Malware Exploits Streaming App Ads to Steal Data
  • Japan Unveils Urgent Cybersecurity Initiative Amid Attacks
  • OpenAI Introduces GPT-6 Cyber for Enhanced Security

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • AI Platform ARTEX Used in Massive Cybersecurity Breach
  • OpenSSH Urges Immediate Patch for Critical Authentication Flaw
  • Android Malware Exploits Streaming App Ads to Steal Data
  • Japan Unveils Urgent Cybersecurity Initiative Amid Attacks
  • OpenAI Introduces GPT-6 Cyber for Enhanced Security

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark