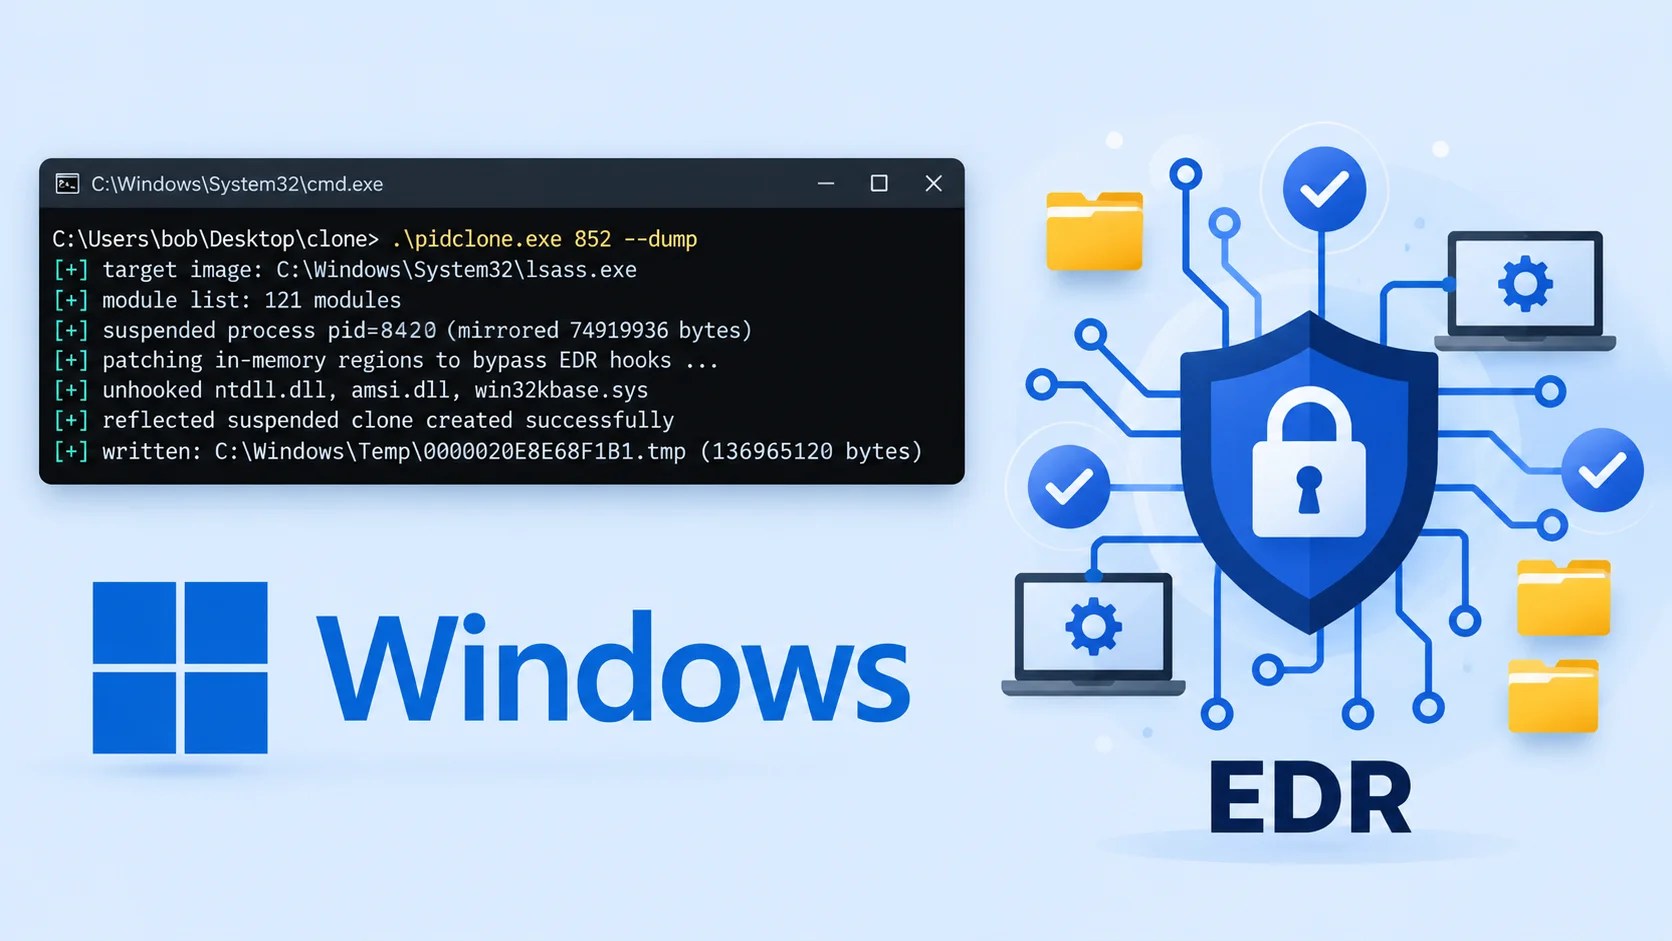
An uncensored artificial intelligence model, hosted locally, has successfully altered a Windows credential-dumping tool to bypass two Endpoint Detection and Response (EDR) systems. This breakthrough, conducted in a controlled lab environment, underscores the potential for generative AI to fast-track the development of custom offensive tools.
Research Insights from Project Black
Project Black’s researcher, Eddie Zhang, shared insights about the experiment, which focused on the Local Security Authority Subsystem Service (LSASS). This service’s memory can contain valuable authentication information, which attackers could exploit for lateral movement after gaining administrative access.
The project set out to determine whether AI could autonomously create an executable to dump LSASS memory without being detected by modern EDR solutions. This task is critical since LSASS memory dumping is classified under MITRE ATT&CK as T1003.001, a Credential Access sub-technique. This capability allows users with administrative or SYSTEM access to extract credentials from LSASS memory for further authentication.
Challenges and Breakthroughs
Initial attempts to generate the dumper using Claude Opus 5, Opus 4.8, and Sonnet 5 were unsuccessful, even though Zhang had approval under Anthropic’s Cyber Verification Program. These models refused to produce the desired output.
Subsequently, Zhang turned to the open-weight DeepSeek v4 Flash 0731 model. After several prompt iterations, DeepSeek created a working executable that accepted a process identifier, cloned the target process through reflection, and generated an encrypted minidump. However, the executable still triggered EDR detection initially, leading to further refinement efforts.
Refinements and Implications
To enhance stealth, Zhang used an uncensored, community-modified Qwen 3.8 27B model on a local password-cracking setup with Nvidia RTX 4090 graphics cards. With minimal input to make the executable “more stealthy,” the model produced a version that evaded detection by both EDR platforms tested.
The revisions included changes to process-spawning behavior, access mask requests, randomization of delays, and modifications to output filenames and paths. These adjustments are crucial as they disrupt the patterns typically monitored by defenses to detect suspicious activities.
Though the findings are significant, they are limited in scope. The names of the EDR vendors were not disclosed, and the configurations were not detailed, meaning the results are not universally applicable. Yet, it demonstrates how local AI models can refine offensive code without external dependencies, reducing the expertise required to create environment-specific variants.
Defensive Measures and Recommendations
Security experts recommend viewing EDR as part of a multi-layered defense strategy rather than a standalone solution. Microsoft advises enabling LSASS credential-stealing Attack Surface Reduction rules with tamper protection, running LSASS as a Protected Process Light, and utilizing Credential Guard. Organizations should also restrict RDP administration, disable WDigest caching, and monitor for unusual LSASS access to quickly isolate potential threats.
Ultimately, minimizing local administrator rights and segregating privileged accounts are key strategies to bolster security defenses against credential dumping threats.